Every policy current, approved, and actually in use
When a procedure changes, nobody should work from last quarter’s copy. One library, one approval path, and a record of who has the current version.
Trusted by 1500+ enterprises
-
1,500+
Clienti in 48 paesi
-
50%+
Tra i clienti della classifica Fortune 500
-
65%
Delle organizzazioni che dedicano maggiore impegno alla quantificazione
-
15,000+
Membri della comunità di rischio Archer
Close the distance between the approved policy and daily practice
A regulation shifts and forty documents need revision. Your reviewers work the same draft, the workflow you defined carries each one to publish, and the teams who follow those procedures get the current version.
-
One published version, always the current one
-
A record of who has the current version
-
Approvals attached, dated, and exportable
How a policy travels from first draft to the people who follow it
Document Governance spans the complete lifecycle from drafting through attestation.
Governed, not just stored
Drafting, review, and approval all happen inside the record, so the document you publish carries its own workflow, permissions, and full history with it.
Everyone knows the change
Attestation tracking shows which people received a published change, so a procedure update reaches the floor instead of resting in a folder nobody opens.
Linked to your controls
Template metadata maps to fields in your Archer instance, so a published policy links to the obligations and controls it governs instead of standing on its own.
Everything that keeps the policy program running once it is live
Complete toolkit for authoring, governance, and distribution.
1
Reusable document templates
You build a template once with its metadata fields, workflow, and body structure, so a new procedure starts in the right shape and your library stays consistent.
2
Configurable workflows
You define the review stages between drafting and publishing, so the approval path matches how your organization actually signs off rather than a fixed model.
3
Co-editing on one version
Your reviewers edit the same draft at once and see each other’s cursors, while the version your organization currently follows stays untouched until you publish.
4
Redlines and diff stepper
Reviewers see additions in green and removals in red, and the stepper walks them through every change, so approval rests on what moved instead of a full reread.
5
Permissions built by role
You give owners, delegates, contributors, and readers access at the document, version, or draft level, so the right people edit and everyone else still reads.
6
Tags for your taxonomy
You tag published documents by department, document type, or business line, so a compliance officer filters to the twelve policies that matter and skips the rest.
What you get with Document Governance
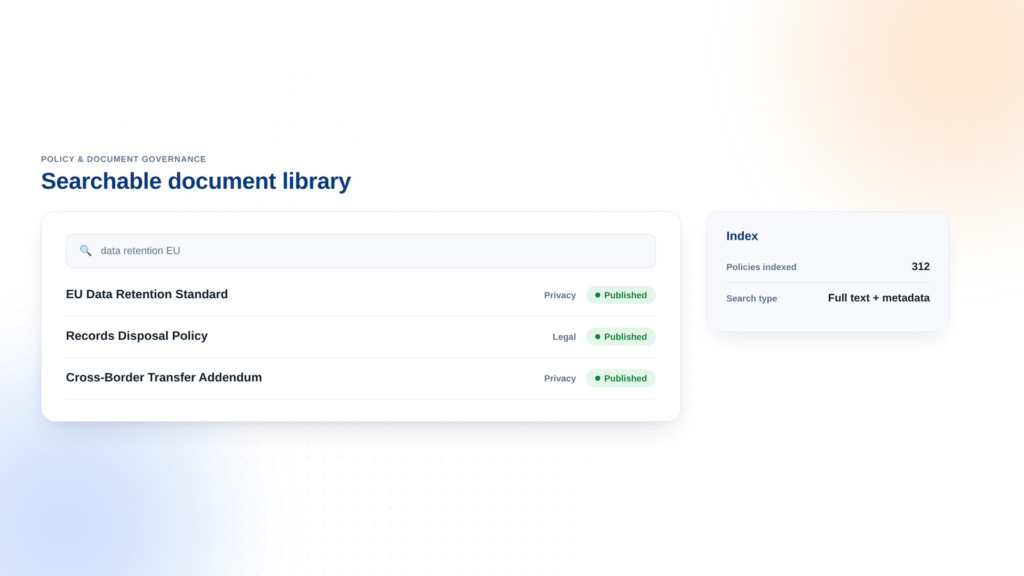
Searchable document library
Full text search across every published document.
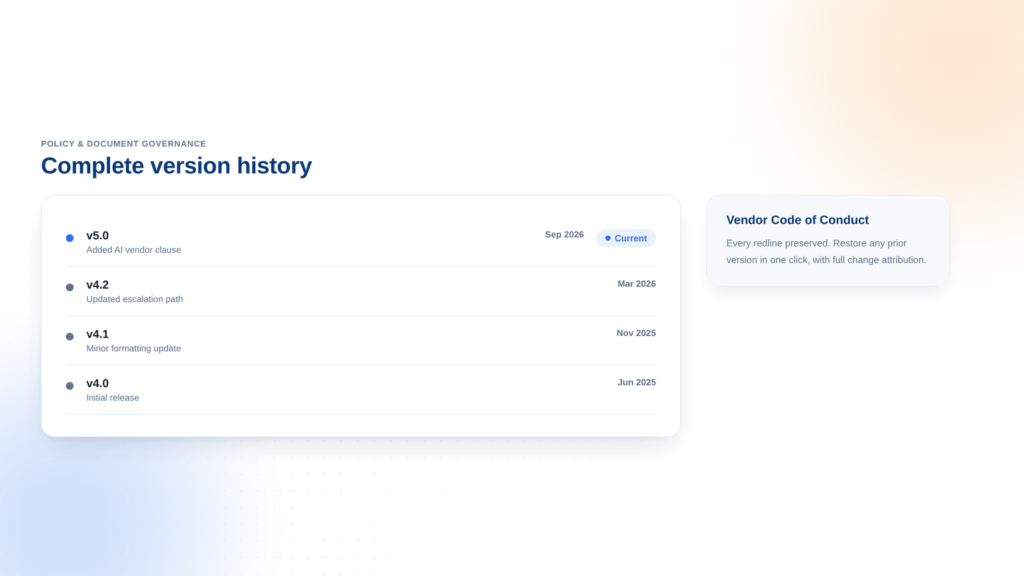
Complete version history
Every prior version kept with its approvals.
Configurable approval workflow
Review stages matching how your teams approve.
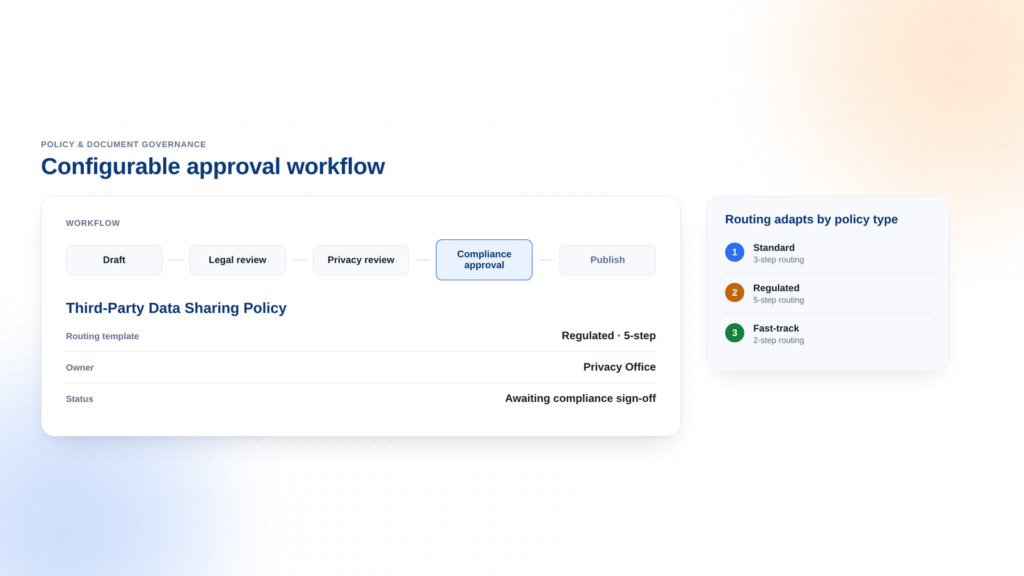
Le immagini riportate sopra non sono screenshot reali del prodotto.
Policy governance across every scenario
Document Governance handles the complete policy lifecycle in every context.
-
Enterprise policies
Every policy sits in one searchable library, drafted by the people who own it and approved through the path you defined. The published version is the one anyone can act on, and each prior version stays on file with its approvals attached.
-
Operating procedures
The procedure your operations team follows updates on the same controlled path as your policies, and the template holds its structure. Attestation tracking shows who received the change, so a process update reaches the floor and not a folder.
-
Regulatory change response
A rule changes and twenty procedures need revision. You open a new version of each, reviewers work in parallel, and the workflow carries every one to publish. Attestation shows who holds the current copy, and prior versions stay on file.
-
Reportistica pronta per il consiglio di amministrazione
Genera report per i dirigenti e il consiglio di amministrazione in pochi minuti anziché in giorni.
-
Conformità sicura
Assicuratevi di essere sempre pronti per gli audit in tutti i contesti normativi in cui operate.
-
Si adatta alle tue esigenze
Integra nuove unità, framework e regioni senza dover ricompilare il programma.
How Archer compares to a repository plus a workflow tool
Archer brings approval, distribution, and control linkage into one system.
A repository plus a workflow tool
Separate systems for storage and approvals.
Ecco cosa riceverai
-
File storage
-
Separate approval process
-
Manual distribution tracking
Archer Document Governance
One integrated system for the complete policy lifecycle.
Ecco cosa riceverai
-
One library and one approval path in the same system
-
Attestation tied to the published version
-
Policy linked to the obligations and controls it governs
-
Permissions at the document, version, and draft level
-
One activity log spanning document, version, and draft
-
Redlines and a change stepper inside the approval step
Conformità fai da te
Fogli di calcolo, unità di rete condivise e conoscenze non documentate.
Ecco cosa riceverai
-
Monitoraggio manuale
-
Infrastruttura personalizzata
-
Aggiornamenti personalizzati
Scopri i nostri casi di studio
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
- Visualizza il caso di studio:
- Visualizza il caso di studio: Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
- Visualizza il caso di studio: Intuitive Surgical è passata ad Archer SaaS per intraprendere un percorso verso una gestione del rischio più efficace
- Visualizza il caso di studio: Resilienza operativa per gli istituti di servizi finanziari
Oltre 1.300 organizzazioni utilizzano Archer®, tra cui metà delle aziende della classifica Fortune 500 e 37 delle prime 50 banche mondiali. Scopri quali sfide hanno dovuto affrontare i loro team, cosa hanno realizzato e cosa è cambiato.
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
Intuitive Surgical è passata alla piattaforma SaaS Archer per intraprendere un percorso verso una gestione del rischio più efficace
Resilienza operativa per gli istituti di servizi finanziari
Scelto con fiducia dai team che si assumono il rischio
I responsabili dei settori rischio, conformità e audit raccontano cosa è cambiato dopo l’implementazione di Archer Evolv.
Abbiamo riconosciuto la necessità di una piattaforma software GRC che fosse fondamentale per la nostra capacità di migliorare e trasformare i nostri processi aziendali in materia di rischio e conformità.
Archer è la fonte di verità e ci fornisce un'ottima traccia di audit. In qualità di compagnia assicurativa, siamo sottoposti a verifiche da parte di ogni ente governativo. Ora possiamo dire: “Ecco il nostro archivio, date un’occhiata”.
L'aggregazione dei rischi è un aspetto fondamentale per noi: ci permette di individuare dove si concentrano i rischi all'interno dell'organizzazione e di garantire una maggiore visibilità ai consigli di amministrazione e ai dirigenti.
Turkcell utilizza Archer come principale strumento di GRC all’interno dell’azienda. Ci offre un quadro di governance trasparente e sicuro.
Archer ci offre la possibilità di sintetizzare le cose in cifre e dettagli concreti anziché in generalità. Si tratta di una gestione basata sui fatti anziché sull'intuizione o sulla sensazione.
Mette in comunicazione tutte le diverse applicazioni, consentendoti così di sfruttare tali riferimenti incrociati e collegamenti per prendere decisioni aziendali più efficaci, poiché hai tutto a portata di mano in un unico posto.
Frequently asked questions
Answers to what policy owners and compliance leaders ask before adopting Document Governance.
You do not rebuild the library by hand. Bring your existing documents into templates that match how you already write policy, publish them through the workflow you define, and version history runs from that point forward.
Yes. Reviewers edit the same draft at the same time and see each other’s cursors and highlights as they work. Comments attach to a point or a passage, and redlines mark every addition and removal, so nobody merges competing copies by hand.
The activity log holds every action taken on a document, its versions, and its drafts, and it exports to CSV. You send the record of who drafted, reviewed, approved, and published, plus the version that was in force on the date in question.
Document Governance runs the document itself, from drafting and review through approval, publication, and version history. Policy Program Management runs the program around it, mapping policies to risks and controls. Many teams run both.
Template metadata maps to fields in your Archer instance, so a published policy carries its links to the obligations and controls it governs. A policy owner opens the policy and sees what it covers rather than tracing connections by hand.
Permissions run at the document, version, and draft level. Owners hold full control, delegates act for them, contributors draft with owner approval to merge, and readers see the published version. Only the owner applies tags to published documents.