See risk forming before it becomes loss
Cyber, AI, business interruption, and regulation top this year’s risk list, and each one lives in a different system. Evolv Risk reads them as one.
1,500+ organizations run risk and compliance on Archer · 50% of clients in the Fortune 500
-
1,500+
Clienti in 48 paesi
-
50%+
Tra i clienti della classifica Fortune 500
-
65%
Delle organizzazioni che dedicano maggiore impegno alla quantificazione
-
15,000+
Membri della comunità di rischio Archer
Your register refreshes quarterly. Your exposure does not wait.
The board asks where exposure sits and whether you are ready. That looks forward. Your register, heat map, and quarterly assessment look back. Evolv Risk keeps the picture current, so the answer is ready before the question lands.
-
One risk picture instead of six disconnected ones
-
Exposure that moves when the business moves
-
Every score traced to the source behind it
Built to hold up when the board asks how you know that number
Archer Evolv offre funzionalità di livello aziendale per aziende di ogni dimensione.
An answer you can defend
Every judgment carries its own lineage, so you can open any risk score and follow it back to the document, the version, and the date it came from.
A picture that stays live
Signals from inside the business and outside it feed one view, so a shift in one corner shows up wherever it raises risk instead of sitting in a silo.
Work that lands in Archer
Operators do not stop at a summary. They open the assessment, assign the owner, and update the register in the system your team already works in.
What your team gets on day one, in the order they will use it
Archer Evolv è stato progettato specificamente per soddisfare le esigenze dei team GRC e degli utenti aziendali.
1
Continuous signal intake
Internal loss events, control failures, third party changes, and outside intelligence land in one place as they happen, so no one spends a week chasing what changed.
2
Business impact scoring
Exposure reads in financial terms rather than a color on a grid, so a risk in one business unit compares honestly against a risk in another when funding is short.
3
Confidence-based routing
Every operator scores its own certainty. Calls above the threshold your team sets move through. Calls below it reach a named reviewer before anything changes.
4
Versioned source lineage
Sources, amendments, and reasoning keep their history at the citation level, so a question about how a risk reached the register has an answer already waiting.
5
Two-way Archer integration
Evolv reads and writes to your Archer record, which stays the system of record, so your team stops keying the same finding into two places and nothing drifts apart.
6
Dynamic AI guardrails
Policy documents turn into live guardrails that test and monitor the AI your business is already running, and route what fails into your issue management process.
What Evolv Risk does in the moment
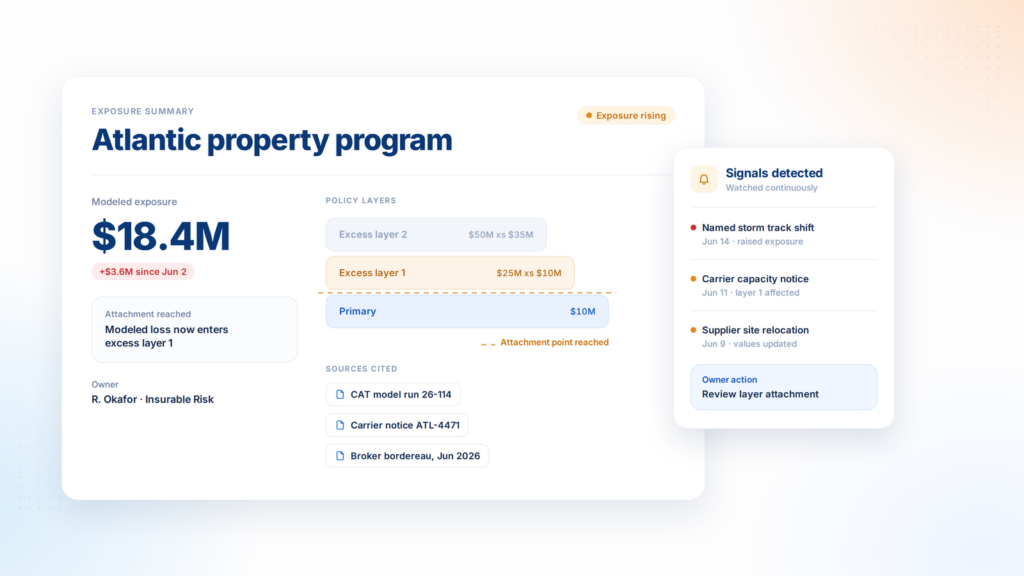
Spot exposure before it lands
A threat in one domain cascades into three others long before anyone reviews it, and the first sign shows up in a system your risk team does not watch. Evolv Risk reads those signals continuously and raises exposure as it forms, while there is room to act.
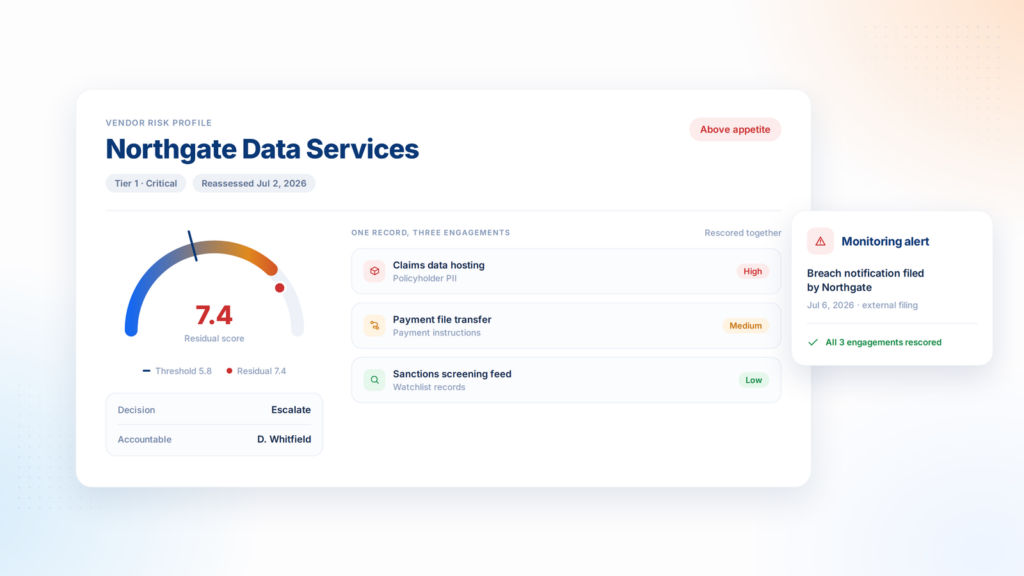
Decide against your appetite
Enterprise risk holds one piece, operational risk another, the business units the rest. Evolv Risk reads every domain from one plane and scores exposure in business terms, so you can weigh a supplier concentration against a control gap and fund the greater.
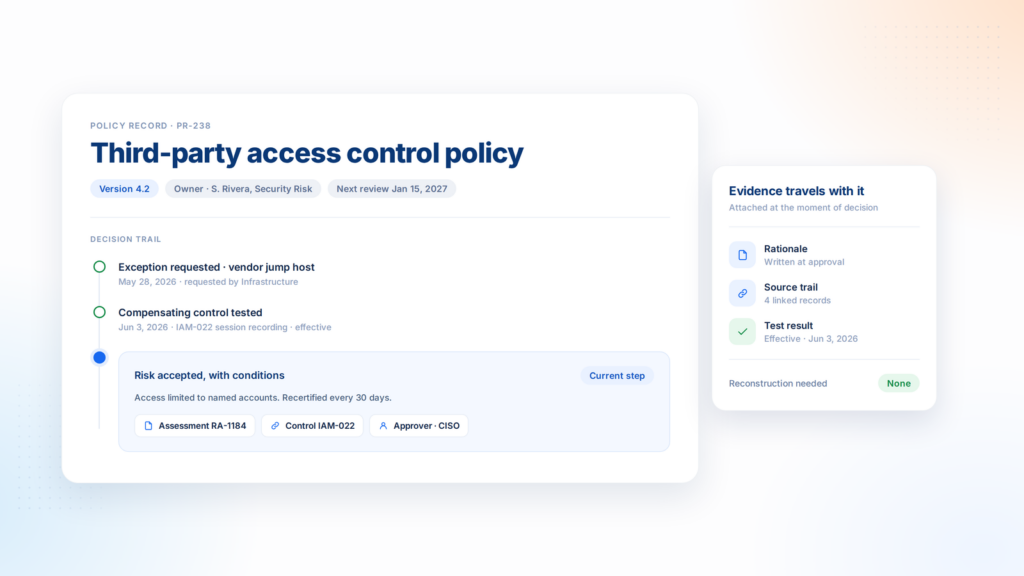
Defend every judgment you make
Regulators now ask you to demonstrate that controls work, not that a policy exists. A register updated twice a year cannot carry that. In Evolv Risk the reasoning and source trail travel with the decision, so the evidence exists when you make the call.
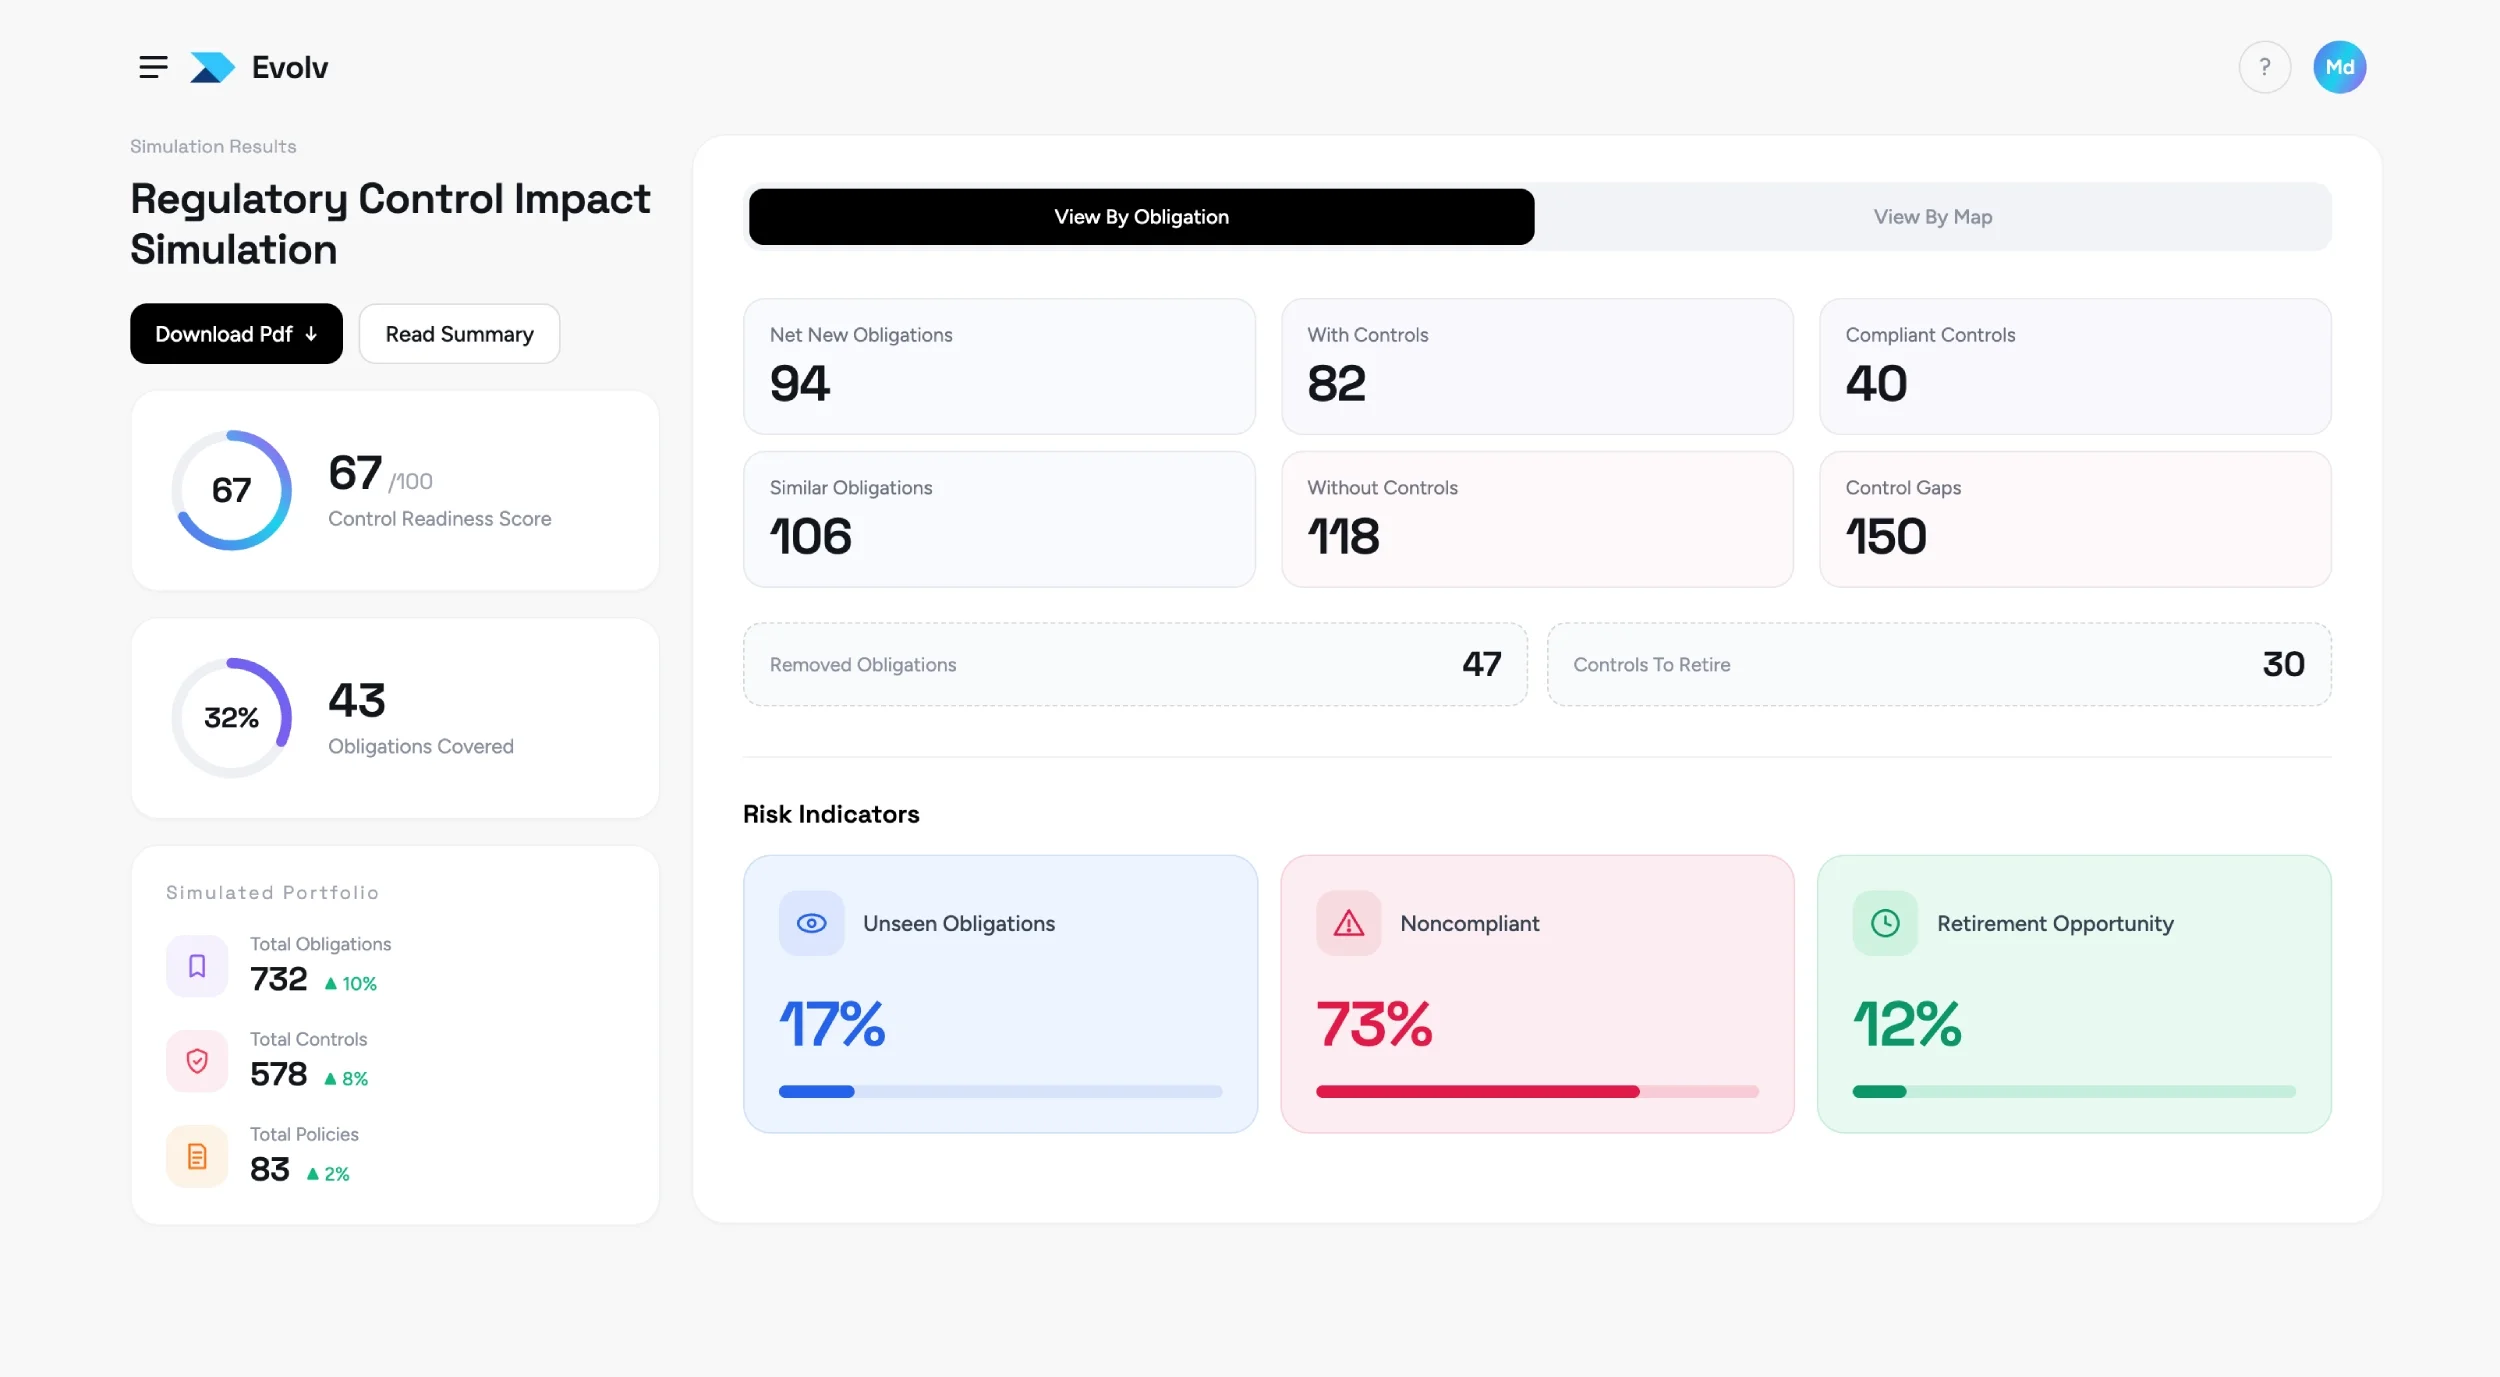
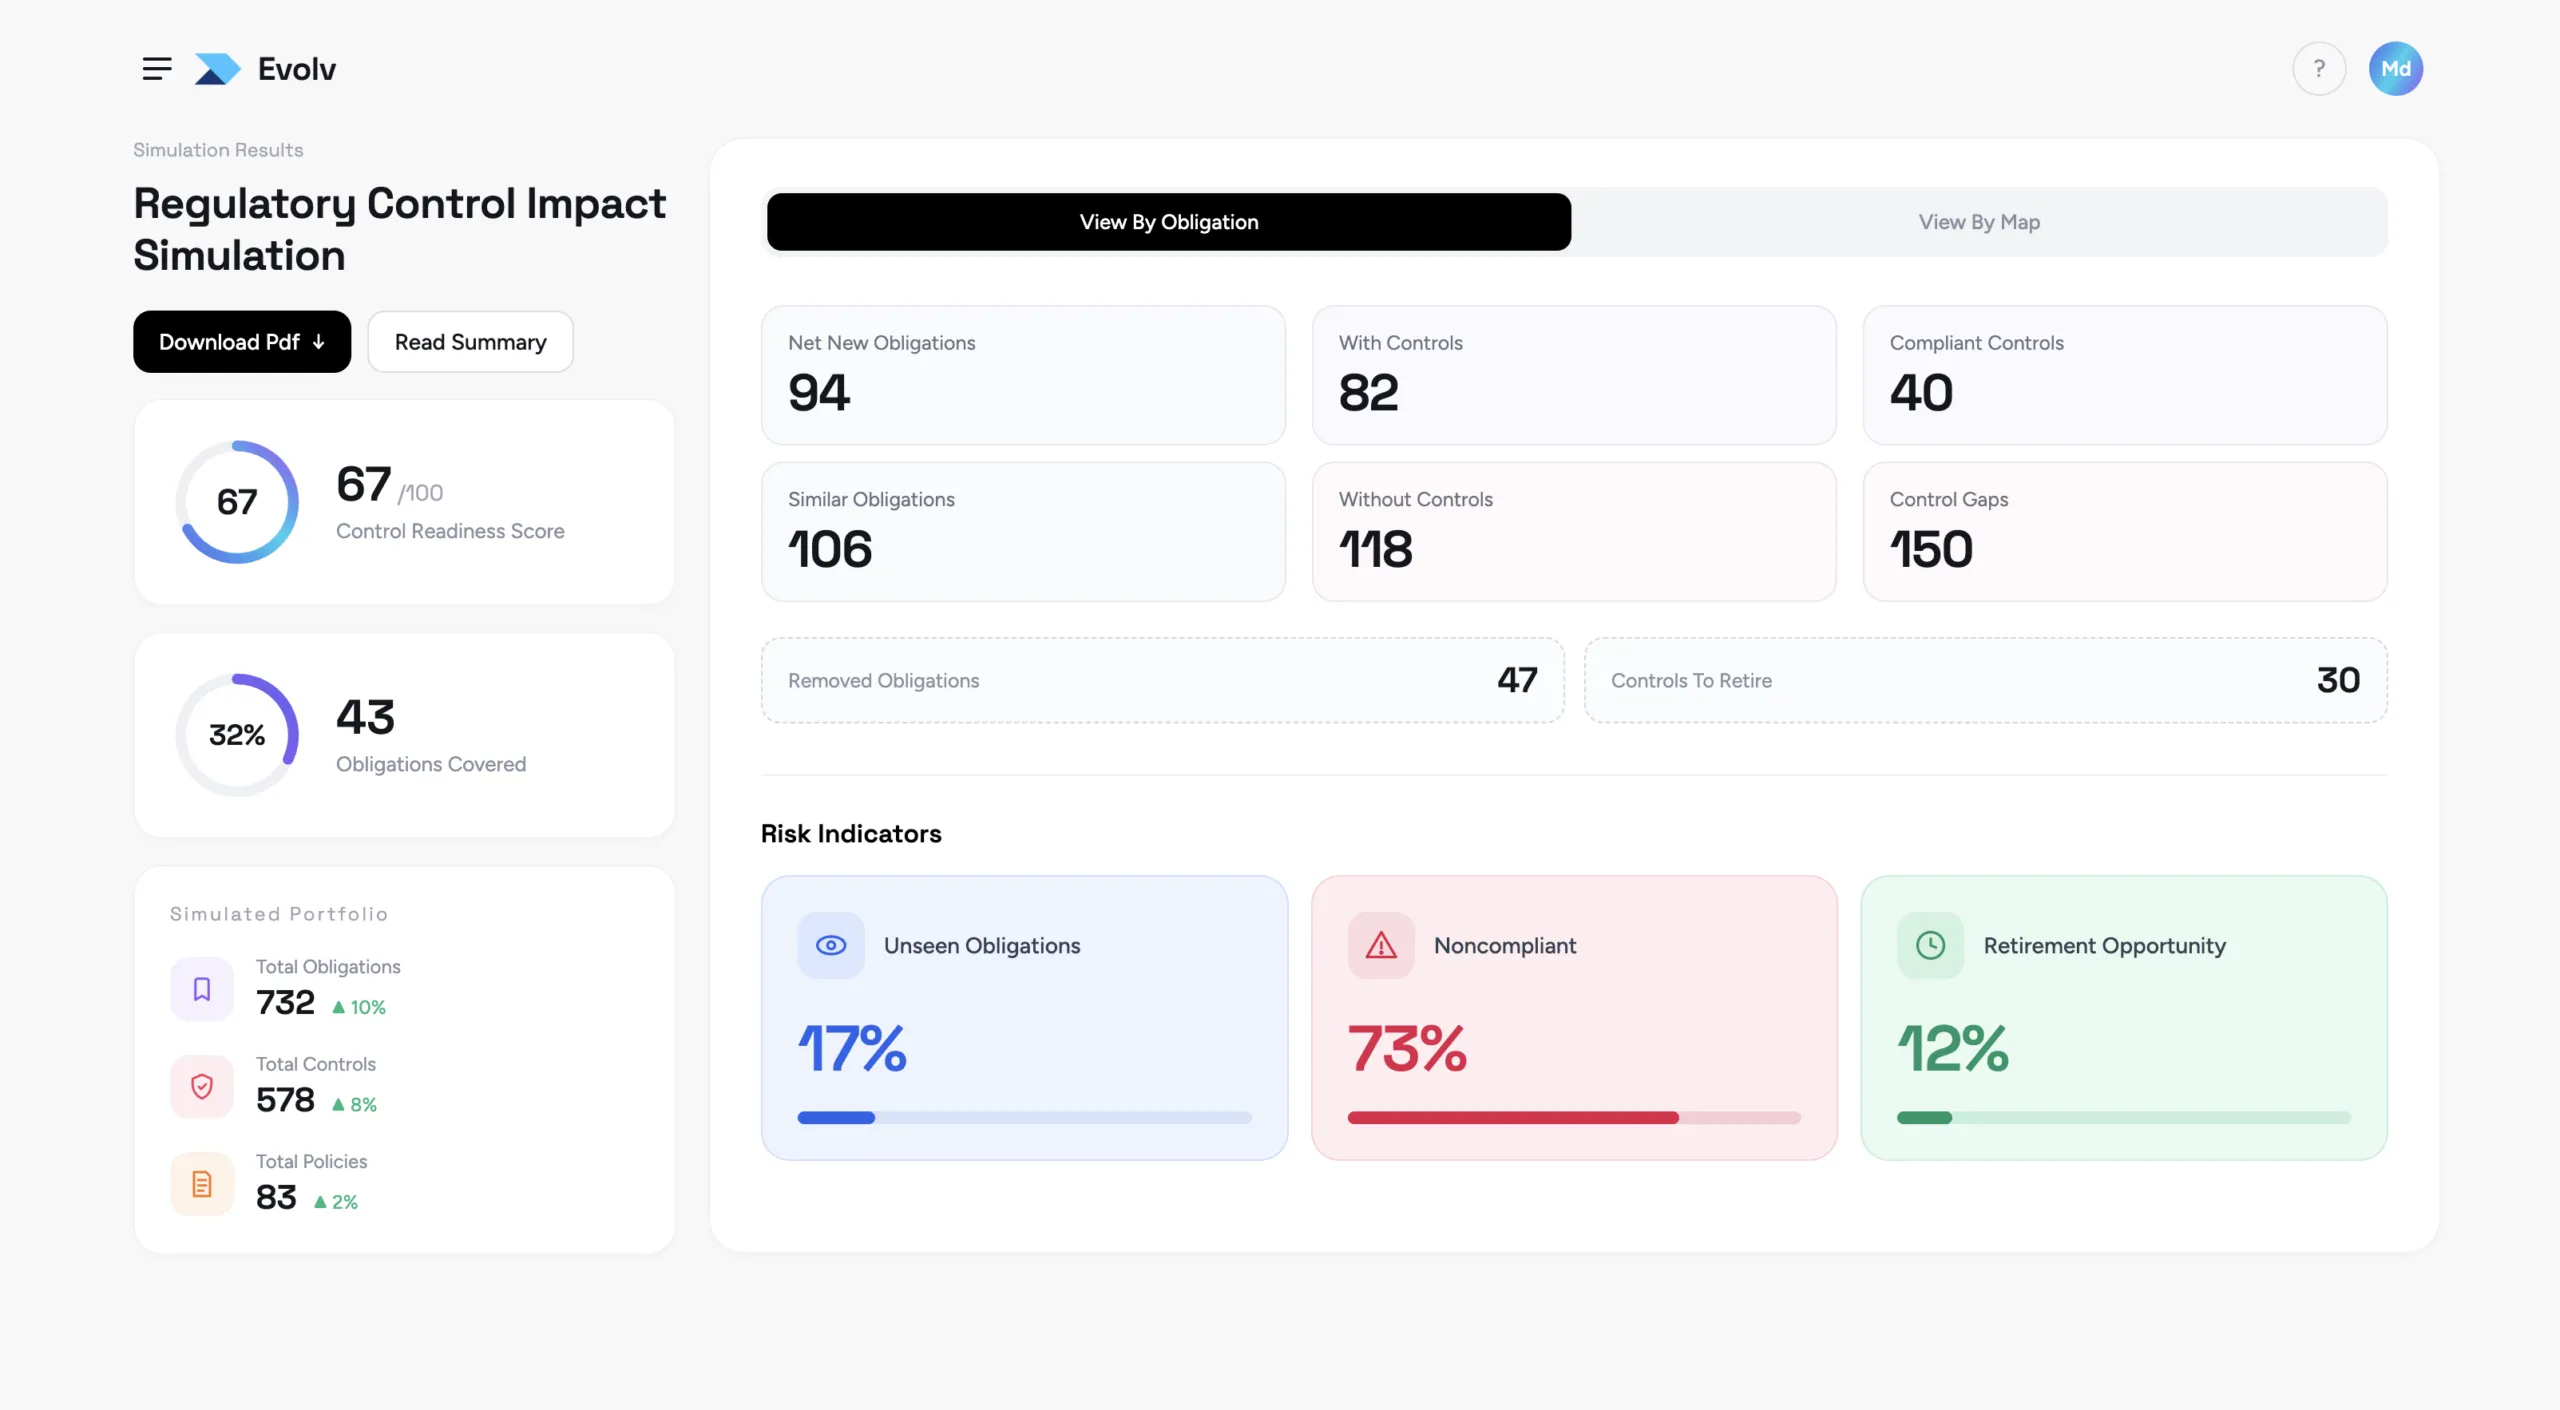
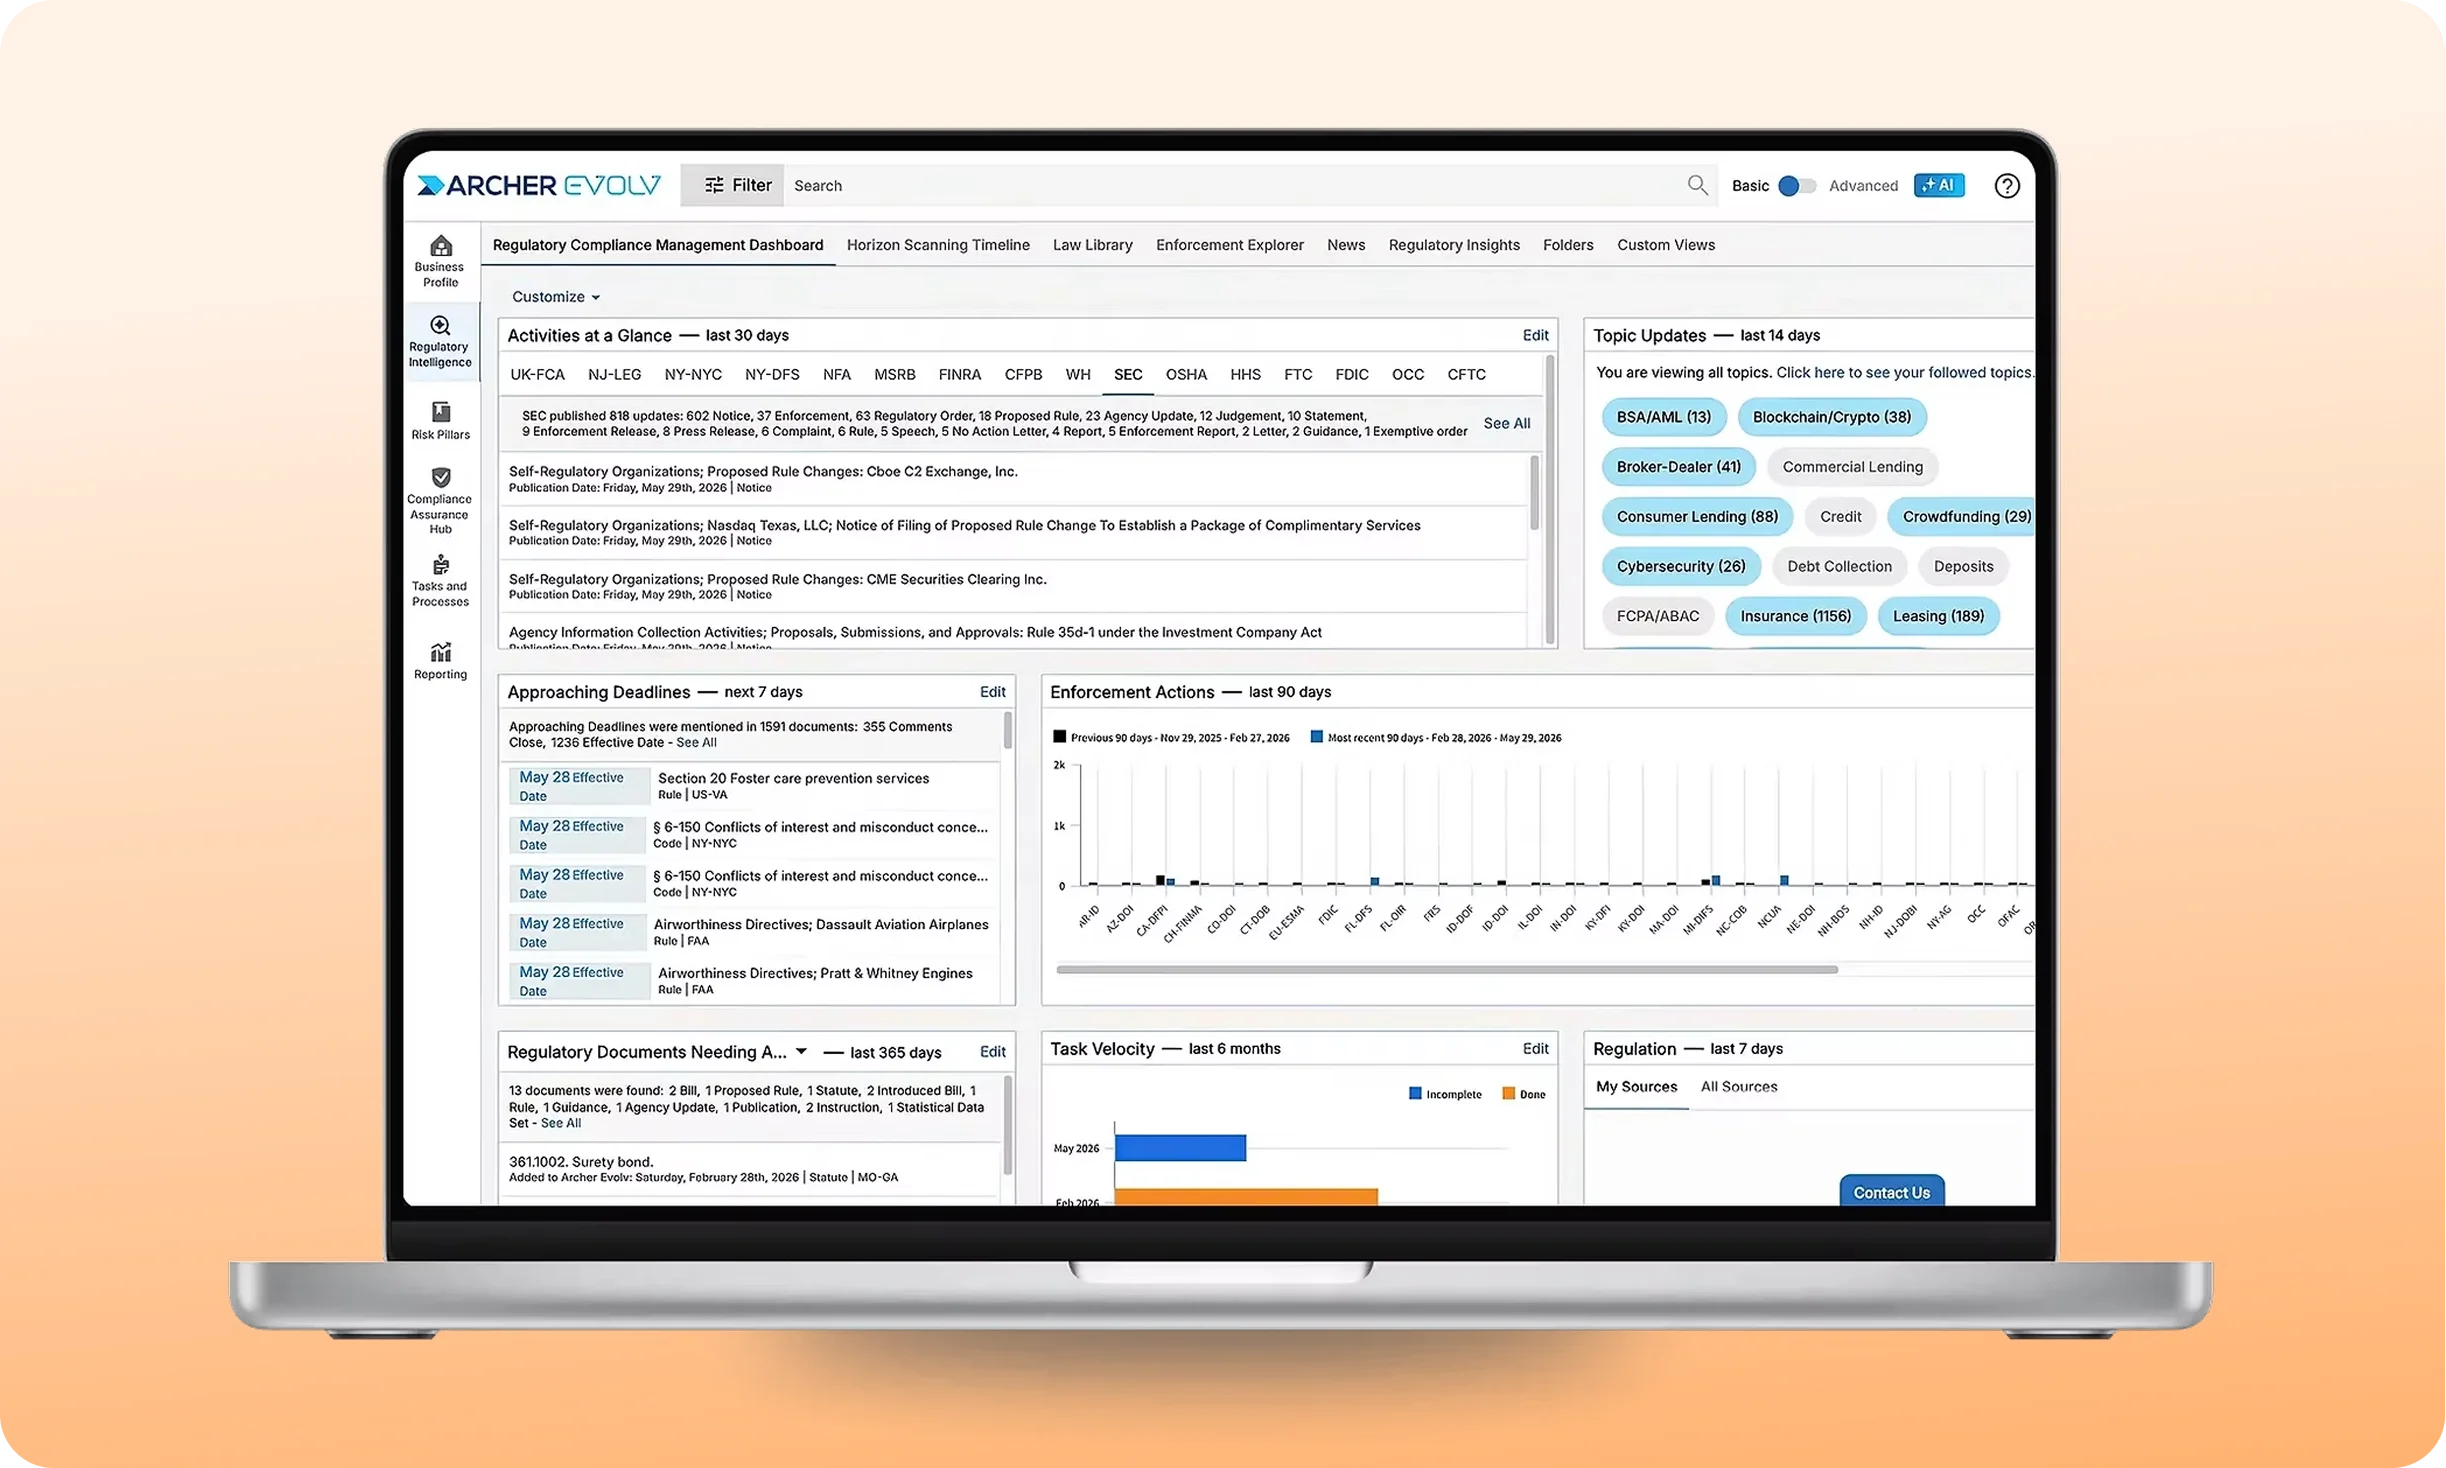
Le immagini riportate sopra non sono screenshot reali del prodotto.
Everything your risk program needs, all of it on one platform
Archer Evolv consente di adottare una strategia integrata per tutte le funzioni relative alla gestione dei rischi e alla conformità.
-
Risk register
One catalog of every risk across the enterprise
-
Control library
Map a control once to every framework it covers
-
Loss event management
Capture incidents, analyze them, tie them to controls
-
Key indicator management
Thresholds that trigger before the exposure arrives
-
Third party exposure
Read supplier risk alongside everything else you carry
-
Rendicontazione al Consiglio di Amministrazione
A current view of exposure, ready when the meeting is
How an Archer Evolv operator differs from a general-purpose AI tool
Scopri come Archer GRC si posiziona rispetto agli strumenti generici e alle soluzioni aziendali personalizzate.
Where the answer comes from
Copertura di base per le squadre alle prime armi.
Ecco cosa riceverai
-
Strutture predefinite
-
Autorizzazioni personalizzate
-
Infrastruttura personalizzata
Archer Evolv Risk
Progettato per i team che necessitano di visibilità e controllo in tempo reale.
Ecco cosa riceverai
-
Modelli di rischio predefiniti
-
Integrazioni native (oltre 200)
-
Raccolta automatizzata delle prove
-
Mappatura dei controlli tra framework
-
Dashboard esecutivi in tempo reale
-
Valutazione del rischio assistita dall'intelligenza artificiale
-
Implementazione SaaS multi-tenant
Handling uncertainty
Fogli di calcolo, unità di rete condivise e conoscenze non documentate.
Ecco cosa riceverai
-
Monitoraggio manuale
-
Infrastruttura personalizzata
-
Aggiornamenti personalizzati
Scopri i nostri casi di studio
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
- Visualizza il caso di studio:
- Visualizza il caso di studio: Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
- Visualizza il caso di studio: Intuitive Surgical è passata ad Archer SaaS per intraprendere un percorso verso una gestione del rischio più efficace
- Visualizza il caso di studio: Resilienza operativa per gli istituti di servizi finanziari
Oltre 1.300 organizzazioni utilizzano Archer®, tra cui metà delle aziende della classifica Fortune 500 e 37 delle prime 50 banche mondiali. Scopri quali sfide hanno dovuto affrontare i loro team, cosa hanno realizzato e cosa è cambiato.
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
Intuitive Surgical è passata alla piattaforma SaaS Archer per intraprendere un percorso verso una gestione del rischio più efficace
Resilienza operativa per gli istituti di servizi finanziari
Scelto con fiducia dai team che si assumono il rischio
I responsabili dei settori rischio, conformità e audit raccontano cosa è cambiato dopo l’implementazione di Archer Evolv.
Abbiamo riconosciuto la necessità di una piattaforma software GRC che fosse fondamentale per la nostra capacità di migliorare e trasformare i nostri processi aziendali in materia di rischio e conformità.
Archer è la fonte di verità e ci fornisce un'ottima traccia di audit. In qualità di compagnia assicurativa, siamo sottoposti a verifiche da parte di ogni ente governativo. Ora possiamo dire: “Ecco il nostro archivio, date un’occhiata”.
L'aggregazione dei rischi è un aspetto fondamentale per noi: ci permette di individuare dove si concentrano i rischi all'interno dell'organizzazione e di garantire una maggiore visibilità ai consigli di amministrazione e ai dirigenti.
Turkcell utilizza Archer come principale strumento di GRC all’interno dell’azienda. Ci offre un quadro di governance trasparente e sicuro.
Archer ci offre la possibilità di sintetizzare le cose in cifre e dettagli concreti anziché in generalità. Si tratta di una gestione basata sui fatti anziché sull'intuizione o sulla sensazione.
Mette in comunicazione tutte le diverse applicazioni, consentendoti così di sfruttare tali riferimenti incrociati e collegamenti per prendere decisioni aziendali più efficaci, poiché hai tutto a portata di mano in un unico posto.
Evolv Risk, answered
Plenty of vendors have one of these. The defensible position is having all three on the same foundation.
An operator works inside your own record, bound to an identity and scoped to what that identity already permits, so it reaches nothing your team has not granted it. It cites what it used, and when it is not certain it routes the call to a reviewer.
No. It protects their time for the judgment only they can make. The operator handles the gathering and the first pass. Your experts own the decision, and every override they make teaches the operator what your organization means by acceptable.
Four domains run in production now: regulatory intelligence, regulatory change management, AI risk, and decision support. Operational risk is next, then IT risk, policy content, and third party. Start with what ships today and add the rest.
No. Archer Evolv runs on the Archer instance you already have, and that is the point. The controls, policies, findings, and workflows your team encoded are what make the AI defensible. Data quality operators improve your data during deployment.
They read from the same plane, so risk and compliance work from one lineage instead of two. A regulatory change that lands in Compliance moves the risk picture in Evolv Risk, because neither has to be told what the other found.