Cyber risk and business risk, finally the same number
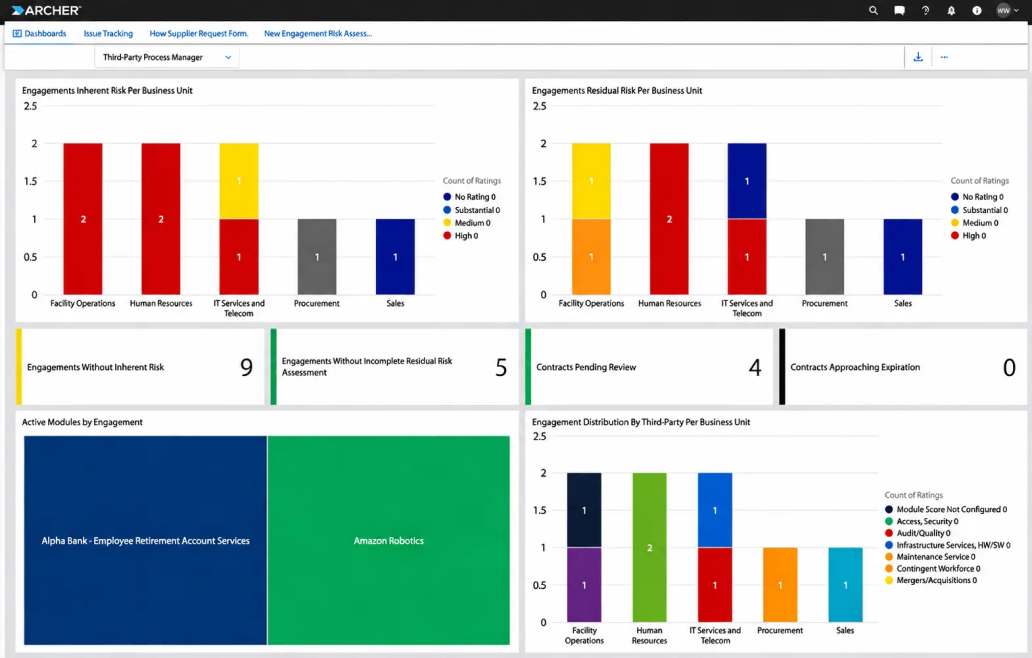
From the analyst closing a finding to the board reading the exposure summary, every role works from the same assets, controls, and risk data.
Trusted by 1,500+ organizations
-
1,500+
Clienti in 48 paesi
-
50%+
Tra i clienti della classifica Fortune 500
-
65%
Delle organizzazioni che dedicano maggiore impegno alla quantificazione
-
15,000+
Membri della comunità di rischio Archer
One set of assets and controls, a view for every role that asks
An analyst assesses a system once. That result reaches the director’s queue, the CISO’s exposure summary, the enterprise register the CRO owns, and the board pack, with no rekeying and no fight over whose spreadsheet is current.
-
Analysts: assess once, and it lands everywhere
-
CISO and CRO: one exposure number, not two
-
Board: an exposure view that survives questions
What the analyst, the CISO, and the board each get
From IT risk analyst to enterprise risk officer, one platform serves every role.
For the IT risk analyst
Archer fits the process your team runs now, so assessments, control tests, and findings sit in one queue instead of four spreadsheets and an inbox.
For the security GRC lead
Roll every system, control, and open finding into one picture of exposure, so you answer the hard question in the meeting instead of rebuilding the deck.
For the CISO and the CRO
Cyber exposure and enterprise risk draw on the same assets, controls, and scenarios, so the two of you bring one number to the executive table.
Where an IT and security risk program actually does the work
Nine interconnected use cases replace spreadsheets with workflows that move findings and controls from assessment through closure.
1
IT risk register
Catalog the organization and its IT assets, then log every IT risk against the systems it touches, so the register reflects the estate you actually run.
2
Control testing
Test IT controls on a project schedule and pull results in from automated systems, so manual evidence and machine evidence land together in the same record.
3
Vulnerability triage
Rank threats and vulnerabilities by what they put at risk in the business, using asset context and scan results to settle which one your team works on first.
4
Incident response
Escalate, investigate, and close declared incidents in a defined workflow, with the business context that tells the team which incident to work on first.
5
Policy content
Start from current security frameworks and control catalogs, including the ISO 27000 series, COBIT 5, the NIST 800 series, and PCI DSS, all shipped with the use case.
6
Regulatory change
Track changes to IT obligations, judge the business impact, and route the response, so senior management hears about a new requirement from your team first.
How every role benefits from one platform
For security and IT risk teams
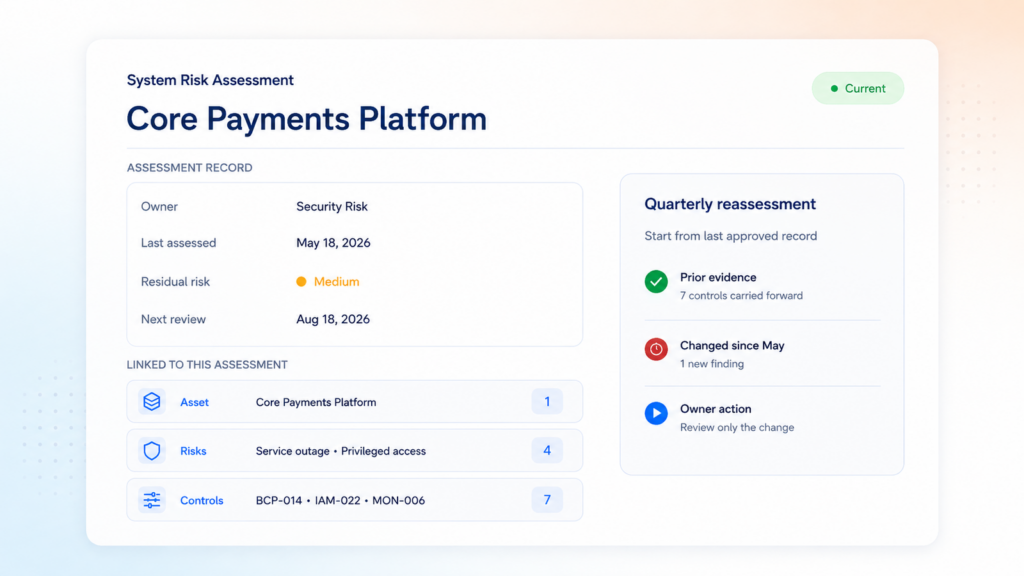
Assess a system once and let the result stand. Risks link to the assets they threaten and the controls meant to hold them, findings carry owners and dates, and next quarter’s reassessment starts from last quarter’s record instead of a blank template.
For the CISO and the CRO
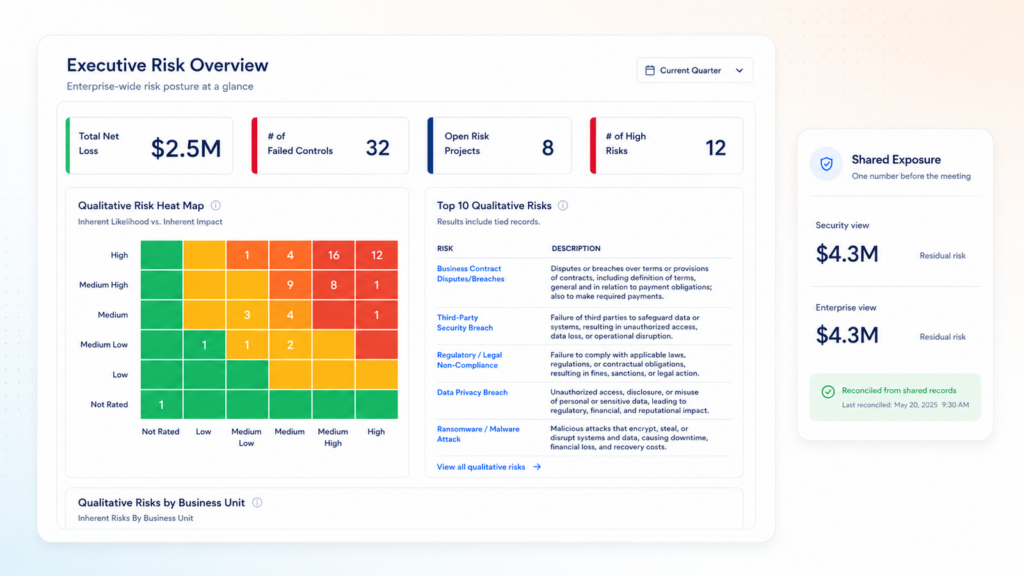
Cyber exposure and enterprise exposure draw on one set of assets, controls, and scenarios, so the security number and the enterprise number reconcile before the executive meeting rather than during it. You fund what the shared picture says matters.
For the board and audit
The exposure summary the board reviews comes from the same records the analysts work in, so a question about one number ends in a control and an owner rather than a promise to follow up. Appetite set in the boardroom reaches the thresholds security runs against.
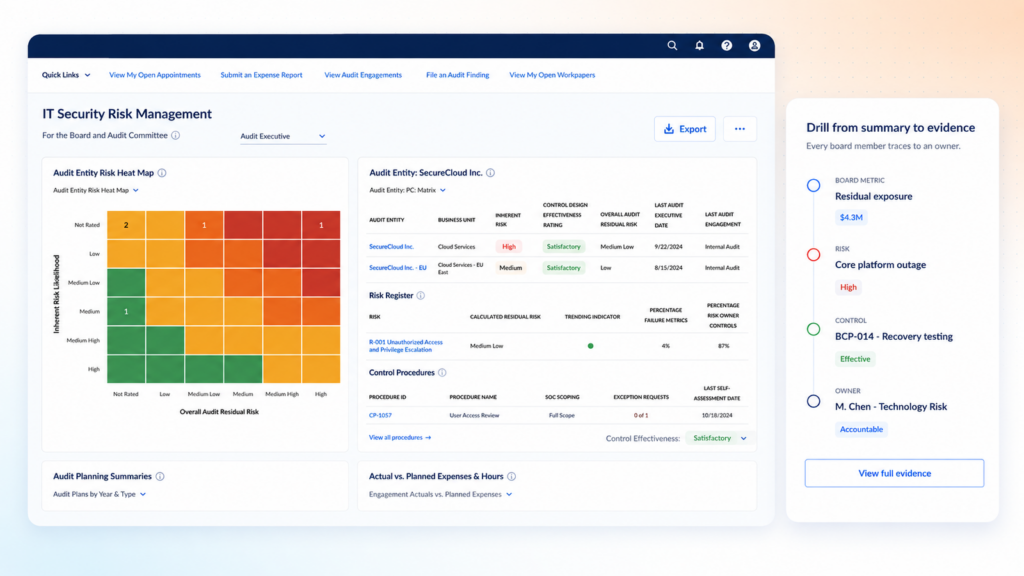
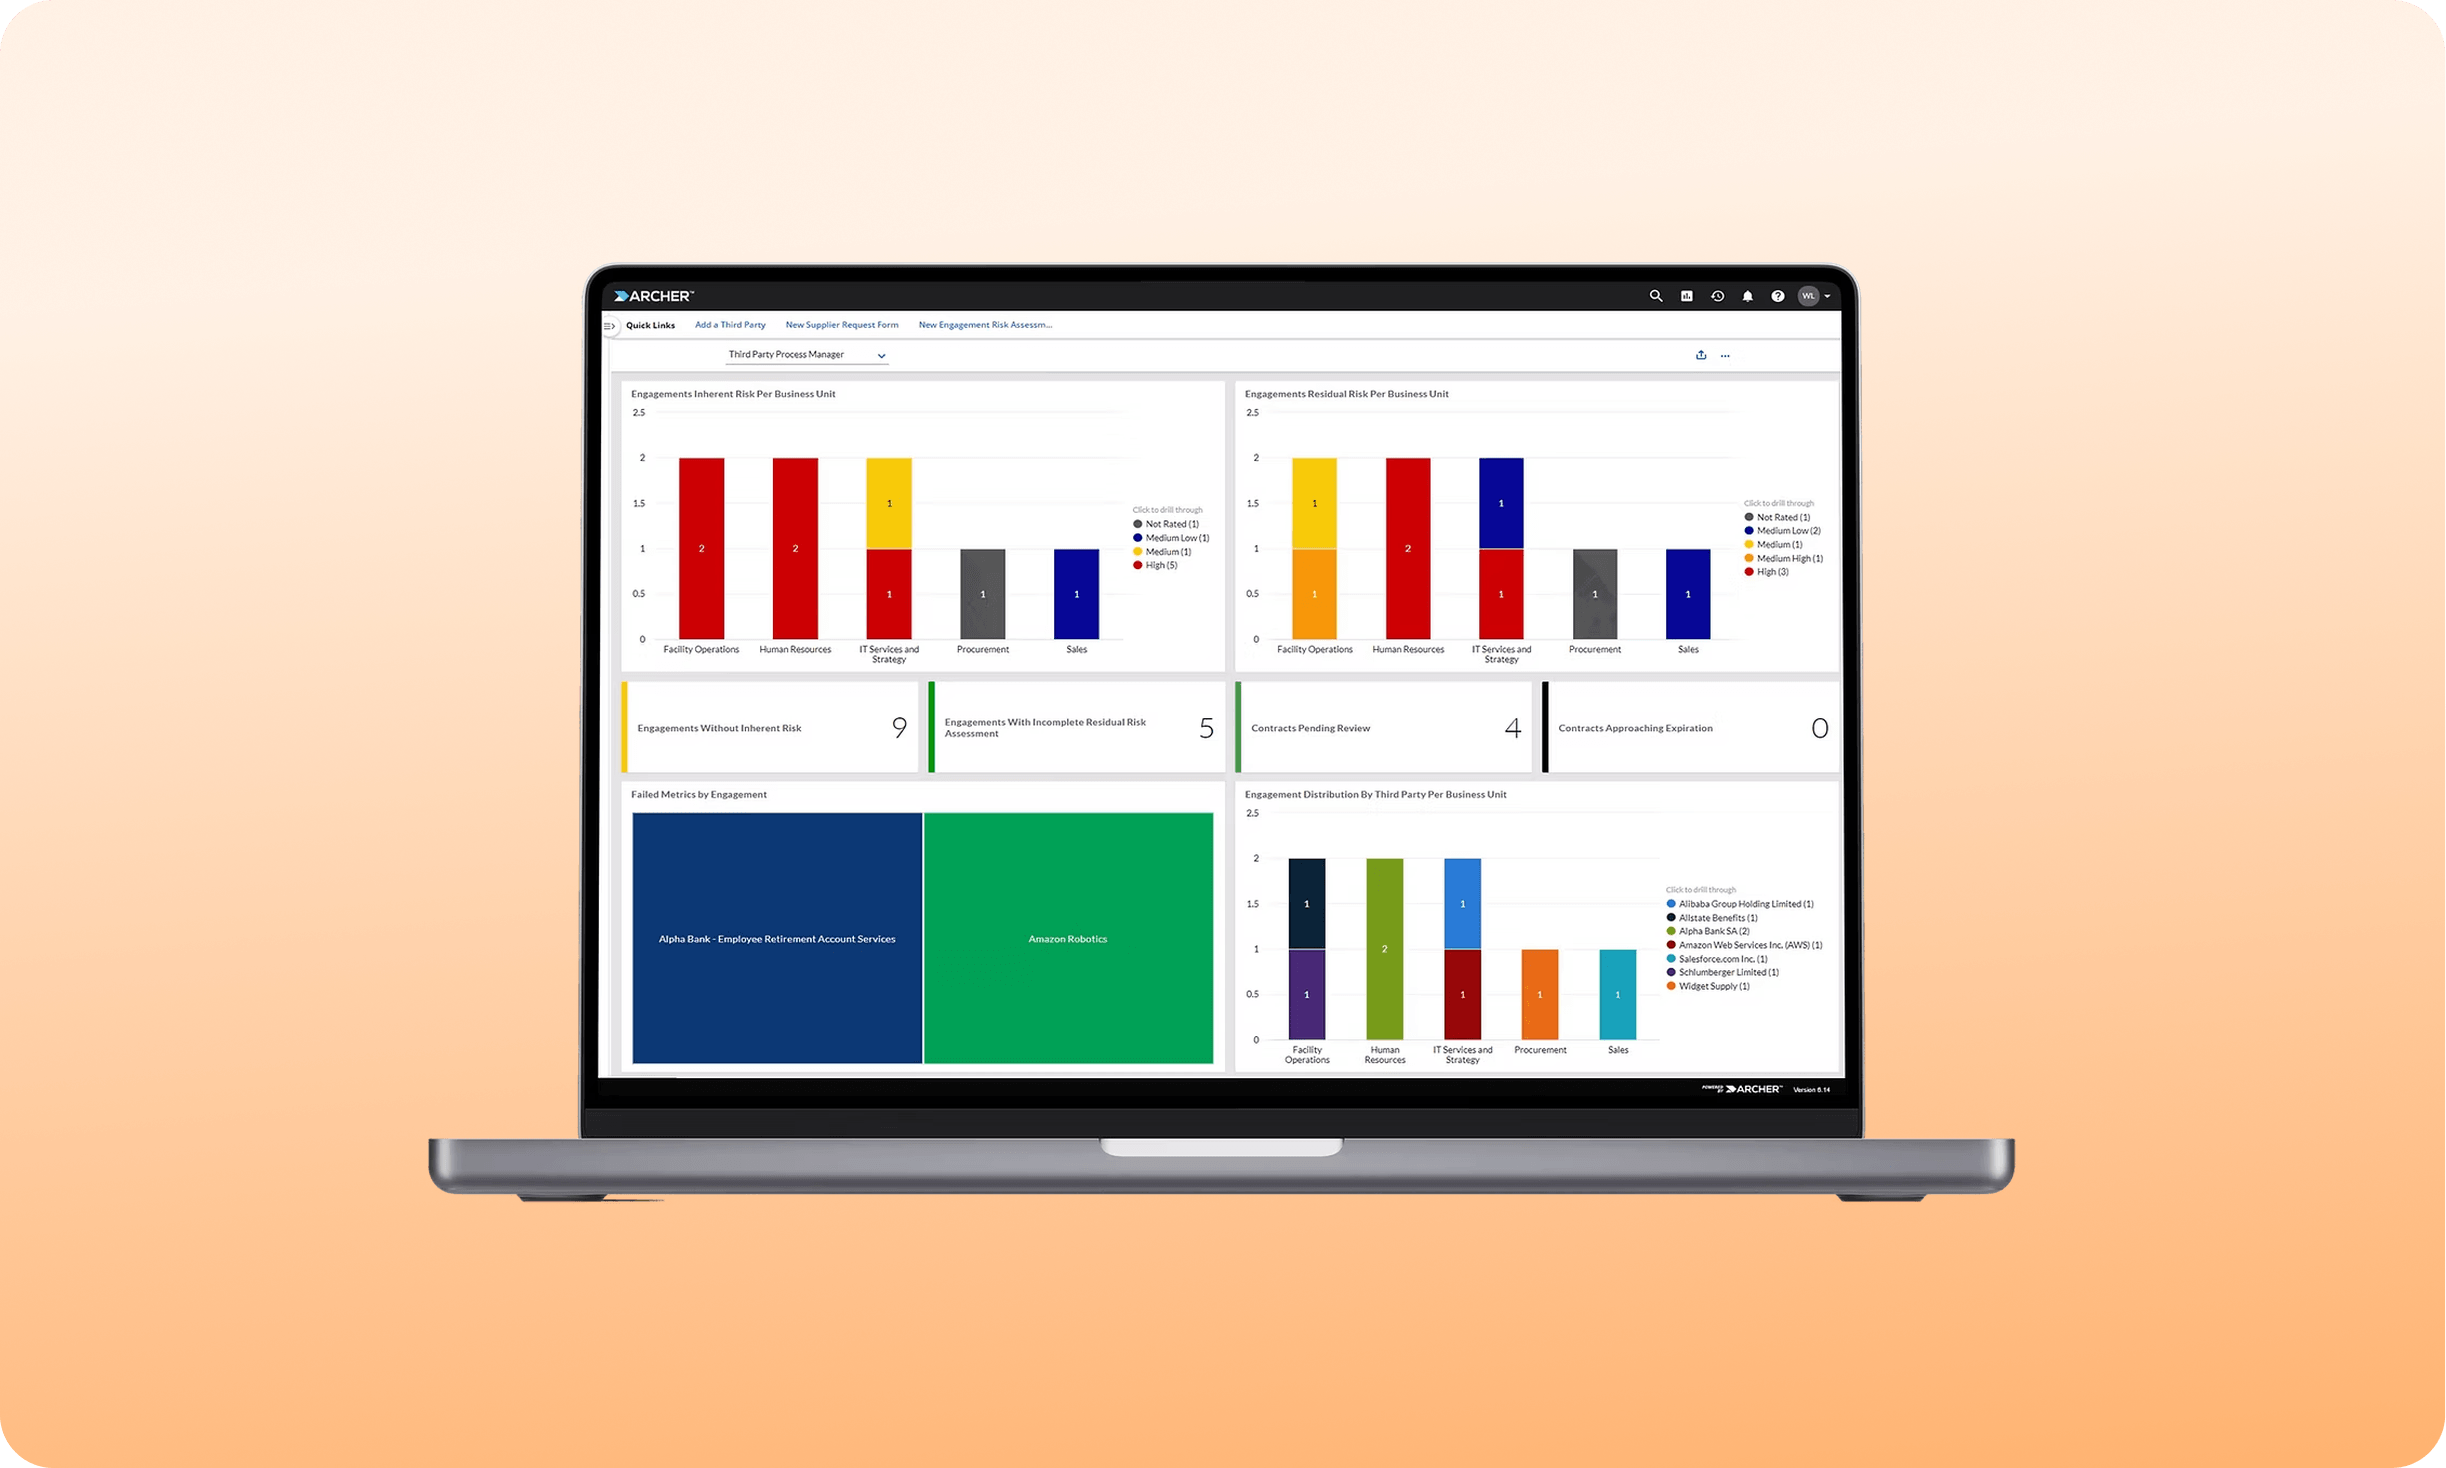
Le immagini riportate sopra non sono screenshot reali del prodotto.
I vantaggi che il tuo team ottiene con Archer
Archer Evolv consente di adottare una strategia integrata per tutte le funzioni relative alla gestione dei rischi e alla conformità.
-
Verifiche più rapide
Riduci i tempi di preparazione dell'audit fino al 40% grazie alla documentazione riutilizzabile e alla raccolta automatizzata.
-
Meno sorprese
Il monitoraggio continuo individua i rischi emergenti prima che si trasformino in incidenti.
-
Costi di attrezzaggio inferiori
Raggruppare gli strumenti GRC che si sovrappongono in un’unica piattaforma e ridurre la proliferazione delle licenze.
-
Reportistica pronta per il consiglio di amministrazione
Genera report per i dirigenti e il consiglio di amministrazione in pochi minuti anziché in giorni.
-
Conformità sicura
Assicuratevi di essere sempre pronti per gli audit in tutti i contesti normativi in cui operate.
-
Si adatta alle tue esigenze
Integra nuove unità, framework e regioni senza dover ricompilare il programma.
What your team gains over a point IT risk tool
Archer sits on the same platform as enterprise and operational risk, so cyber and business risk reconcile before the meeting instead of after.
A point IT risk tool
Work spread across a scanner, a spreadsheet, and a ticket queue
Ecco cosa riceverai
-
Asset data limited to the tool
-
Evidence scattered across systems
-
IT risk only, no business context
Archer IT & Security Risk
One platform for IT risk and enterprise risk
Ecco cosa riceverai
-
One queue, one record, one reassessment cycle
-
Trending on residual risk and control effectiveness
-
Cyber estimates built from the same scenarios enterprise risk uses
-
Appetite set at the top reaches control thresholds and remediation dates
-
Works with the CMDB, scanners, and ITSM you already run
Custom spreadsheet builds
Proof that paperwork moved faster
Ecco cosa riceverai
-
Manual tracking and updates
-
No integration with source systems
-
Risk interpretation varies by user
Scopri i nostri casi di studio
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
- Visualizza il caso di studio:
- Visualizza il caso di studio: Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
- Visualizza il caso di studio: Intuitive Surgical è passata ad Archer SaaS per intraprendere un percorso verso una gestione del rischio più efficace
- Visualizza il caso di studio: Resilienza operativa per gli istituti di servizi finanziari
Oltre 1.500 organizzazioni utilizzano Archer®, tra cui metà delle aziende della classifica Fortune 500 e 37 delle prime 50 banche mondiali. Scopri quali sfide hanno dovuto affrontare i loro team, cosa hanno realizzato e cosa è cambiato.
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
Intuitive Surgical è passata alla piattaforma SaaS Archer per intraprendere un percorso verso una gestione del rischio più efficace
Resilienza operativa per gli istituti di servizi finanziari
Scelto con fiducia dai team che si assumono il rischio
I responsabili dei settori rischio, conformità e audit raccontano cosa è cambiato dopo l’implementazione di Archer Evolv.
Abbiamo riconosciuto la necessità di una piattaforma software GRC che fosse fondamentale per la nostra capacità di migliorare e trasformare i nostri processi aziendali in materia di rischio e conformità.
Archer è la fonte di verità e ci fornisce un'ottima traccia di audit. In qualità di compagnia assicurativa, siamo sottoposti a verifiche da parte di ogni ente governativo. Ora possiamo dire: “Ecco il nostro archivio, date un’occhiata”.
L'aggregazione dei rischi è un aspetto fondamentale per noi: ci permette di individuare dove si concentrano i rischi all'interno dell'organizzazione e di garantire una maggiore visibilità ai consigli di amministrazione e ai dirigenti.
Turkcell utilizza Archer come principale strumento di GRC all’interno dell’azienda. Ci offre un quadro di governance trasparente e sicuro.
Archer ci offre la possibilità di sintetizzare le cose in cifre e dettagli concreti anziché in generalità. Si tratta di una gestione basata sui fatti anziché sull'intuizione o sulla sensazione.
Mette in comunicazione tutte le diverse applicazioni, consentendoti così di sfruttare tali riferimenti incrociati e collegamenti per prendere decisioni aziendali più efficaci, poiché hai tutto a portata di mano in un unico posto.
Questions security teams ask before they choose
Straight answers to what the team running IT and security risk actually needs to know.
Archer configures to the process you run today, and it takes asset context, scan results, and control evidence from systems you already own. Your team maps its own workflow during scoping, well before anything goes live.
Scope drives the timeline. Intuitive Surgical spent seven months choosing and six weeks migrating. Most programs start with one use case out of the nine, and the first thing leadership notices is the reporting time your team stops spending.
Archer takes scan results and asset data as inputs, so your estate stays where it is. Vulnerability findings arrive with business context already attached, and issues route back into the tracking your teams use today.
No. The solution area holds nine use cases and most programs sequence them. Teams often begin with IT risk management or controls assurance, then add vulnerability, incident response, policy, and regulatory work on the same asset and control records.