Patient Trust Starts With Compliance You Can Prove
Archer helps health systems unify HIPAA, privacy, and quality obligations so patient care never waits on paperwork.
Trusted by 1,500+ enterprises · SOC 2 · ISO 27001
-
1,500+
Clienti in 48 paesi
-
50%+
Tra i clienti della classifica Fortune 500
-
65%
Delle organizzazioni che dedicano maggiore impegno alla quantificazione
-
15,000+
Membri della comunità di rischio Archer
Scelto dalle principali istituzioni finanziarie
Perché Archer?
Scopri perché una banca con una lunga tradizione ha scelto Archer per la gestione del rischio e l'innovazione nel campo dell'intelligenza artificiale.
-
50%+
Tra i clienti della classifica Fortune 500
-
25+
Anni di esperienza nei settori della governance, della gestione dei rischi e della conformità
-
1,500+
Organizzazioni che utilizzano Archer
Patient Care is Your Priority, Compliance Shouldn’t be an Emergency
Staff shouldn’t spend their time chasing paperwork. With constant regulatory updates and complex risks on the horizon, manual compliance tracking pulls attention away from where you need to focus.
-
HIPAA, GDPR, and state laws shift constantly
-
Vendor and business associate gaps draw fines
-
High data breach costs eat into clinical budgets
-
Accreditation reviews demand constant proof
Unify a genuinely fragmented regulatory picture
Archer offre funzionalità di livello aziendale per aziende di ogni dimensione.
Gestione dei cambiamenti normativi
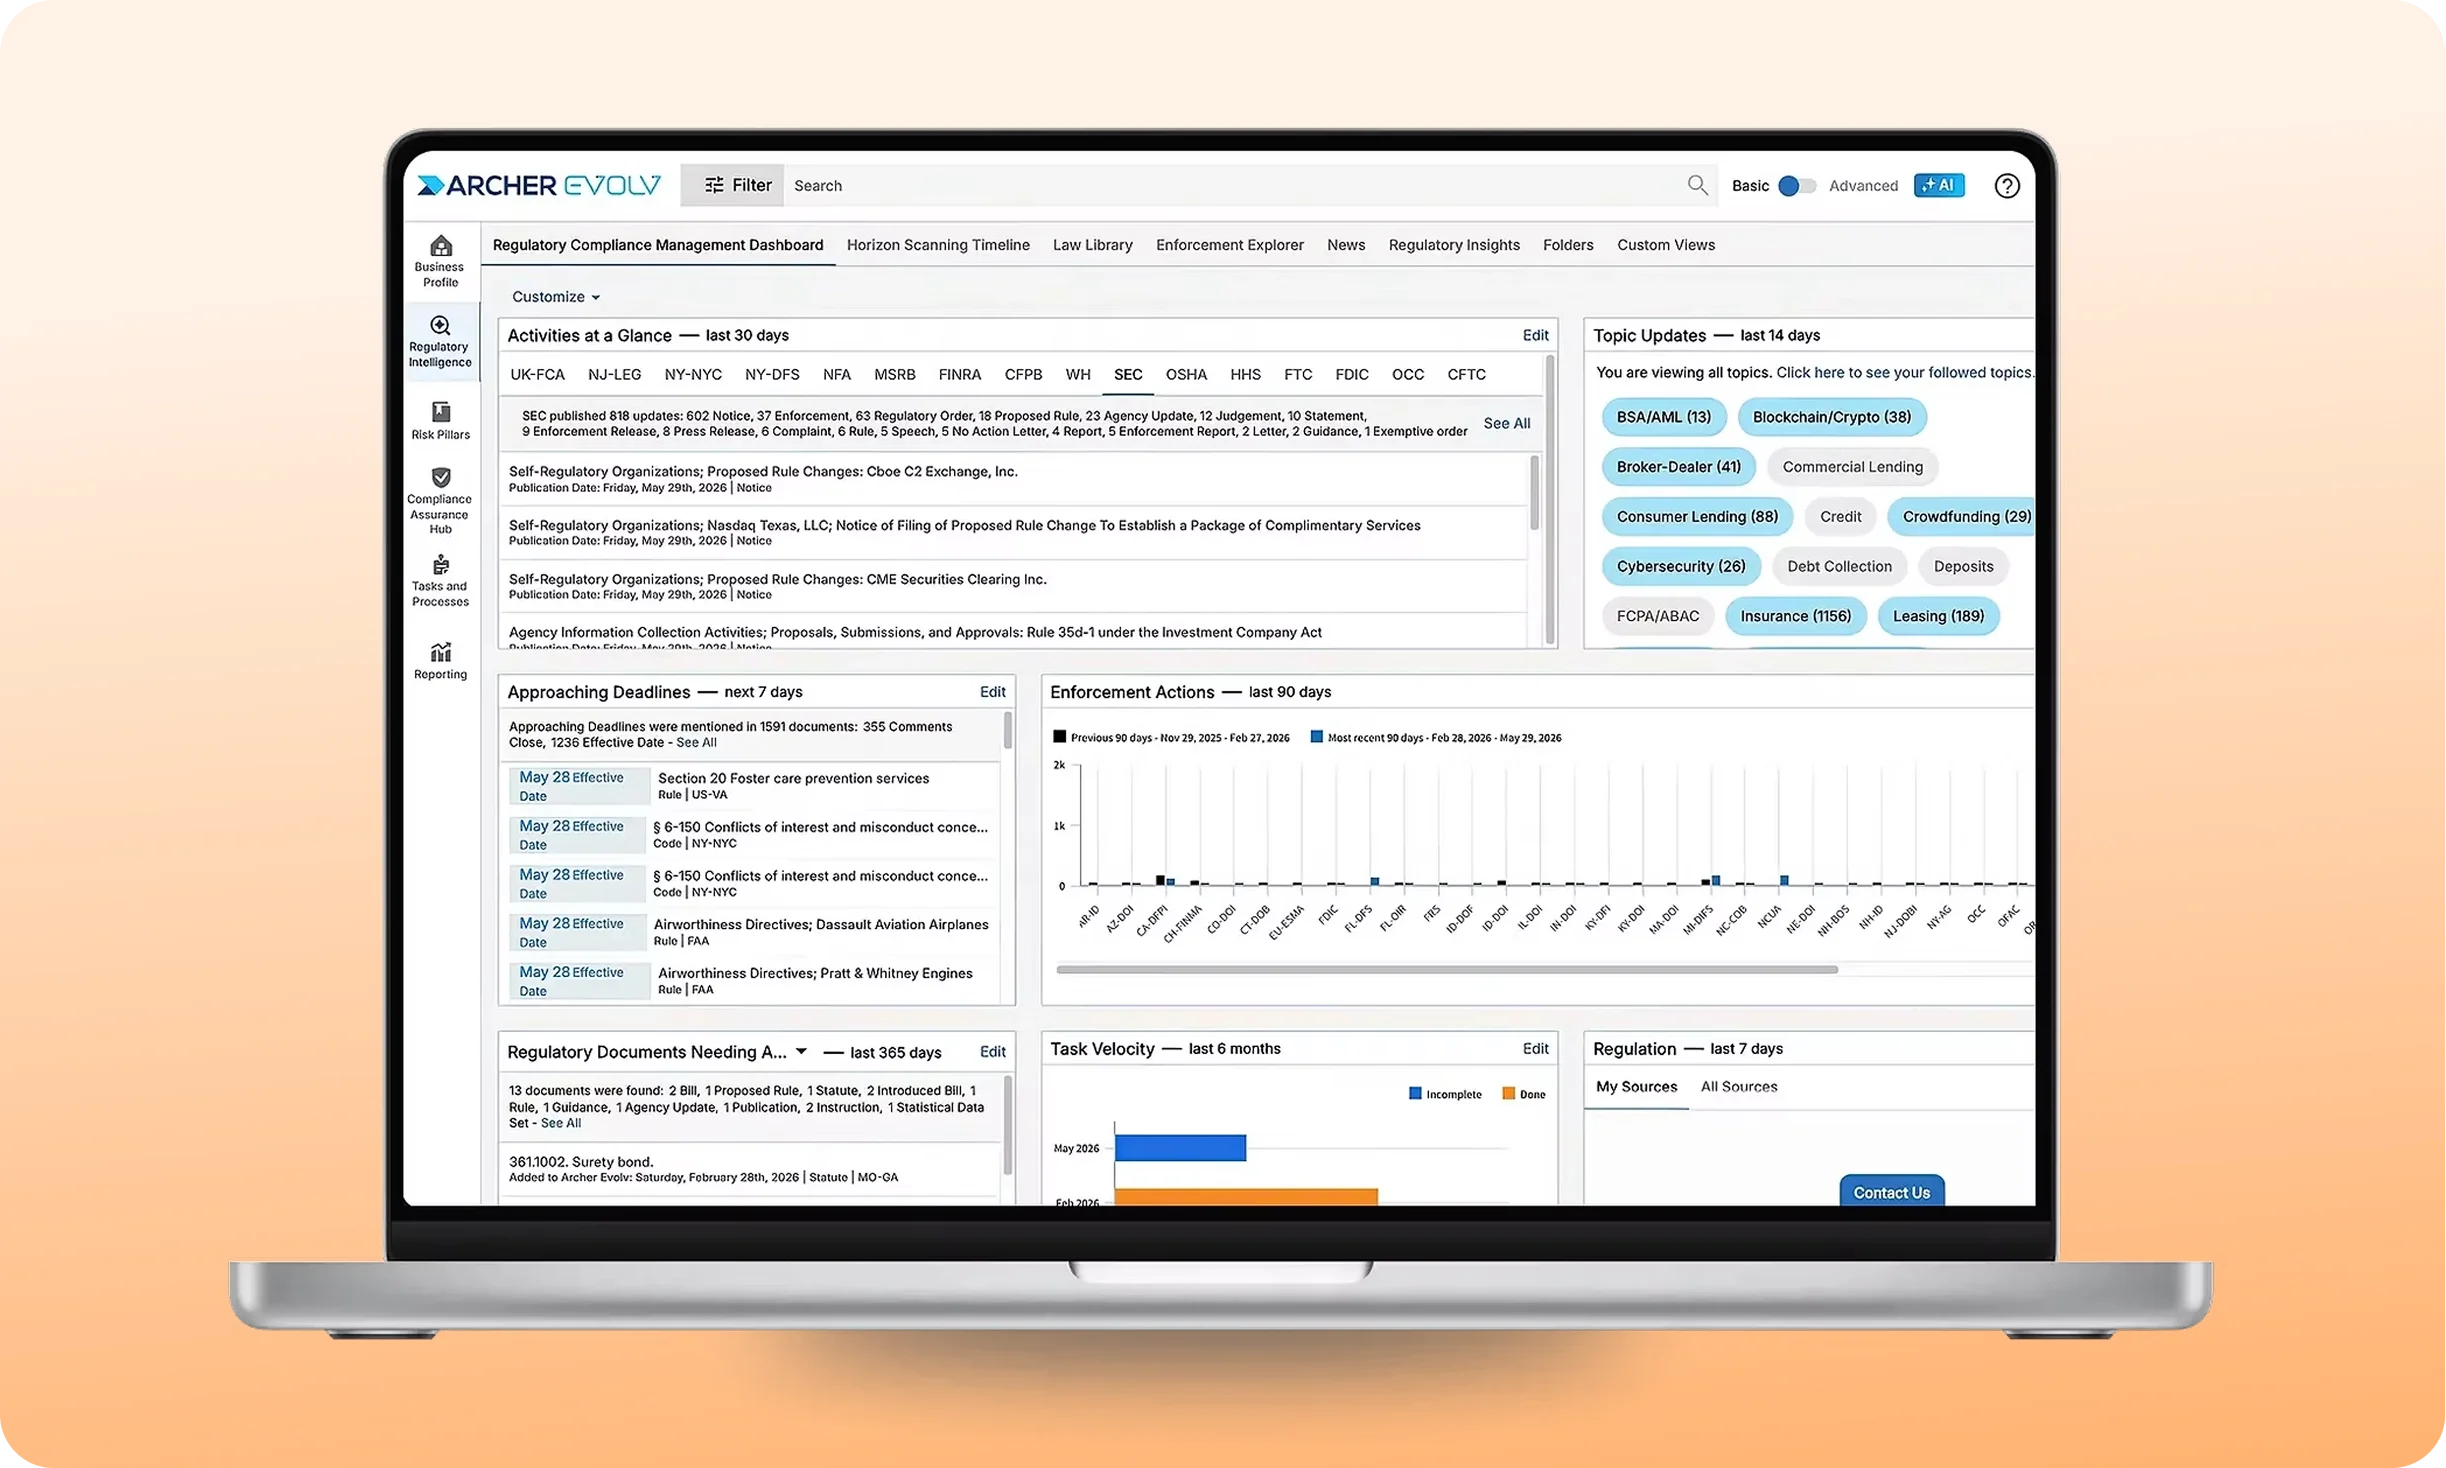
Archer tracks HIPAA, GDPR, and state privacy changes as they happen, so your team knows about a new rule before it becomes a finding.
Test Once, Comply Many
One review of how patient data is secured can satisfy privacy law and accreditation standards at once, cutting audit fatigue for clinical staff.
Vendor Risk Management
Track every vendor’s certifications, audits, and BAAs in one portal, closing the business associate gaps that drive a growing share of HIPAA fines.
AI-powered GRC built for healthcare compliance and accreditation
Archer è stato progettato specificamente per soddisfare le esigenze dei team GRC e degli utenti aziendali.
1
Hub unificato per la conformità
Replace disconnected spreadsheets and tools with a single platform that centralizes risk, compliance, and audit evidence.
2
Accreditation-ready automation
AI workflows automatically generate and organize evidence for CMS, TJC, and CIHC audits in real time.
3
Instant audit evidence
Map controls directly to regulatory requirements so surveyors see proof within seconds, not weeks.
4
Proactive deficiency prevention
Identify and remediate compliance gaps before external surveys and accreditation reviews.
5
Unified program visibility
Give compliance, clinical quality, and audit teams one shared view of your entire risk posture.
6
Healthcare-grade security
SOC 2, ISO 27001, and HIPAA-aligned controls with role-based access and complete audit trails.
Cosa può fare Archer per te?
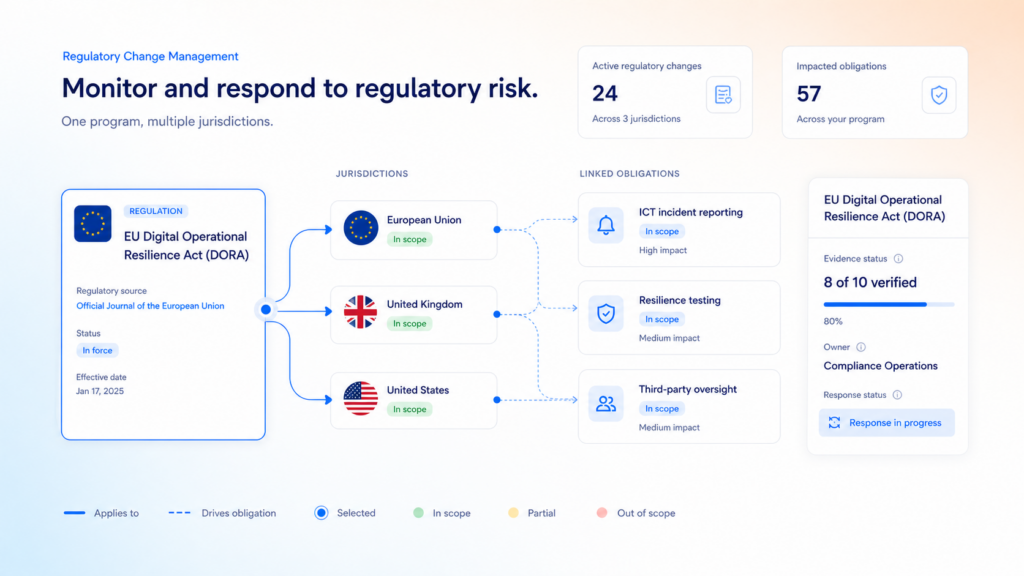
Gestione dei cambiamenti normativi
Track regulatory obligations from federal, state and local regulators from identification through remediation in one system, with clear ownership at every stage. Archer maps each obligation to the controls and policies that satisfy it, so status is always current and defensible to a regulator.
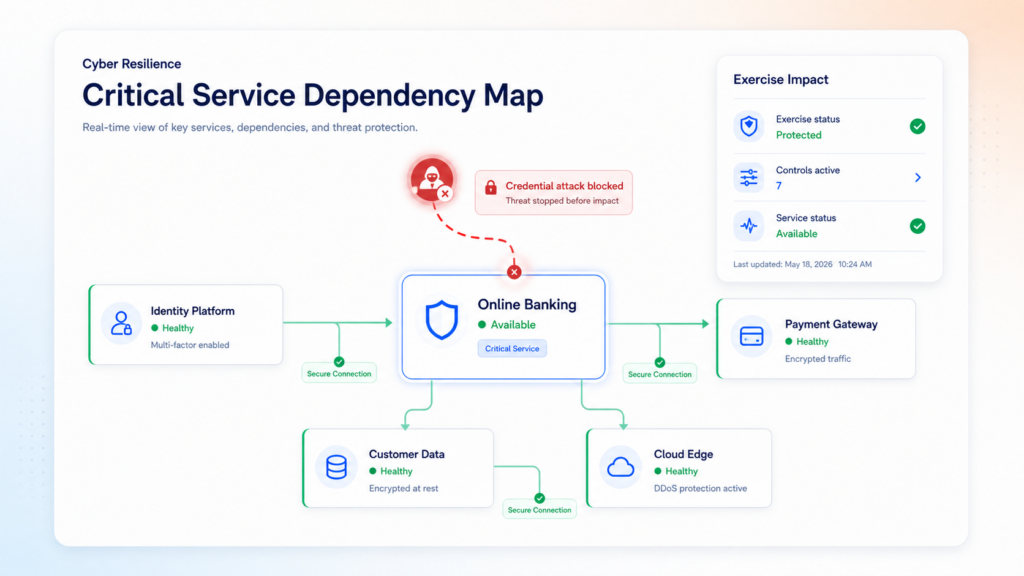
Terze parti, IT/sicurezza informatica e resilienza
Riunisci le attività dei diversi gruppi funzionali in un unico sistema di riferimento, condividendo i dati e favorendo l’integrazione dei processi. Archer può aiutarti a coordinare le attività per definire una strategia coerente in tutte le tue operazioni.
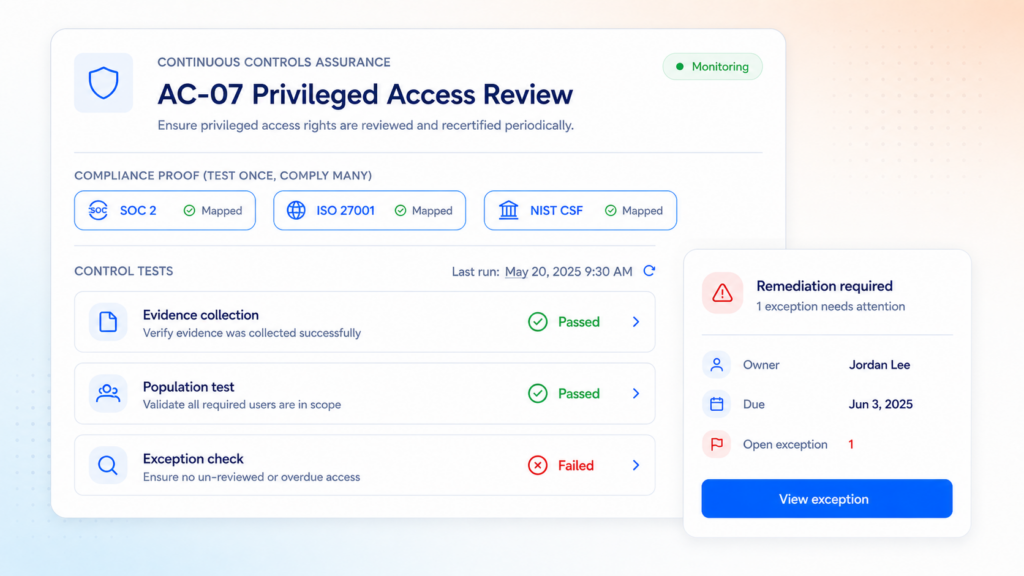
Garanzia di controlli continui
Esegui i test dei controlli a intervalli regolari o in modo continuo, segnala gli errori non appena si verificano e avvia automaticamente le azioni correttive. I dirigenti ottengono una visione in tempo reale dello stato dei controlli, anziché un’istantanea puntuale. Archer è in grado di automatizzare i test dei controlli e facilitare valutazioni continue basate sull’intelligenza artificiale.
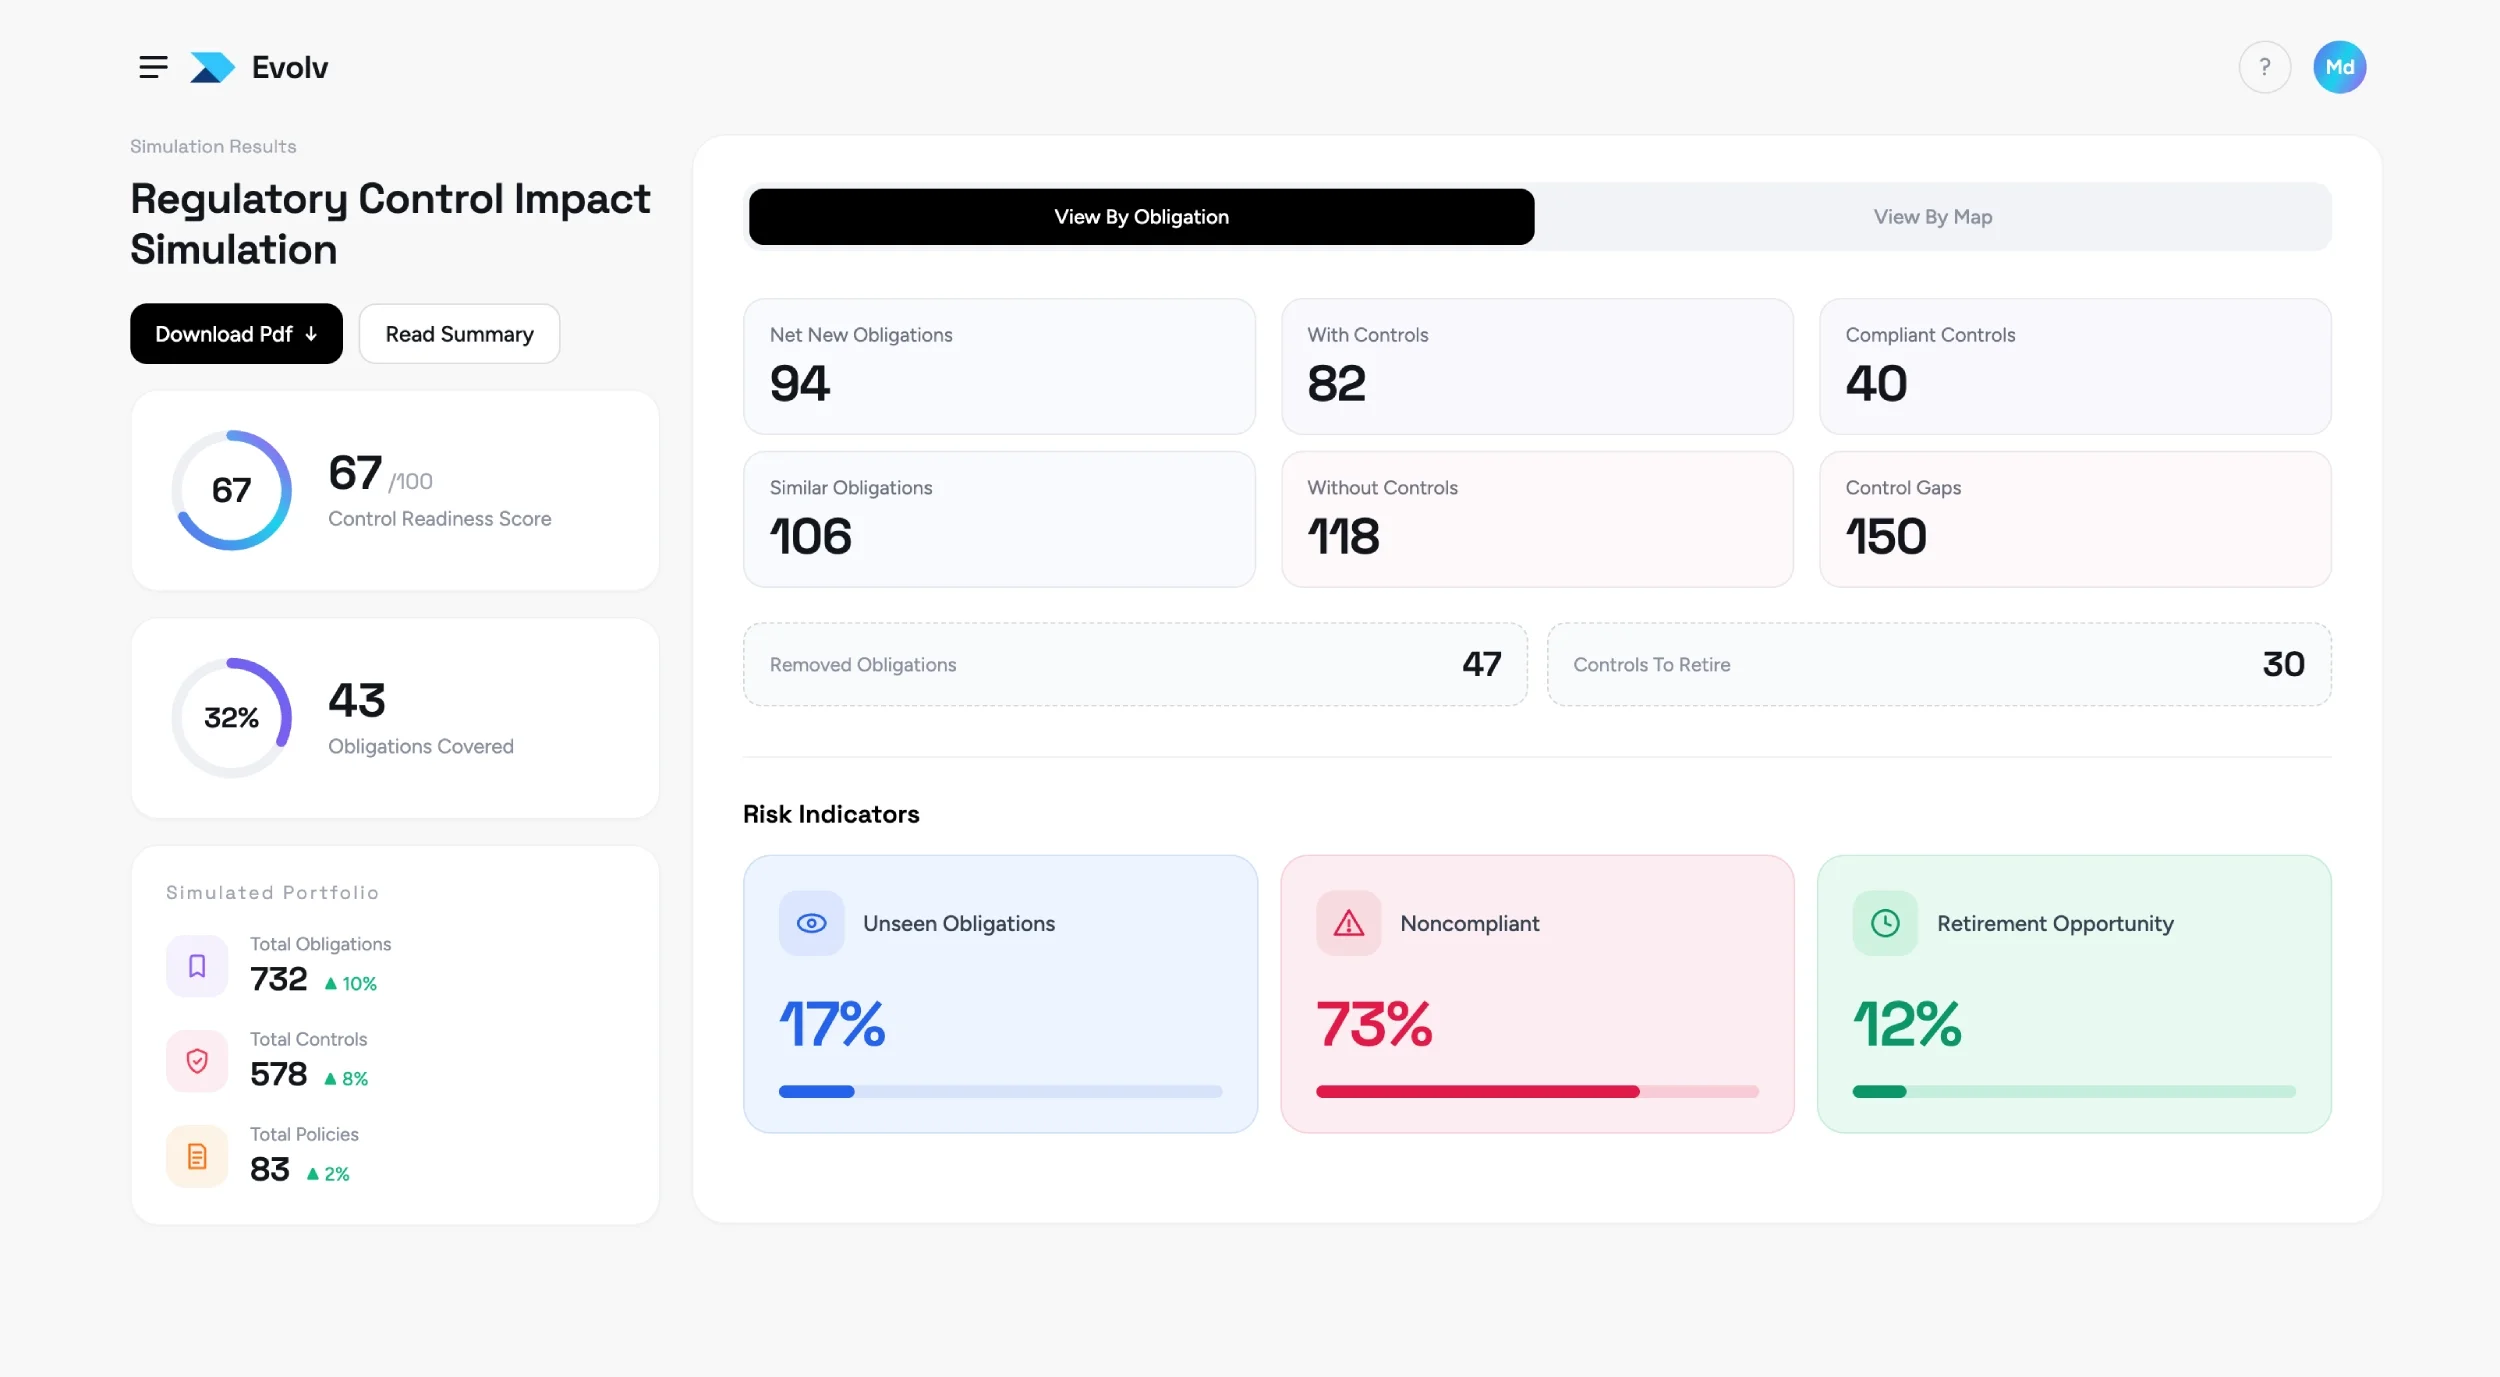
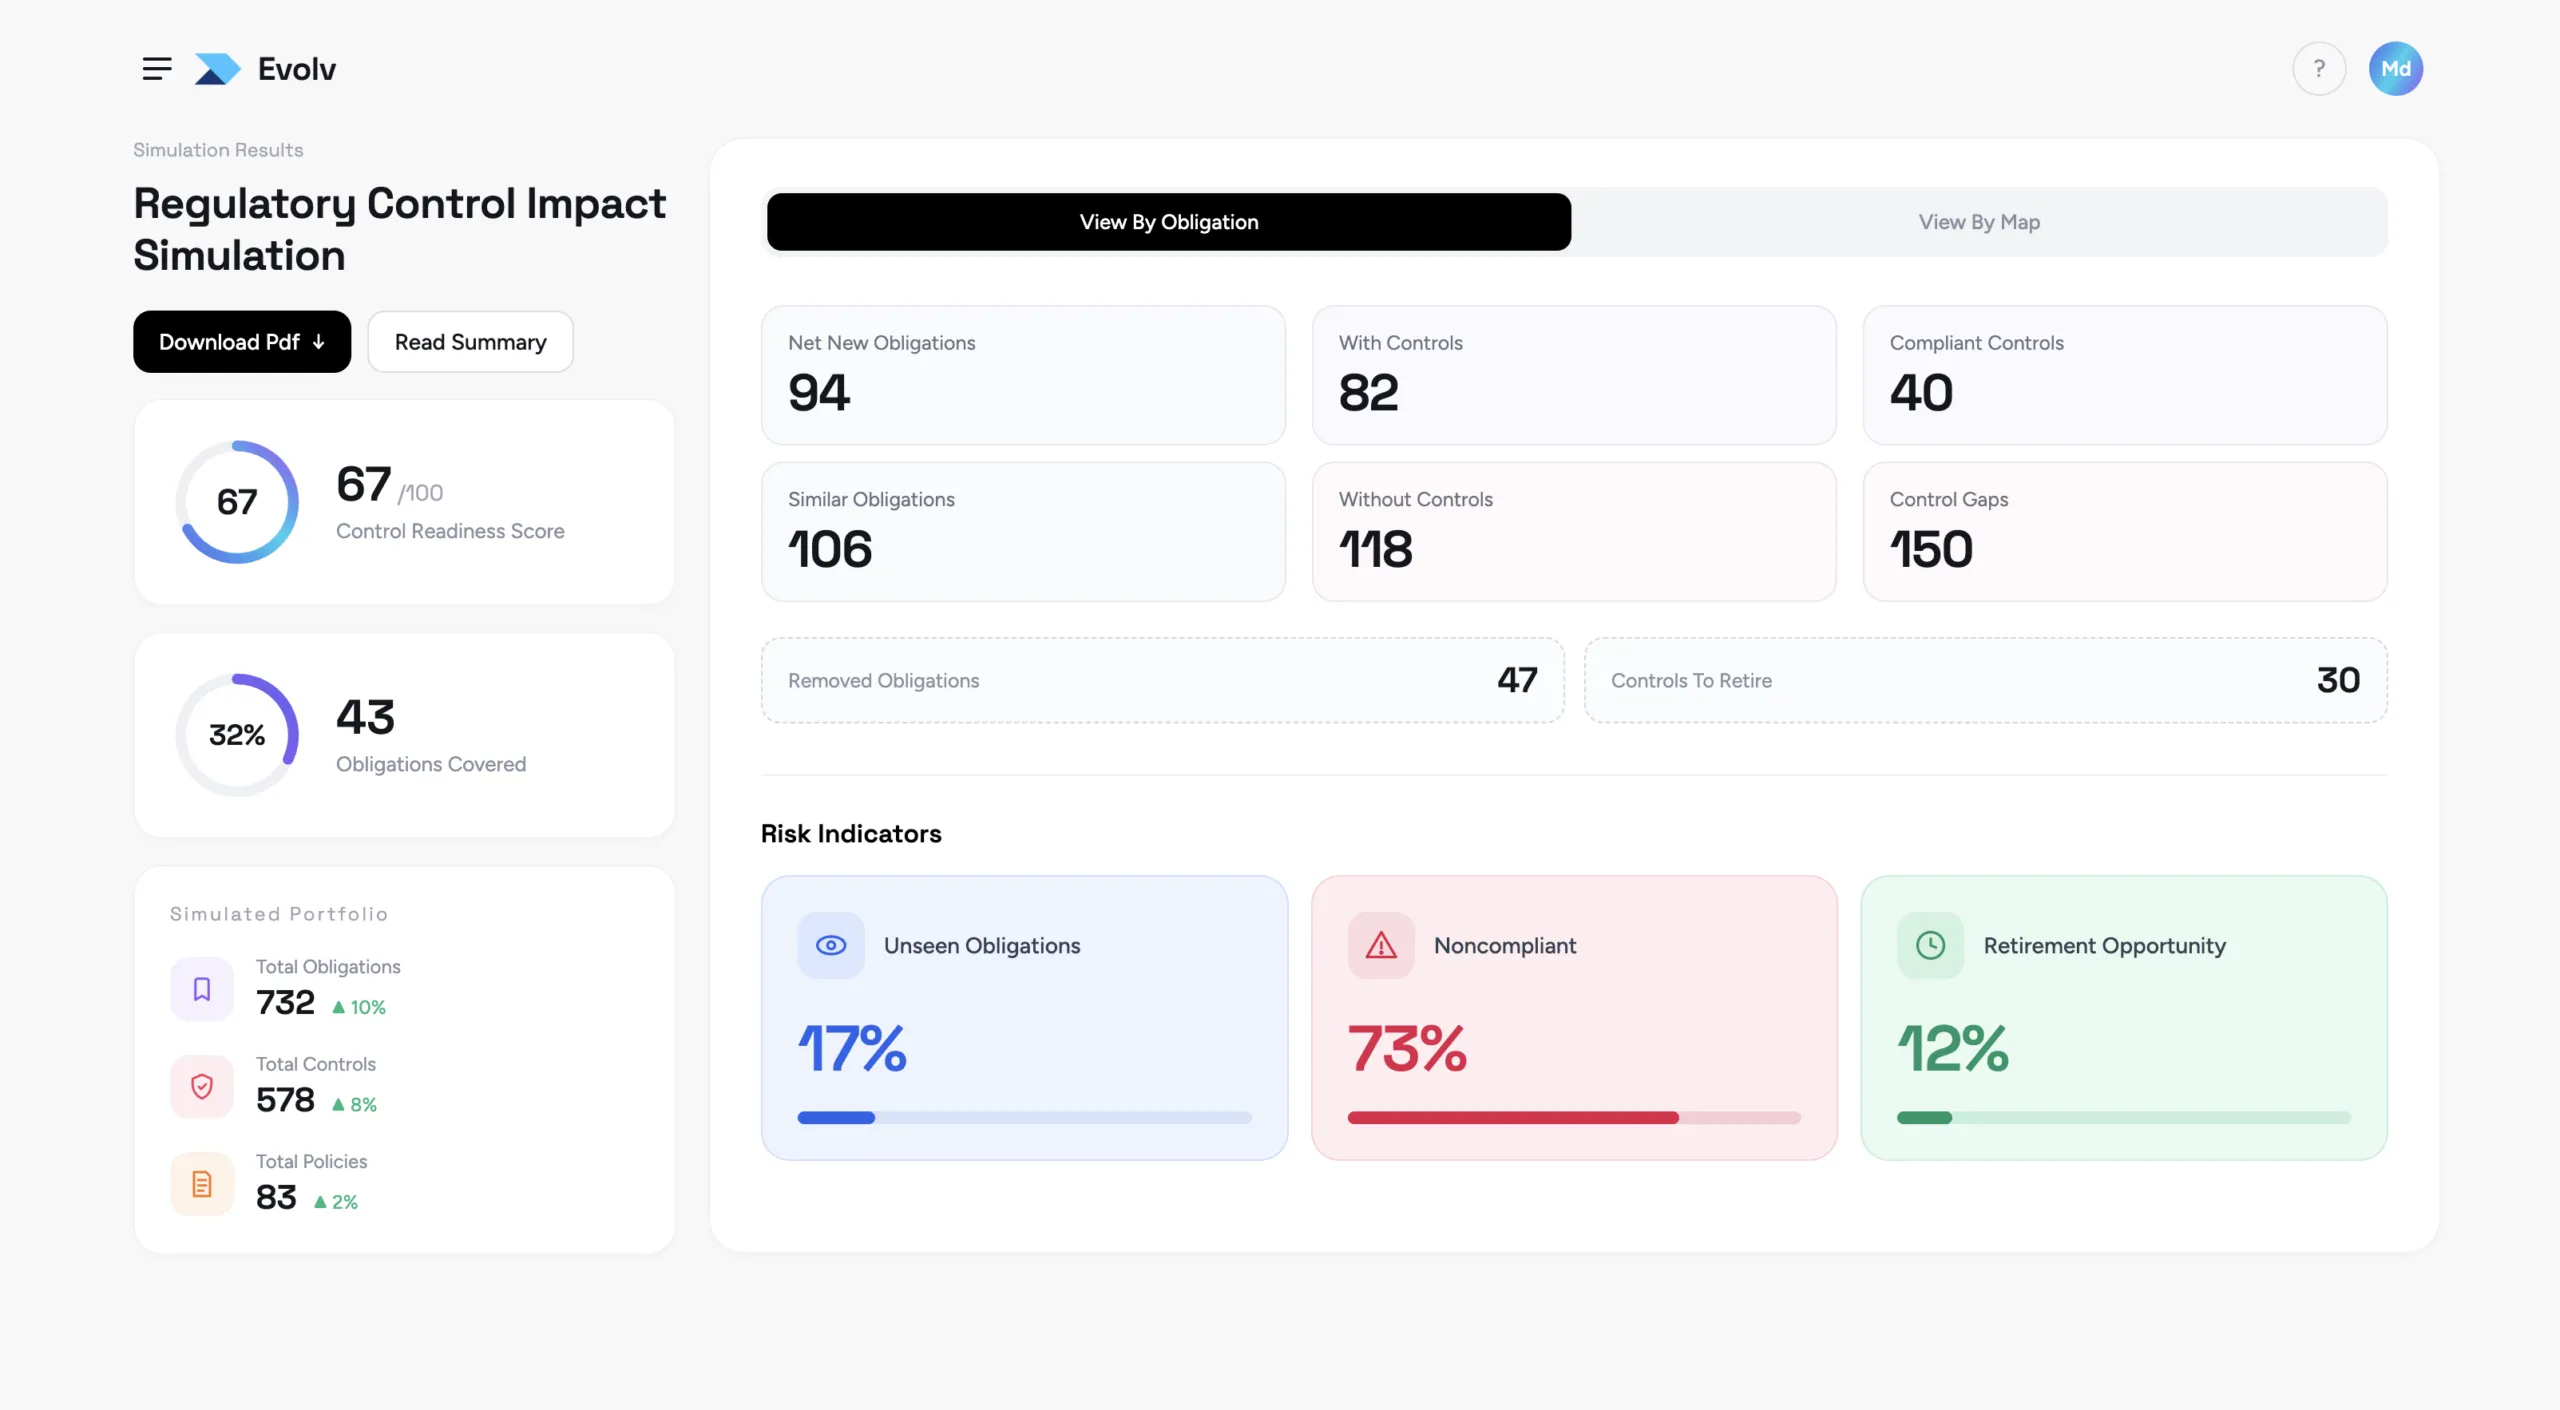
Le immagini riportate sopra non sono screenshot reali del prodotto.
Compliance + Risk Management = Confidence
Archer consente di adottare una strategia integrata che abbraccia tutte le funzioni relative alla gestione dei rischi e alla conformità.
-
Faster audit readiness
Reduce audit preparation time by up to 40% with automated evidence collection and reusable documentation.
-
Prevent compliance gaps
Identify and remediate HIPAA and business associate risks before they trigger OCR investigations.
-
Reduce tool sprawl
Consolidate fragmented GRC systems into one unified platform and lower technology costs.
-
Regulatory visibility
Deliver regulators and boards a single authoritative view of your compliance posture.
-
Protect patient care
Remove compliance burden from clinical teams so they focus on delivering quality healthcare.
-
Expand sustainably
Add new departments, locations, and compliance frameworks without disrupting existing programs.
Healthcare compliance, simplified
See how Archer enables proactive compliance and risk management purpose-built for healthcare’s regulatory complexity.
Spreadsheets and manual processes
Disconnected tracking across multiple systems and departments.
Ecco cosa riceverai
-
Inserimento manuale dei dati
-
Assenza di traccia di audit
-
Redundant compliance work
-
No real-time visibility
ArcherEvolv™
Unified platform that maps regulations to controls and streamlines audits.
Ecco cosa riceverai
-
Regulatory monitoring for healthcare laws (HIPAA, GDPR)
-
Test once, comply many control mapping
-
Closed-loop incident and corrective action tracking
-
Compliance dashboards for leadership
-
Flexible reporting for regulators and accreditors
-
Integrated enterprise risk management
Strumenti generici per la gestione del rischio e della conformità (GRC)
Broad solutions without healthcare-specific workflows.
Ecco cosa riceverai
-
Generic frameworks
-
Manual control mapping
-
Limited healthcare context
-
Separate risk modules
Scopri i nostri casi di studio
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
- Visualizza il caso di studio:
- Visualizza il caso di studio: Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
- Visualizza il caso di studio: Intuitive Surgical è passata ad Archer SaaS per intraprendere un percorso verso una gestione del rischio più efficace
- Visualizza il caso di studio: Resilienza operativa per gli istituti di servizi finanziari
Oltre 1.500 organizzazioni utilizzano Archer®, tra cui metà delle aziende della classifica Fortune 500 e 37 delle prime 50 banche mondiali. Scopri quali sfide hanno dovuto affrontare i loro team, cosa hanno realizzato e cosa è cambiato.
Eastern Bank utilizza Archer per ottimizzare i processi aziendali e semplificare la conformità normativa
Banorte Bank ottiene un quadro preciso dei rischi grazie ad Archer
Intuitive Surgical è passata alla piattaforma SaaS Archer per intraprendere un percorso verso una gestione del rischio più efficace
Resilienza operativa per gli istituti di servizi finanziari
Scelto con fiducia dai team che si assumono il rischio
I responsabili dei settori rischio, conformità e audit raccontano cosa è cambiato dopo l’implementazione di Archer Evolv.
Abbiamo riconosciuto la necessità di una piattaforma software GRC che fosse fondamentale per la nostra capacità di migliorare e trasformare i nostri processi aziendali in materia di rischio e conformità.
Archer è la fonte di verità e ci fornisce un'ottima traccia di audit. In qualità di compagnia assicurativa, siamo sottoposti a verifiche da parte di ogni ente governativo. Ora possiamo dire: “Ecco il nostro archivio, date un’occhiata”.
L'aggregazione dei rischi è un aspetto fondamentale per noi: ci permette di individuare dove si concentrano i rischi all'interno dell'organizzazione e di garantire una maggiore visibilità ai consigli di amministrazione e ai dirigenti.
Turkcell utilizza Archer come principale strumento di GRC all’interno dell’azienda. Ci offre un quadro di governance trasparente e sicuro.
Archer ci offre la possibilità di sintetizzare le cose in cifre e dettagli concreti anziché in generalità. Si tratta di una gestione basata sui fatti anziché sull'intuizione o sulla sensazione.
Mette in comunicazione tutte le diverse applicazioni, consentendoti così di sfruttare tali riferimenti incrociati e collegamenti per prendere decisioni aziendali più efficaci, poiché hai tutto a portata di mano in un unico posto.
Le domande che ci vengono poste più spesso
Straight answers to what healthcare compliance and risk teams ask before choosing Archer.
Archer consolidates all compliance obligations from HIPAA, GDPR, and national healthcare laws into one unified system, letting you map privacy requirements directly to controls on patient data handling across every ward and department.
Yes. Archer’s Controls Assurance enables a test-once, comply-many approach where one thorough control assessment satisfies multiple regulatory and accreditation requirements simultaneously, cutting redundant paperwork.
Archer integrates risk and compliance management so you can log patient safety incidents or privacy breaches, trigger investigations and corrective actions, and monitor resolution in a closed-loop process.
The platform continuously monitors the healthcare regulatory landscape and alerts you to changes in privacy rules, legislation, and industry standards so you can adapt quickly.
Archer dashboards give at-a-glance visibility into compliance posture and risk indicators like overdue staff training or open corrective actions, enabling leadership to act before issues escalate.