Archer Summit 2026 (Virtual)
Archer Summit brings customers, partners, and industry leaders together to explore bold ideas, innovative solutions, and what’s next in risk management.
Insights, best practices, and expert perspectives on integrated risk management.
Archer Summit brings customers, partners, and industry leaders together to explore bold ideas, innovative solutions, and what’s next in risk management.
All Resources (59)
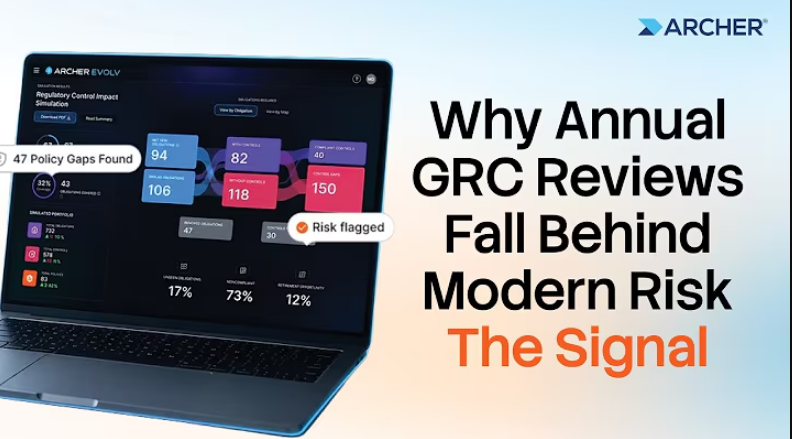
Risk, regulation, third-party exposure, and AI are expanding GRC workloads faster than teams can hire. At Archer Summit 2026, we showed what it looks like when that gap starts to…
Nearly three-quarters of enterprises expect to be using AI agents within two years. One in five can govern them. That gap is where the exposure lives, and it isn’t a…
AI is fundamentally changing how organisations manage risk, controls and governance – but what does this mean for the traditional Three Lines Model and the future role of the control…
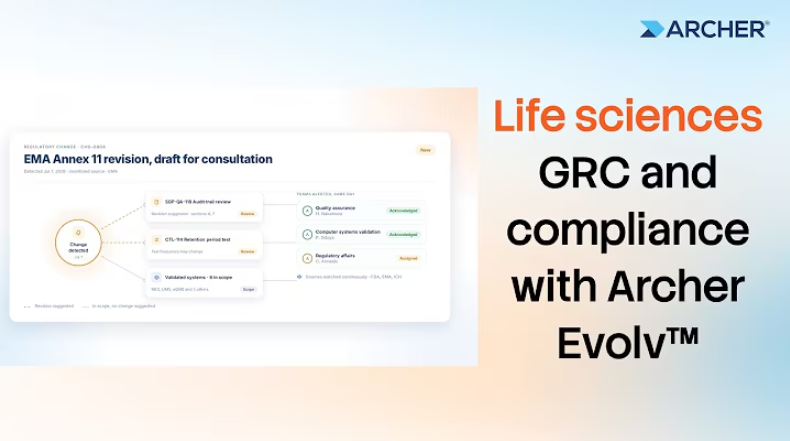
The arrival of the NIS2 Directive represents the most significant shift in European cybersecurity regulation to date. With expanded scope, stricter incident reporting timelines, and direct personal liability for senior…
Modern organizations need faster and more reliable insights into risk and compliance. However, many Cyber GRC programs still rely on manual processes that delay reporting and limit visibility into control…
Most organisations still treat risk as a defensive function, focused on monitoring and reporting. In today’s fast-changing environment, that approach is no longer enough. Leading organisations are redefining risk management…
With the rise of AI, evolving regulation and geopolitical uncertainty reshape the risk landscape, the role of the Chief Risk Officer has never been more complex.
Artificial intelligence is not coming to governance, risk, and compliance — it is already here. But the critical question for GRC executives and practitioners is not simply whether to use…
Regulations update every seven minutes globally. Enterprise data volumes double every eighteen months. More than 60% of risk leaders lack real-time visibility into emerging threats, and over 70% of GRC…