We recognized the need for a GRC software platform that would be central to our ability to improve and transform our enterprise risk and compliance processes.
One governed system connecting risk, controls, obligations and evidence, so you see exposure shift early and prove which controls reduce it.
38 of the Top 50 Banks use Archer
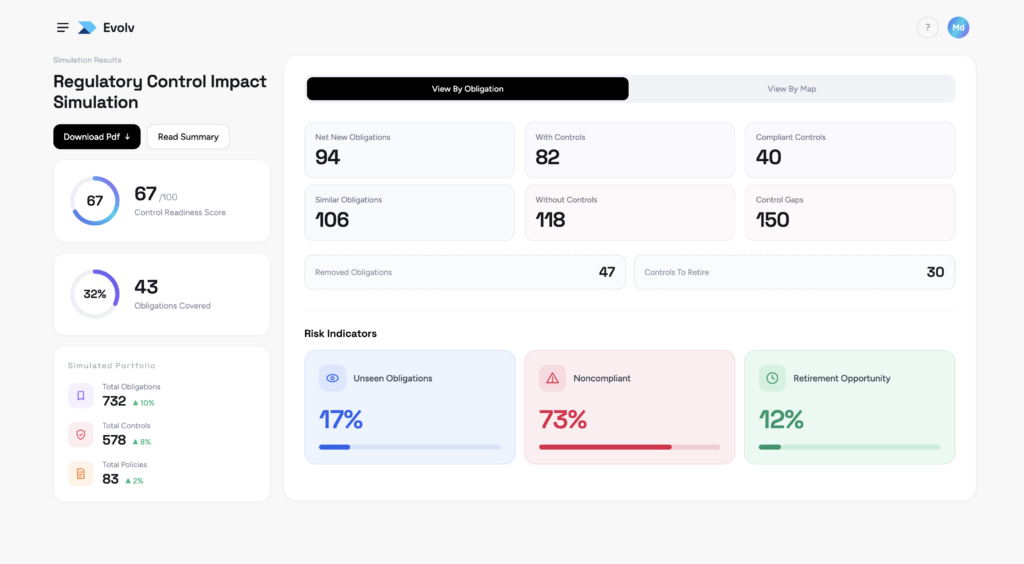
Archer helps the world’s most regulated enterprises stay ahead of regulatory change with AI-powered insights and full audit lineage from source to obligation, control and evidence.
50%+
Of customers in the Fortune 500
25+
Years in governance, risk and compliance
1,500+
Organizations running on Archer
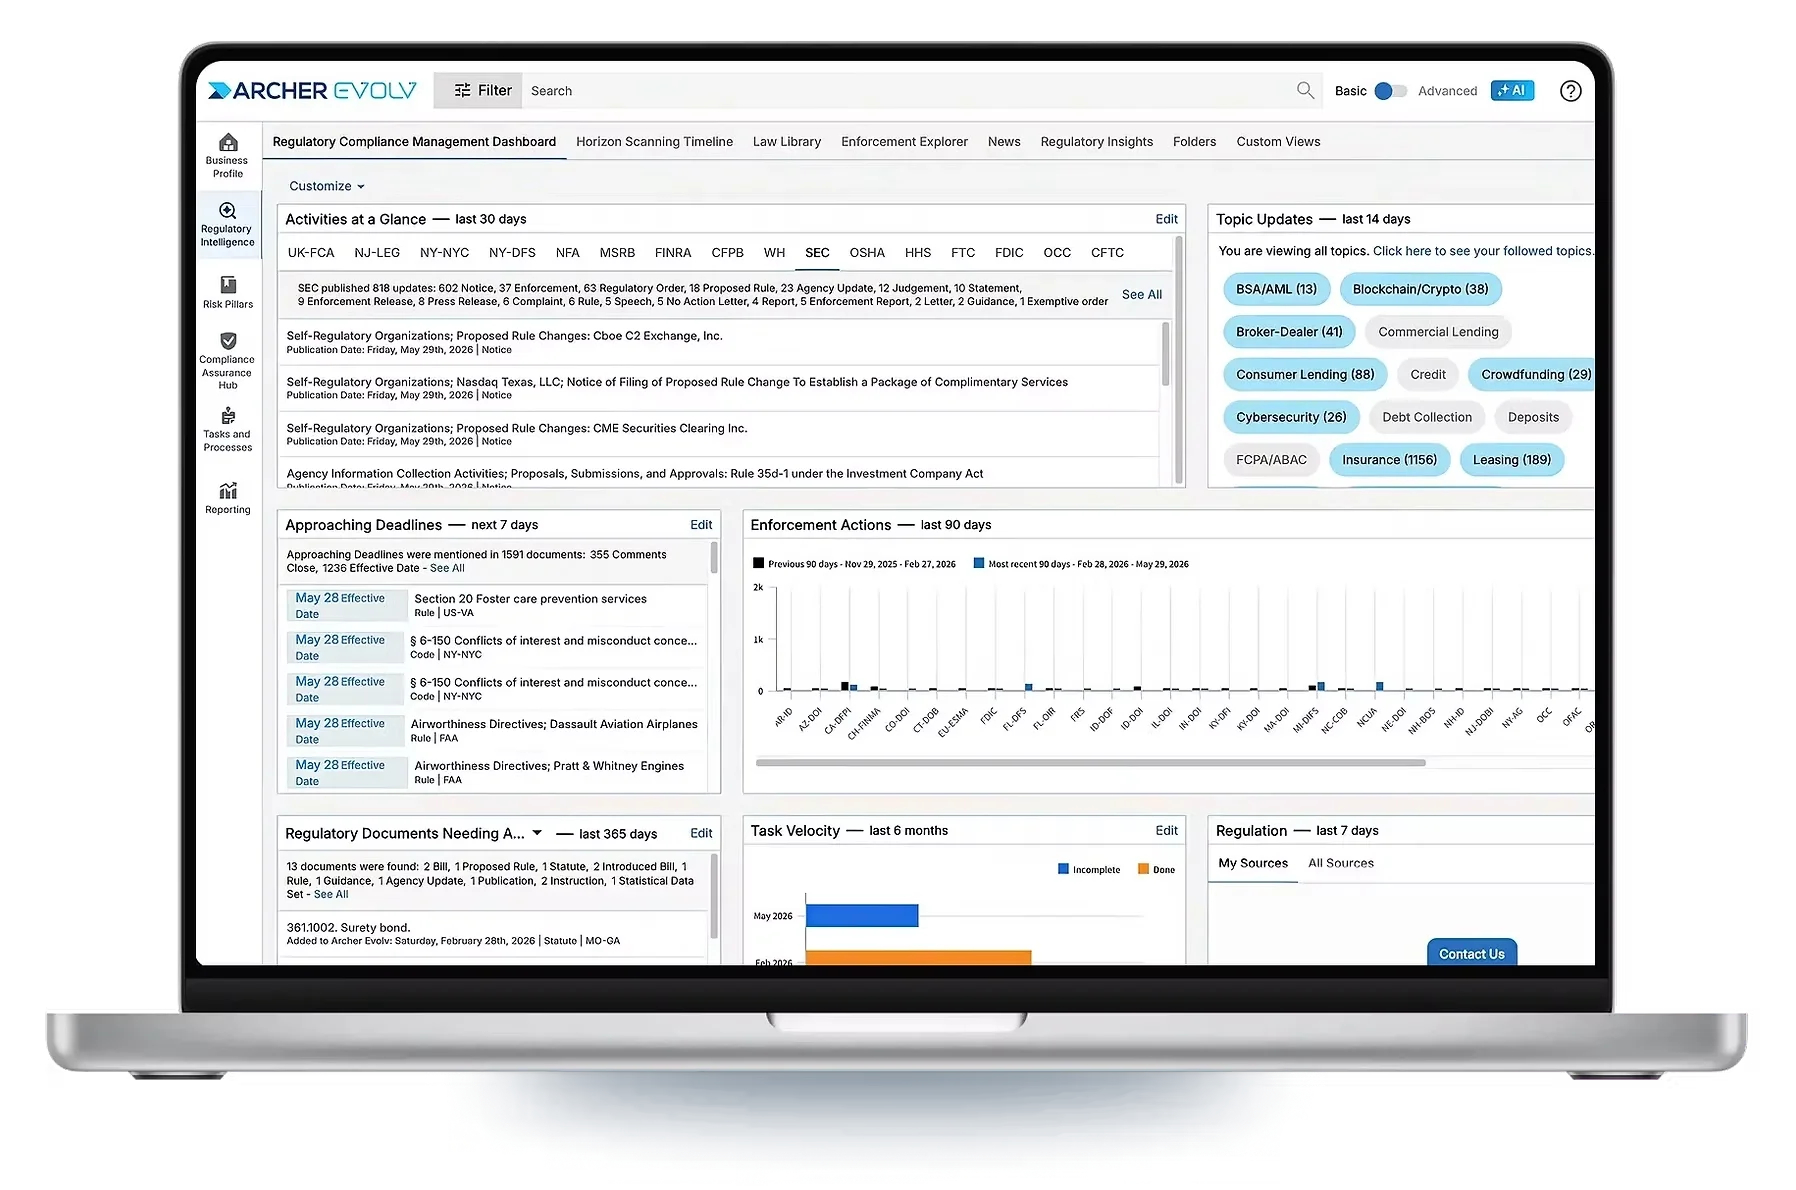
Archer Evolv brings AI-powered intelligence to your existing GRC program, connecting regulatory change obligations, controls, policies, and assurance evidence. Deploy standalone or alongside Archer GRC, on-premises or SaaS, without a costly migration or rebuild.
Continuously monitors authoritative sources to surface relevant regulatory changes earlier.
Uses compliance-trained AI to turn dense regulatory text into structured, traceable obligations.
Keeps obligations, policies, controls, and evidence connected as regulatory requirements change.
Models the potential impact of proposed regulatory change before new requirements take effect.
Regulatory change moves faster than teams can interpret, assess, and operationalize it, creating a growing compliance gap.
Rules are proposed, revised, delayed, and replaced, forcing teams to continuously reassess obligations, controls and impact.
AI introduces new risks, regulations, and governance demands while organizations have little precedent to guide their response.
System of record, system of intelligence, system of outcomes. One connected foundation that puts governed AI to work immediately, using your existing permissions and audit trail.
Your trusted GRC foundation. Enterprise, operational, IT, third-party risk data, workflows permissions, history and controls.
Includes
Evolv understands the context of your GRC environment and turns data into governed intelligence with AI operators.
Includes
Digital workers put intelligence into action. Continuously executing work within your controls and permissions.
Includes
Every signal, decision, action and outcome feeds the next, helping your GRC program continuously adapt and improve.
1
Monitors risk signals and 9,300+ regulatory sources for change
2
Prioritize obligations by impact and route to the right owner
3
Automate task routing, control mapping, policy alignment
4
Capture evidence, produce attestations, and maintain defensible audit trails
5
Learn from real outcomes to continuously improve 492 proprietary AI models
Others offer pieces. Archer brings risk, controls, obligations and evidence into one governed system.
Connects exposure to the controls that reduce it, so you can show which interventions worked.
“Archer helps us understand uncertainty, connect it to what matters to our business, and make better decisions about what to do next.”
Head of Enterprise Risk, global financial services firm
Less time proving compliance. More capacity for the risk work that matters.
Monitors operational, IT and third-party risk continuously, then orchestrates the response.
“Archer helps us understand uncertainty, connect it to what matters to our business, and make better decisions about what to do next.”
Head of Enterprise Risk, global financial services firm
Less time proving compliance. More capacity for the risk work that matters.
Quantified risk and modeled impact, so decisions get made on numbers instead of narrative.
“Archer helps us understand uncertainty, connect it to what matters to our business, and make better decisions about what to do next.”
Head of Enterprise Risk, global financial services firm
Less time proving compliance. More capacity for the risk work that matters.
Workplace is where AI operators do the work. Each operator is built for one governed task, grounded in your risk data and 9,300+ regulatory sources, and traceable to the source behind every result. Pick your domain.
Stay ahead of emerging risk

Risk data moves faster than quarterly reviews. Operators monitor it continuously, score emerging issues, and show where exposure is shifting. Less gathering, more deciding.
Govern technology risk as it changes

Operators monitor technology risks, controls, and issues, enforce your standards, and rank what needs attention first. Keep pace with an environment that keeps changing.
Know which parties need action

Operators run third-party reviews end to end, monitor vendors between assessments, and enforce your requirements as conditions change. Grow the ecosystem without adding headcount.
Keep pace with regulatory change

Operators scan 7,000+ regulatory sources, map new obligations to your controls and policies, and flag the gaps. You review the exceptions, not the rulebook.
Accelerate audit work and assurance

Evidence collection is where audits stall. Operators pull evidence, read prior findings, and flag areas of concern, so auditors spend their time on judgment and assurance.
The images used above are not actual product screenshots.
Archer Insight quantifies exposure in monetary terms, models scenarios, and aggregates risk for the board. Management by fact, not intuition.
See how expert-in-the-loop AI, 25 years of GRC data, and audit-grade workflows come together inside the control fabric. Engineered for risk and regulation. Not retrofitted.
See how risk, compliance, and audit leaders are changing how GRC gets done.
We recognized the need for a GRC software platform that would be central to our ability to improve and transform our enterprise risk and compliance processes.
Archer is the source of truth, and it creates a nice audit trail for us. As an insurance company, we're audited by every governmental entity. Now we can say, here's our repository, take a look.
Risk aggregation is a big point for us, to see where our risk is located within the organization, and to give greater visibility for boards and executives.
Turkcell is using Archer as the main GRC tool in the company. It provides us a transparent and safe governance framework.
Archer gives us the ability to boil things down into numbers and specifics versus generalities. It's management by fact versus intuition or feel.
It connects all the different applications together, so you can use those cross-references and connections to make better business decisions, because you have it all in one place.
Case Studies
See how risk teams detect earlier, quantify exposure, and build programs that survive scrutiny.
See how human-in-the-loop trained AI, twenty-five years of GRC data, and audit-grade workflows come together inside the control fabric. Built for compliance. Not retrofitted.