Governance That Keeps Pace With Federal Mandates
Archer helps government agencies unify FedRAMP, CMMC, and FISMA obligations so compliance keeps pace with new mandates.
Trusted by 1,500+ enterprises · 70+ countries · SOC 2 · ISO 27001
-
1,500+
Clients across 48 countries
-
50%
Of clients in the Fortune 500
-
65%
Of organizations putting more effort into quantification
-
15,000+
Members in the Archer risk community
Non-stop Mandates Keep Landing on Teams Already Stretched Thin.
FedRAMP 20x, CMMC 2.0 enforcement, and evolving FISMA guidance are reshaping federal compliance in 2026, while agencies face the highest ransom demands on record and pressure to do
-
FedRAMP, CMMC, and FISMA rules keep evolving
-
Inaccurate certifications now carry FCA risk
-
Agencies are top targets for ransomware
-
Budgets shrink as mandates keep expanding
Connect certification compliance to the broader risk picture
Archer delivers enterprise capabilities for companies of all sizes.
Connected Compliance and Risk
One connected system of record for federal and state obligations, risks, controls, and issues across every agency.
Test Once/Comply Many
Map controls to frameworks once, test and demonstrate compliance to satisfy overlapping requirements automatically.
Defensibility in AI Automation
Every control in Archer links back to the exact FedRAMP, CMMC, or FISMA requirement it satisfies, and every AI output goes through Expert-in-the-Loop review.
AI powered GRC built for the way risk teams actually work
Archer is specifically designed to meet the needs of GRC teams and business users.
1
One connected platform
Retire the patchwork of spreadsheets and point tools with a single system of record.
2
Automation that scales
Automate using AI purpose-built for risk and compliance processes.
3
Framework coverage
Map controls once and satisfy overlapping regulatory frameworks automatically.
4
Continuous compliance
Replace periodic assessments with ongoing compliance testing for immediate visibility into gaps.
5
Cross-team alignment
Give risk, compliance, and audit a shared, real-time view of the program.
6
Enterprise-grade trust
FedRAMP, SOC 2 and ISO 27001 controls, granular permissions, and full audit trails.
Explore how Archer works across every compliance use case you own
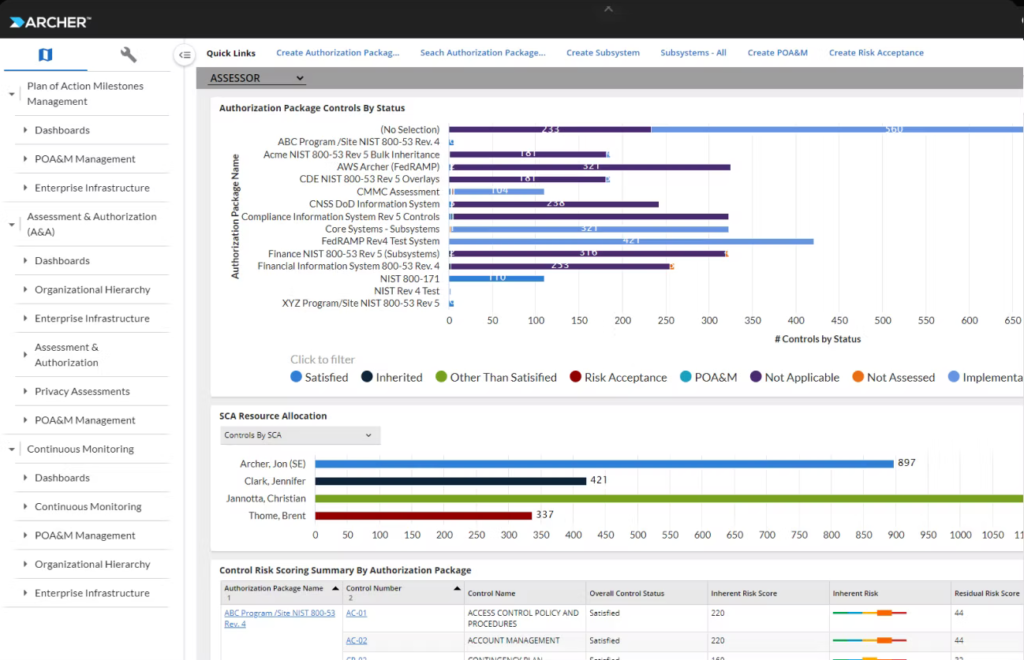
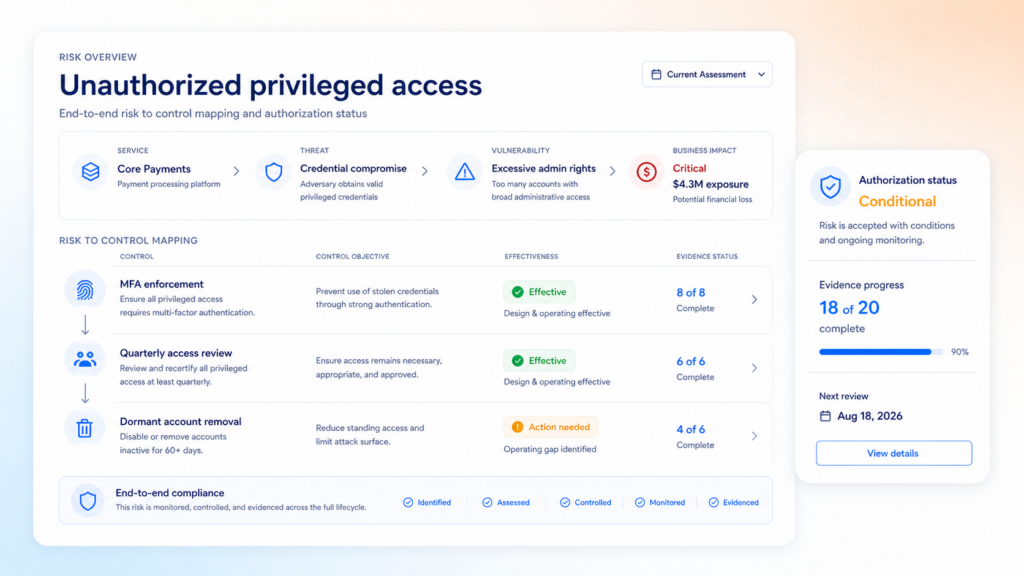
Assessment and Authorization
Comply with FISMA and OMB requirements while improving overall security and controls with a system of record of compliance and lay the foundation for a comprehensive information assurance management program.
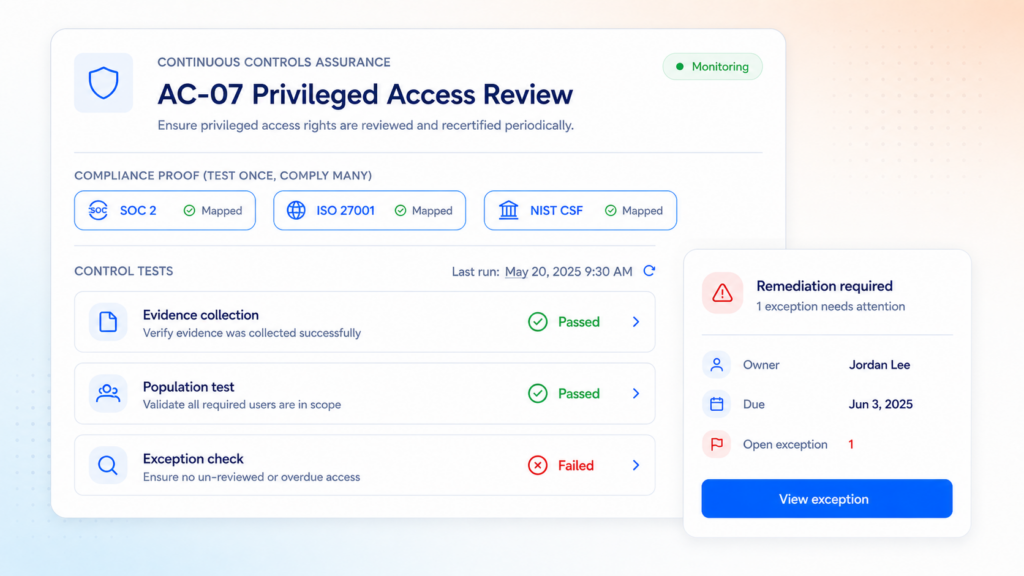
Continuous Controls Monitoring
Prioritize security risk data and automate control assessments building an aggregate risk view at any level of your agency.
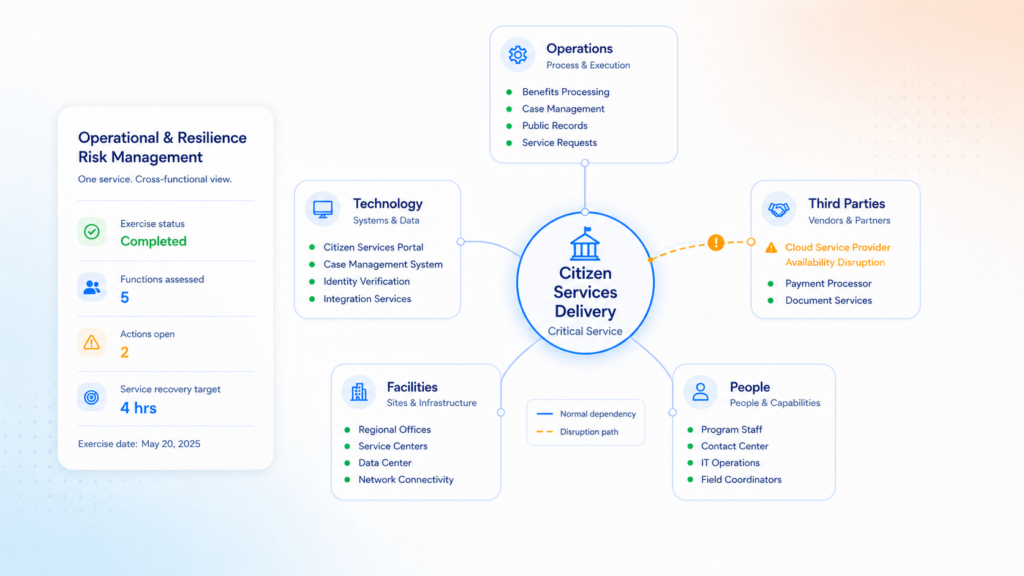
Operational, Vendor and Resilience Risk Management
Build comprehensive risk management practices alongside certification compliance, instead of treating IT security as the only risk that gets tracked.
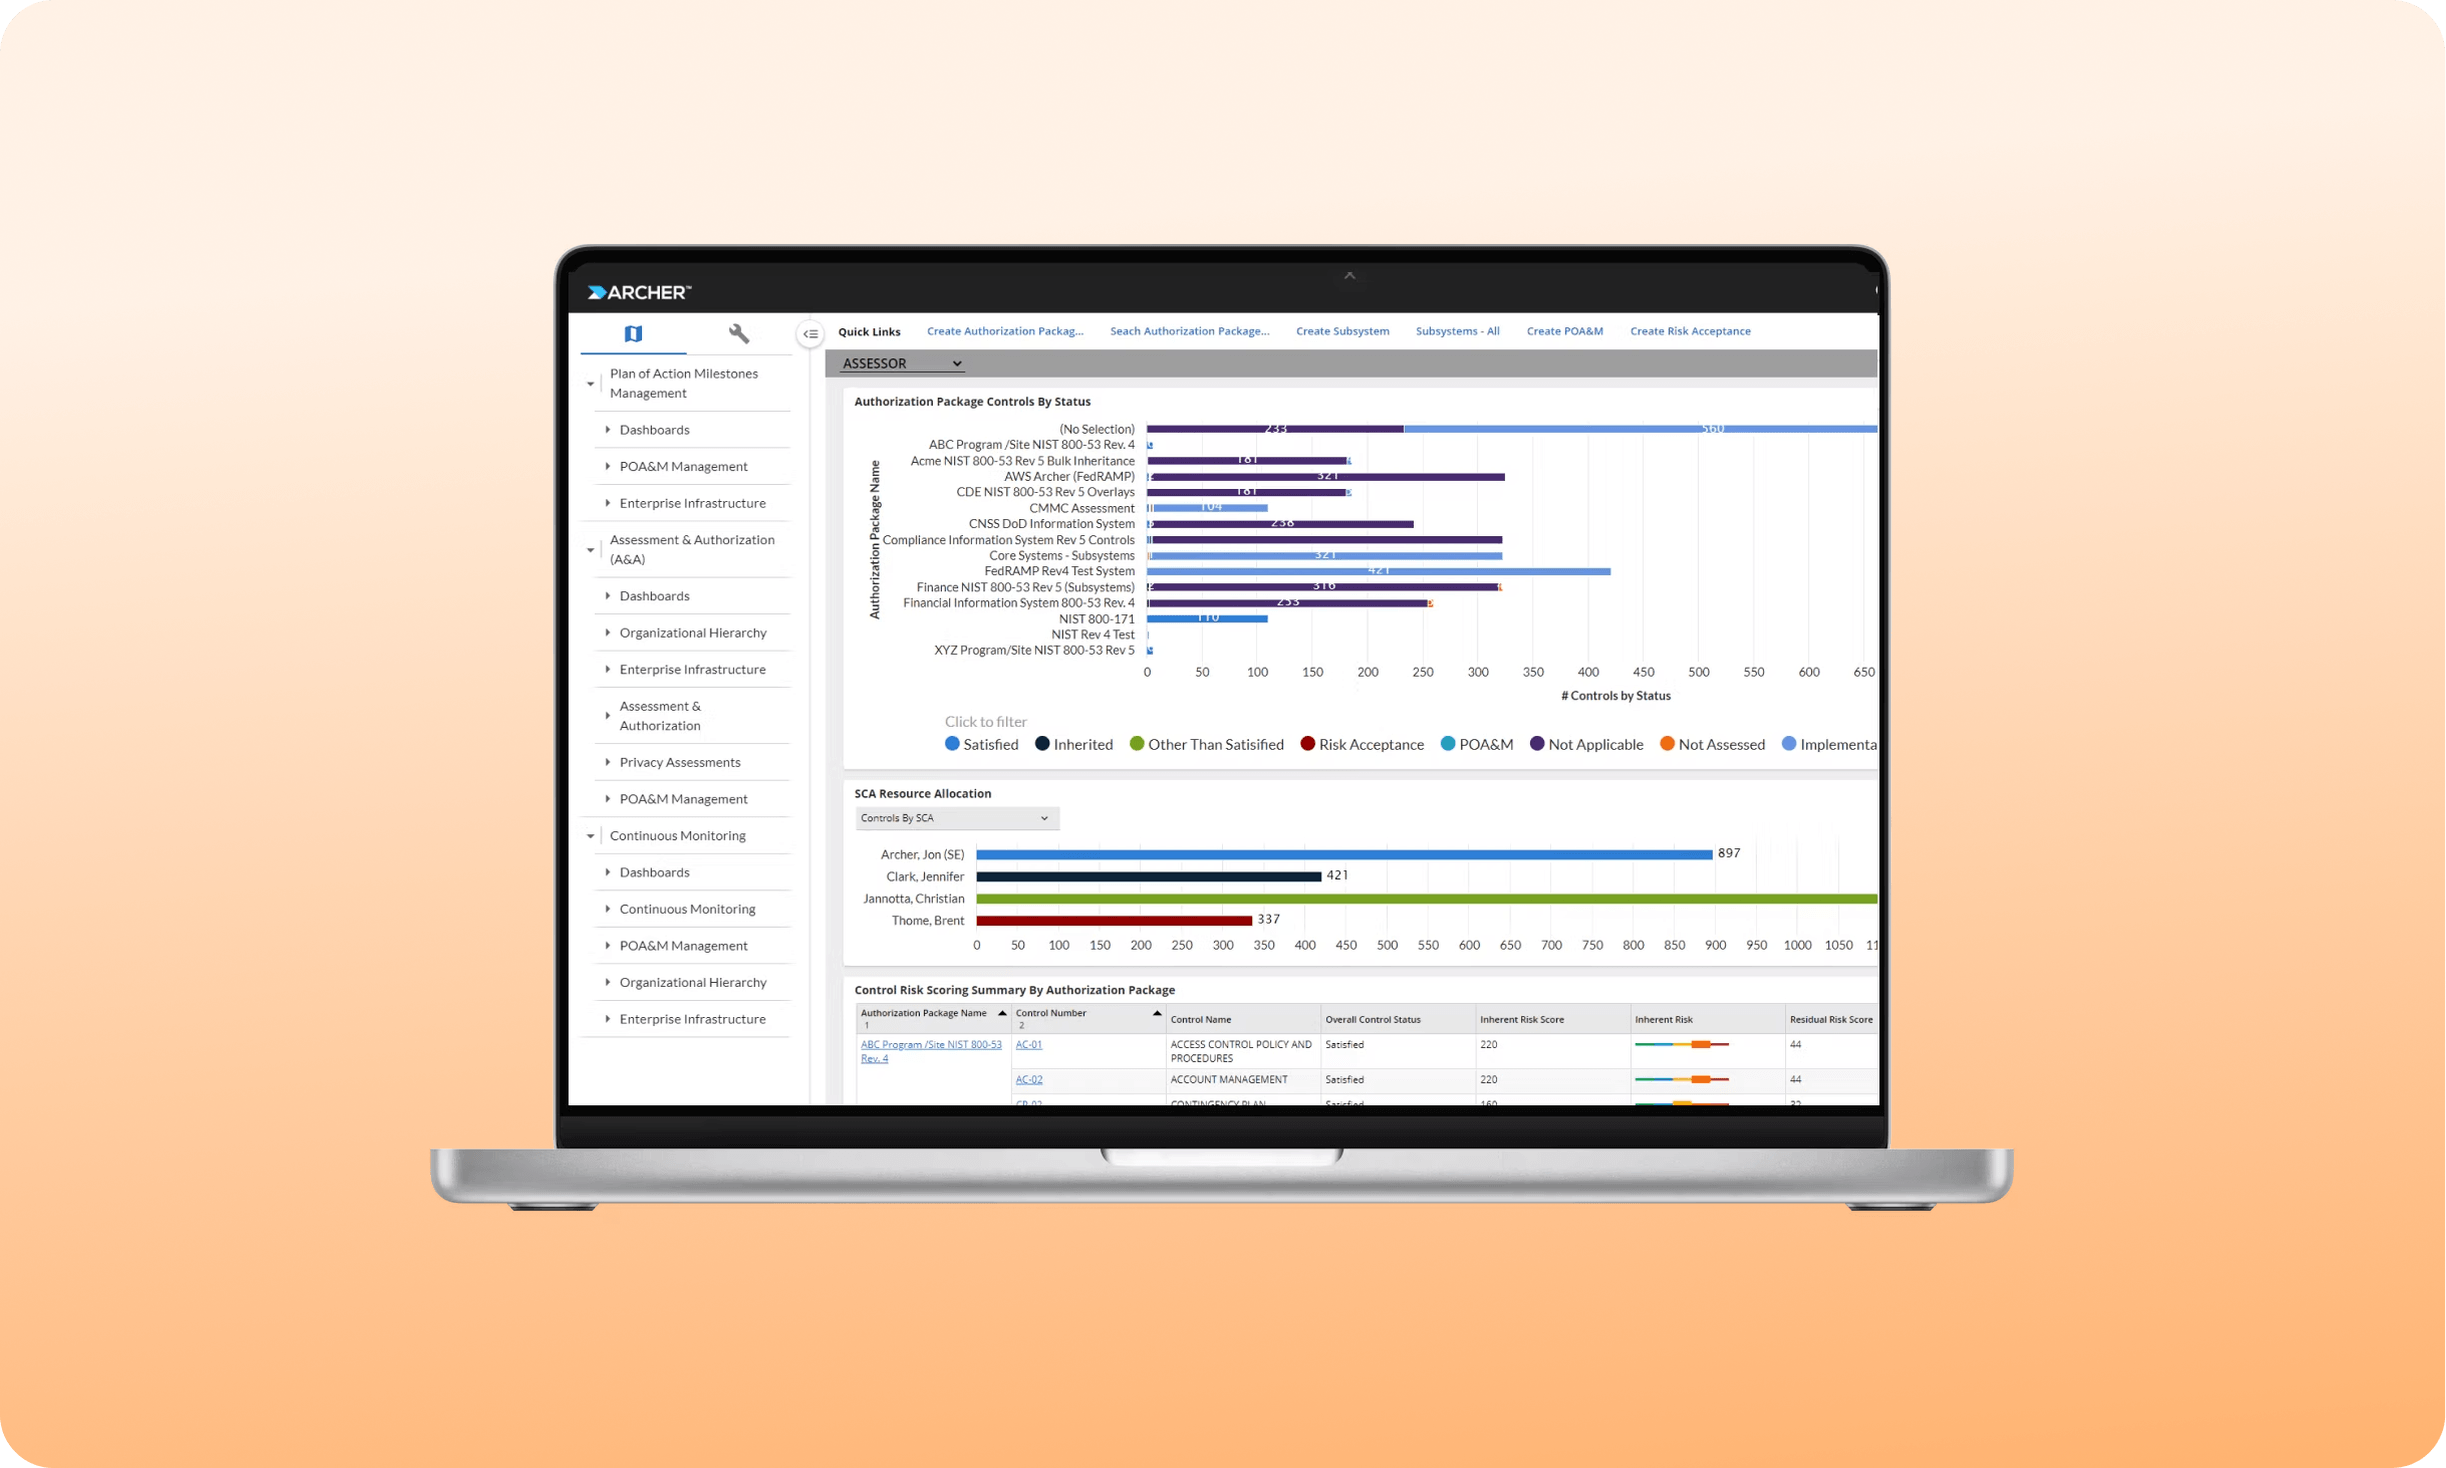
The images used above are not actual product screenshots.
What your agency gains with Archer
Archer enables an integrated strategy across your risk and compliance functions.
-
Faster audits
Reduce audit preparation time by reusing evidence and automating collection workflows.
-
Fewer surprises
Continuous monitoring identifies emerging risks before they become compliance gaps or incidents.
-
Lower tooling cost
Consolidate multiple GRC tools into one platform and reduce IT operational spending.
-
Accuracy and defensibility
Maintain auditable records that withstand inspector scrutiny and regulatory review.
-
Confident compliance
Meet compliance obligations without expanding your team or budget.
-
Certification-ready reporting
Deliver clear, auditable compliance records to oversight bodies and agency partners.
How Archer compares to generic tools
See how Archer GRC stacks up against generic tools and custom enterprise builds.
Other GRC Tools
Basic coverage for teams just getting started.
Here’s what you get
-
Preset frameworks
-
Custom permissions
-
Custom infrastructure
Archer GRC
Built for teams that need real-time visibility and control.
Here’s what you get
-
Pre-built risk templates
-
Native integrations (200+)
-
Automated evidence collection
-
Cross-framework control mapping
-
Real-time executive dashboards
-
AI-assisted risk scoring
-
Multi-tenant SaaS deployment
DIY Compliance
Spreadsheets, shared drives, and tribal knowledge.
Here’s what you get
-
Manual tracking
-
Custom infrastructure
-
Custom updates
Explore Our Case Studies
Eastern Bank Uses Archer to Drive Business Processes and Streamline Compliance
- View case study:
- View case study: Banorte Bank Gains Accurate Picture of Risk with Archer
- View case study: Intuitive Surgical Migrated to Archer SaaS for their journey to empowered risk management
- View case study: Operational Resilience for Financial Services Institutions
More than 1,500 organizations run on Archer®, including half the Fortune 500 and 37 of the top 50 global banks. See what their teams were up against, what they built, and what changed.
Eastern Bank Uses Archer to Drive Business Processes and Streamline Compliance
Banorte Bank Gains Accurate Picture of Risk with Archer
Intuitive Surgical Migrated to Archer SaaS for their journey to empowered risk management
Operational Resilience for Financial Services Institutions
Trusted by the teams who carry the risk
Risk, compliance, and audit leaders on what changed after Archer Evolv was implemented.
We recognized the need for a GRC software platform that would be central to our ability to improve and transform our enterprise risk and compliance processes.
Archer is the source of truth, and it creates a nice audit trail for us. As an insurance company, we're audited by every governmental entity. Now we can say, here's our repository, take a look.
Risk aggregation is a big point for us, to see where our risk is located within the organization, and to give greater visibility for boards and executives.
Turkcell is using Archer as the main GRC tool in the company. It provides us a transparent and safe governance framework.
Archer gives us the ability to boil things down into numbers and specifics versus generalities. It's management by fact versus intuition or feel.
It connects all the different applications together, so you can use those cross-references and connections to make better business decisions, because you have it all in one place.
Questions we hear most often
Straight answers to what enterprise risk and compliance teams ask before choosing Archer.
Most enterprise deployments go live in 8–12 weeks. Pre-built frameworks and templates mean you start configuring, not building from scratch.
Yes. Archer offers 200+ native integrations across security, ITSM, cloud, and ERP systems, plus an open API for anything custom.
Archer ships mapped to NIST, ISO 27001, SOC 2, PCI DSS, and dozens more, with cross-framework control mapping so one control satisfies many requirements.
Both. Archer runs as a multi-tenant SaaS platform or in a private/on-premise configuration to meet your data residency and security requirements.
Pricing scales with modules, users, and deployment model. Contact sales for a tailored quote built around your program’s scope.