Digital workers for GRC that show their work
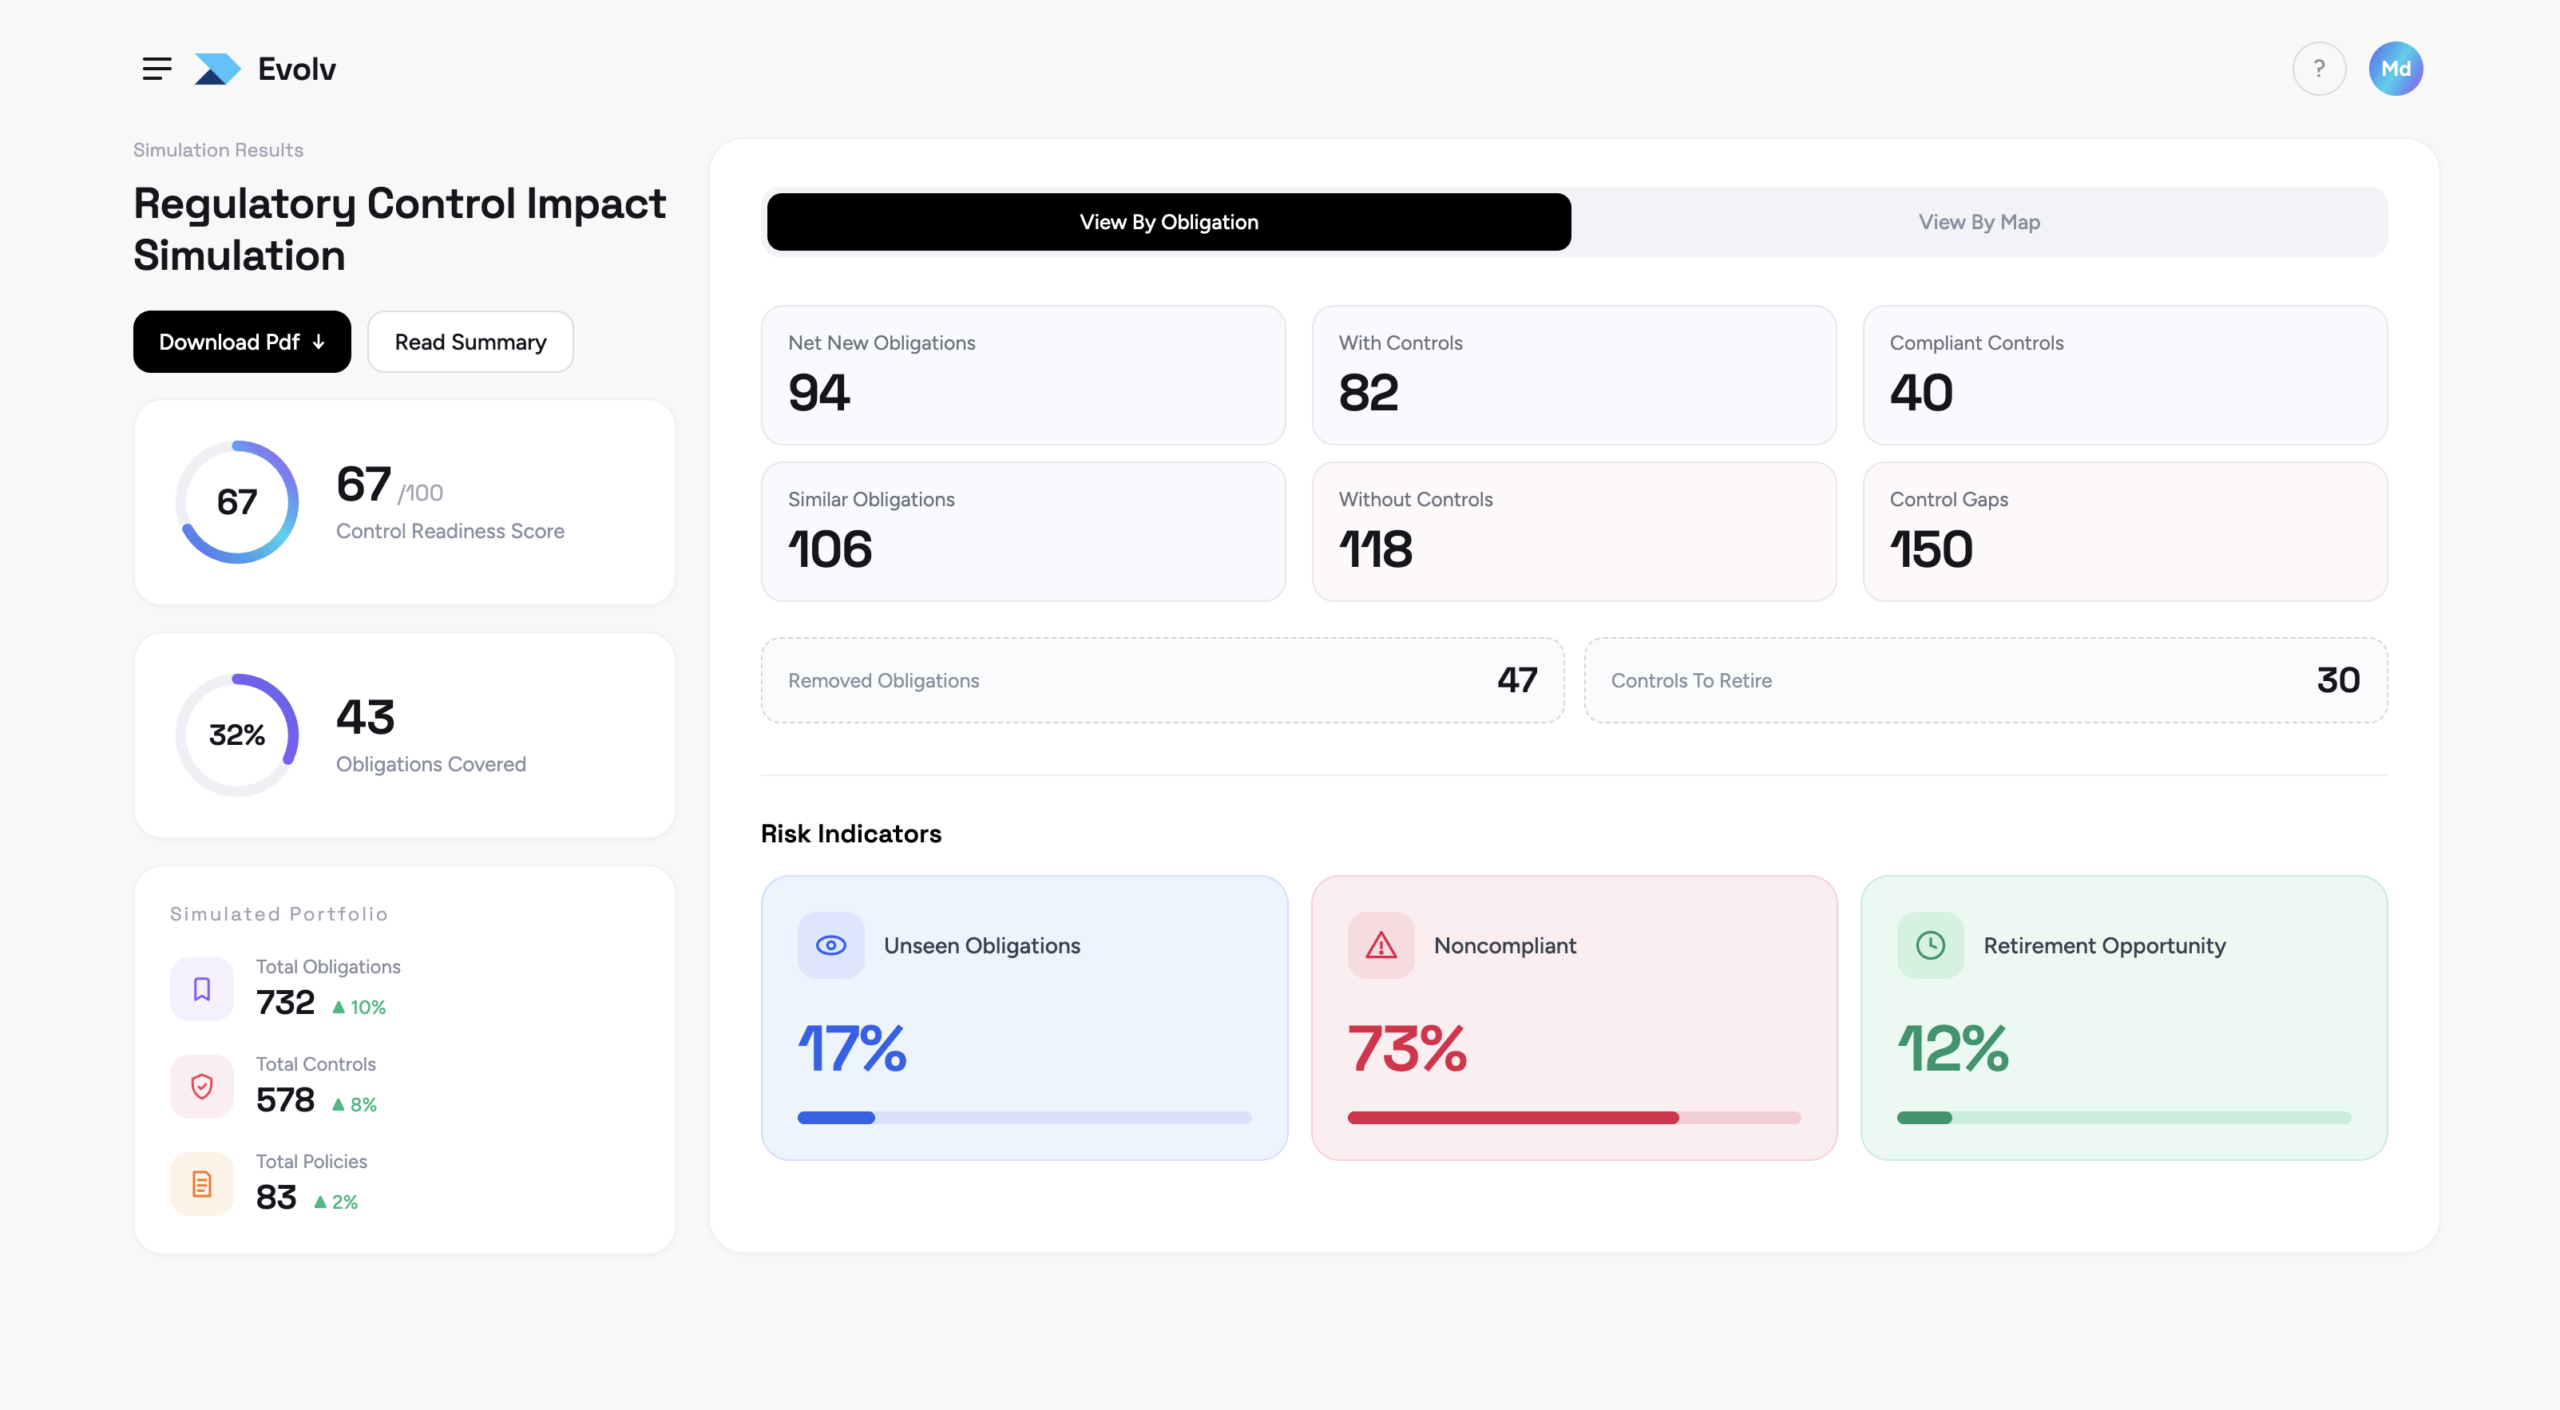
Archer Evolv Workplace puts AI Operators to work inside Archer—each on one job, under your supervision.
AI Operators are governed digital workers built for specific GRC jobs: intake, analysis, decision reasoning, expert approval, and audit-trail writebacks. Each Operator does the gathering and first pass. Your experts own the judgment. Nothing writes back to Archer without a named human approving it, and every action logs in an immutable audit record.
Built for complex, regulated enterprises · 25+ years in GRC · Trusted by 1,500 organizations across 70+ countries
-
43
Operators available now
-
200+
Planned by the end of 2026
-
1,500+
Organizations trust Archer
-
半分
フォーチュン500にランクインする企業の顧客のうち
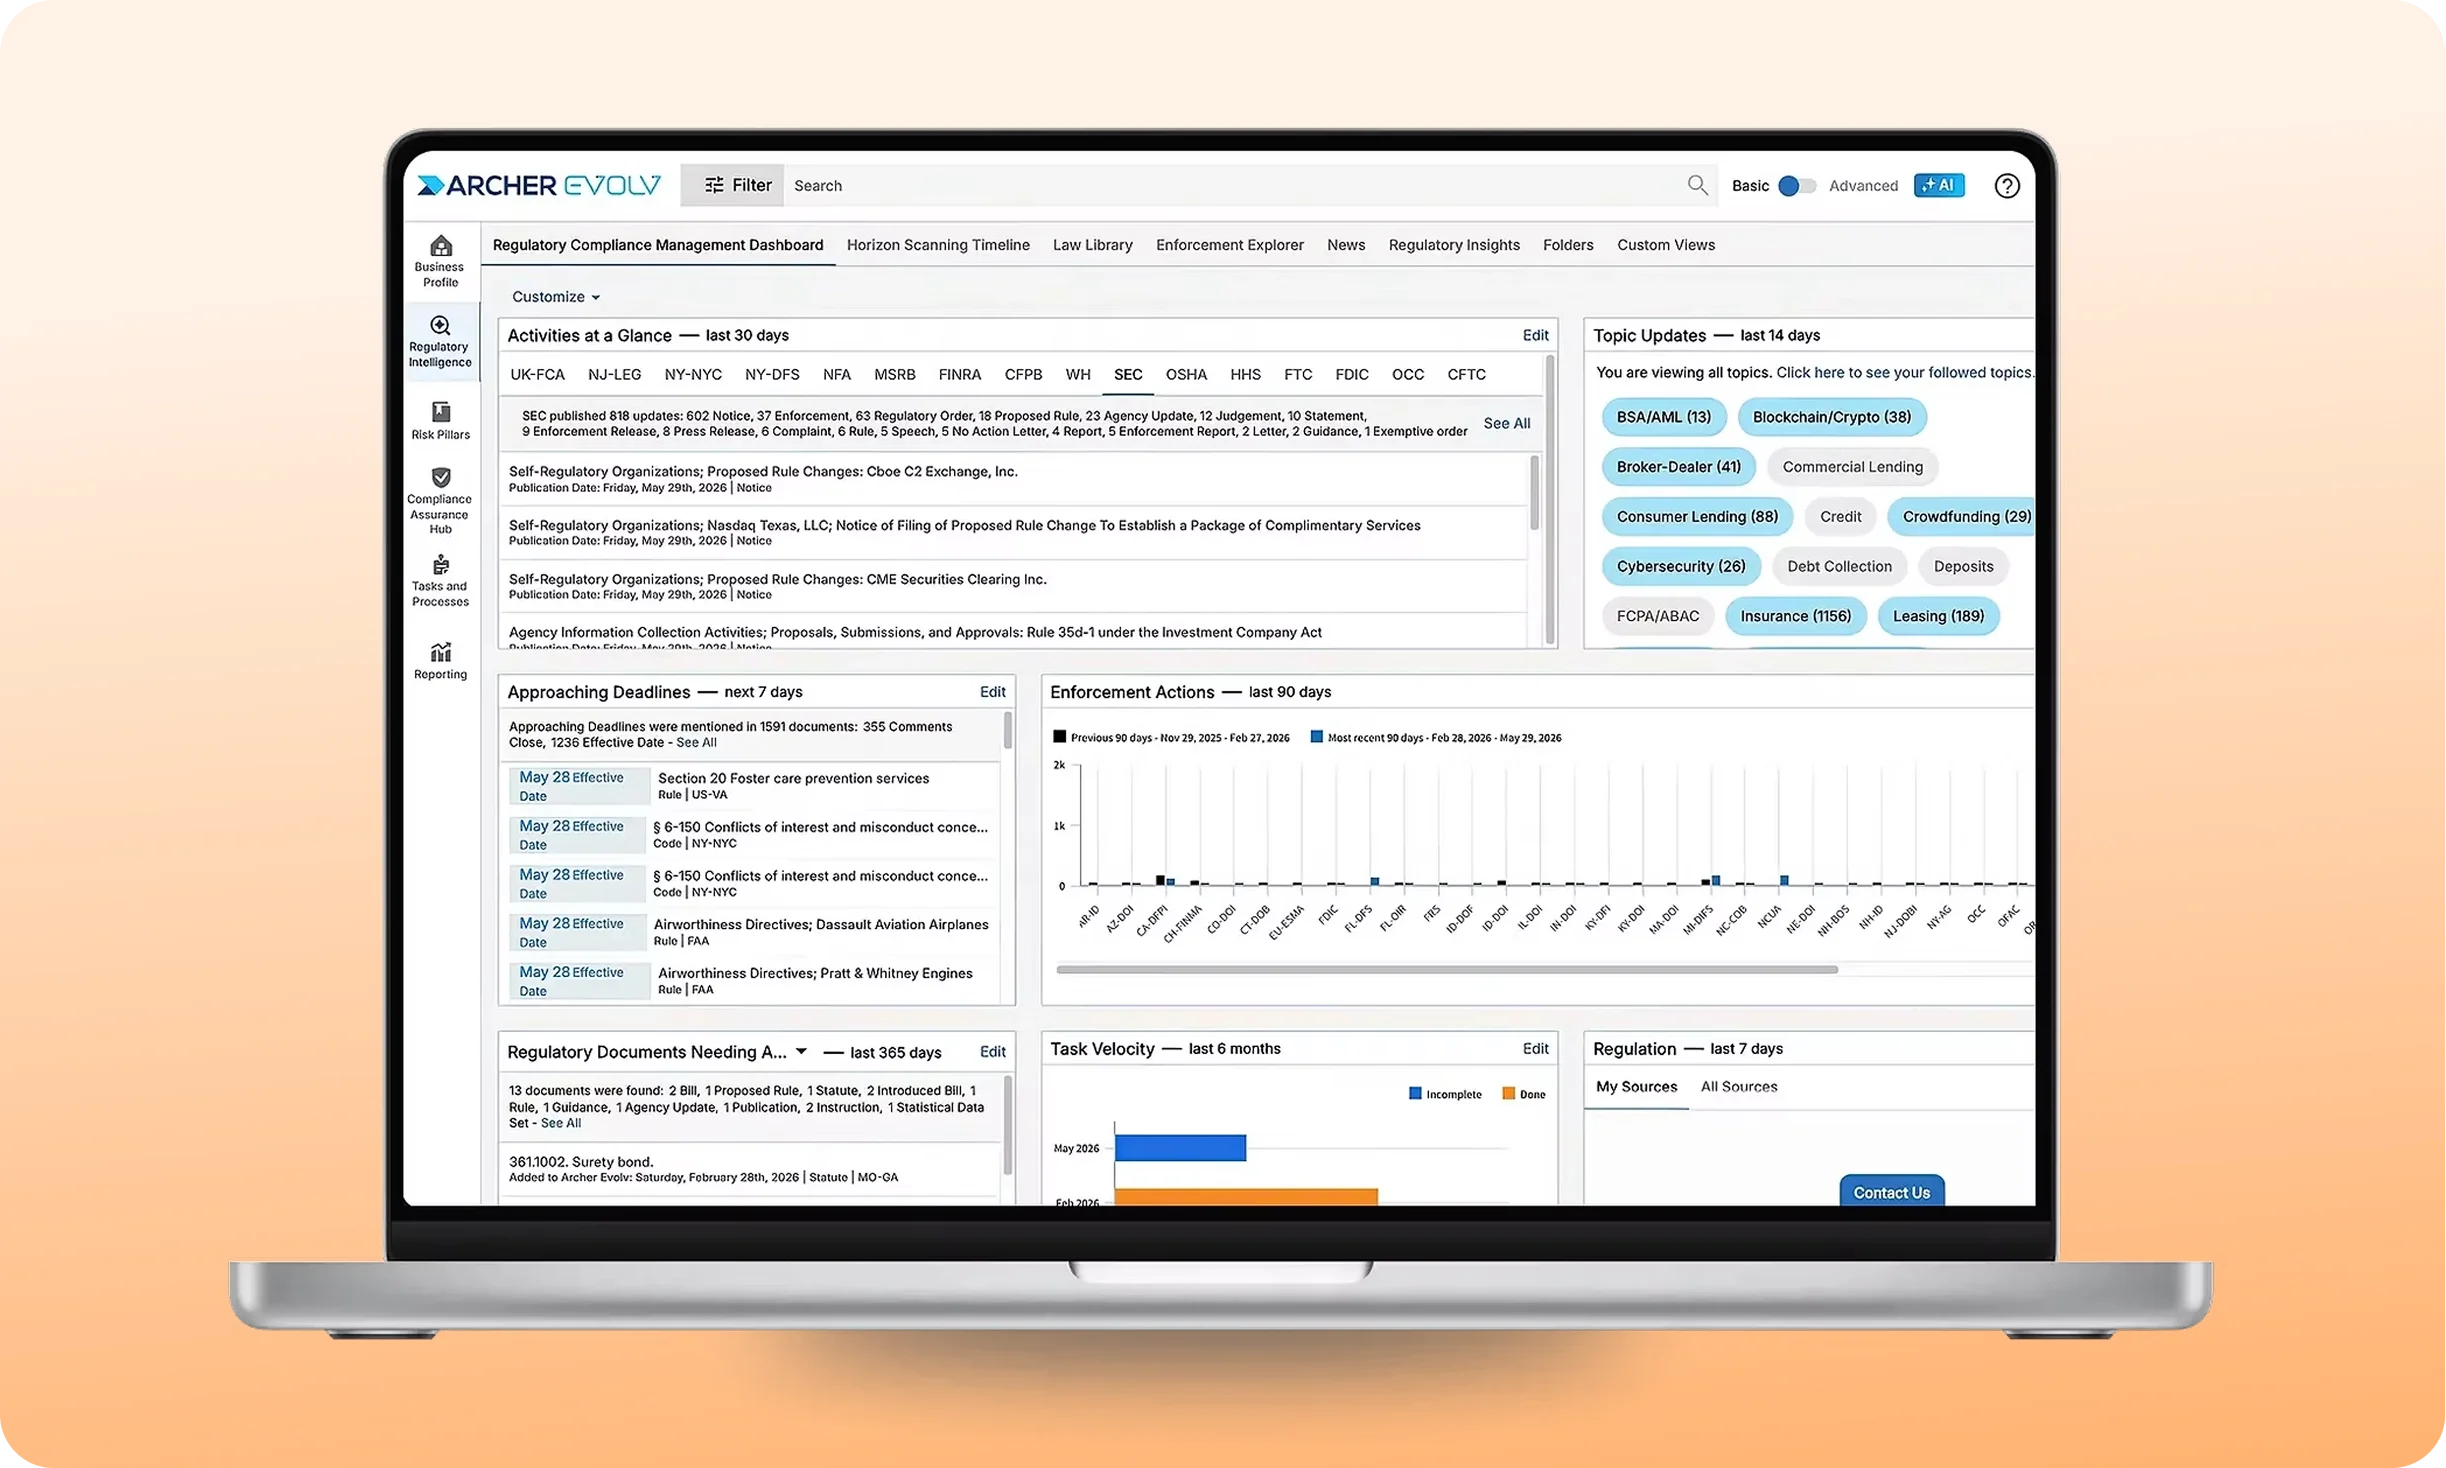
Governed by design, not added after the fact.
For productivity, a generic AI agent can be enough. For control in a regulated environment, you need identity, limits, justification, and an expert in the loop to be part of how the work runs.
Same Archer. Same data. More value with every layer.
Operators sit in the third layer. They work on the governed record you already run in Archer, so none of this requires a migration.
-
アーチャーGRC
The governed foundation your team already runs: risks, controls, policies, workflows, and the roles and permissions around them.
-
Archer Evolv™ Foundation
AI-native access to that record in plain language, with cited answers and cleaner records underneath.
-
Evolv Workplace + AI Compliance
Governed AI Operators and enforceable AI controls that turn intelligence into action, supervised by your people.
Put governed AI to work on the GRC jobs that matter most.
From managing enterprise and third-party risk to accelerating audits and strengthening compliance, Archer Evolv AI Operators reduce manual work, deliver actionable intelligence, and drive better business outcomes with built-in AI governance and controls.
1
CRO or Risk Lead
Get a clearer picture of enterprise and third-party risk.
Duplicate vendor records and fragmented risk data create extra work and can hide emerging issues. AI Operators help clean up records, assess risks and give teams better information to act on.
Featured Operators: Vendor Profile De-duplication, Risk Scoring, Emerging Risk Detection.
2
CISO Office
Put AI governance into practice.
Understand where AI is being used across the organization, assess the associated risks and establish appropriate guardrails. Give teams the oversight they need to deploy AI responsibly.
Featured Operators: AI Asset Intake, Risk Context, Guardrail Seeding.
3
CCO or Compliance Lead
Move from obligations to action faster.
Identify relevant obligations, generate control procedures and document the reasoning behind decisions. Reduce manual analysis while making compliance work easier to manage and review.
Featured Operators: Obligation Extraction, Control Procedure Generation, Auditable Decision Reasoning.
4
Head of Audit
Accelerate audits from planning through remediation.
Reduce time spent gathering evidence, reviewing documentation and tracking findings. AI Operators help audit teams identify issues earlier, streamline assessments and focus more time on the risks that matter.
Featured Operators: Engagement Scoping Curation, Automated Workpapers and Test Procedures, Audit Automated Findings.
From trusted GRC data to governed action.
Whether it’s improving data quality, assessing third-party risk, preparing for audits or identifying emerging risks, Archer Evolv AI Operators help teams get more work done. All are supported by a shared Foundation that provides the GRC context, governance and controls needed to operate with confidence.
-
AI Risk
AI governance
AI Asset Intake and Classification · AI Risk Context · Guardrail Seeding · Governance Oversight
-
ITリスク
Asset management
IT Asset Initiation · Risk Scoring Assistant · Control Alignment and Evidence Sync
-
オペレーショナル・リスク
Risk registers
Control Hygiene · Emerging Risk Detection · Scoring and Recalibration Assistant
-
コンプライアンス
Regulatory work
Obligation Extraction and Classification · Control Procedure Generation · Auditable Decision Reasoning
-
サードパーティ・リスク
Vendor management
Vendor Profile De-duplication · Risk Scoring and Posture Evaluation · Emerging Risk Detection
-
監査
Assurance
Audit Engagement Renewal · Automated Finding Generation · Continuous Auditor
Three ways to put governed AI to work.
You do not have to deploy everything at once. Start with the pressure your team feels most today.
-
Archer Evolv™ FoundationIf your challenge is getting trusted answers from complex Archer data, make governed GRC data easier to query, understand, and improve.
-
Archer Evolv™ Workplace
If your teams are stretched across risk and compliance work, assign governed AI Operators to defined jobs while people keep judgment and approval.
-
Archer Evolv™ AIコンプライアンス
If employees and agents are already using AI, translate approved regulations and policies into runtime guardrails and keep the evidence behind enforcement.
Different starting points. One governed Archer foundation.
Whether you own the compliance program as CCO or head of regulatory compliance, report on it as CRO, test it as head of internal audit, or manage it day to day as head of OT and cyber security, there’s a specific answer for your role. Tell us where you sit and we’ll start there.
この会話で何が期待できるか:
-
Clarity on how cyber and OT findings connect to operational risk.
-
An honest look at how third-party and supplier risk is tracked.
-
Proof points specific to your role, from board reporting for CRO to evidence for audit.
アナリスト界隈で広く認められている。
25 years of purpose-built GRC depth, not general platform breadth.
-
2
ガートナー® マジック・クアドラント™:ガバナンス、リスク、コンプライアンス(GRC)ツール、アシュアランス分野のリーダー
-
3
Forrester Wave™:サードパーティ・リスク管理プラットフォーム、2026年第1四半期
-
4
Verdantix グリーンスクエア:GRCソフトウェア 2025
チームから寄せられる質問
Straight answers before you level up.
No. Operators handle the gathering and the first pass. Your experts own the decision, and anything below the confidence threshold you set goes to a named reviewer first.
No. Archer Evolv connects to your Archer GRC, SaaS or on-prem, in days. Your ODAs, customizations, integrations and permissions stay as they are.
Operators are consumption-based: you pay for jobs completed, not tokens used. Your Archer representative can walk through what that looks like for your volume.
Start with the job that costs your team the most time today. Different operators fit different pressures.
AI Compliance runs standalone. Foundation and Workplace are built on the Archer record, so they get stronger the more of your program already lives there.