Digital workers for GRC that show their work
Archer Evolv Workplace puts AI Operators to work inside Archer—each on one job, under your supervision.
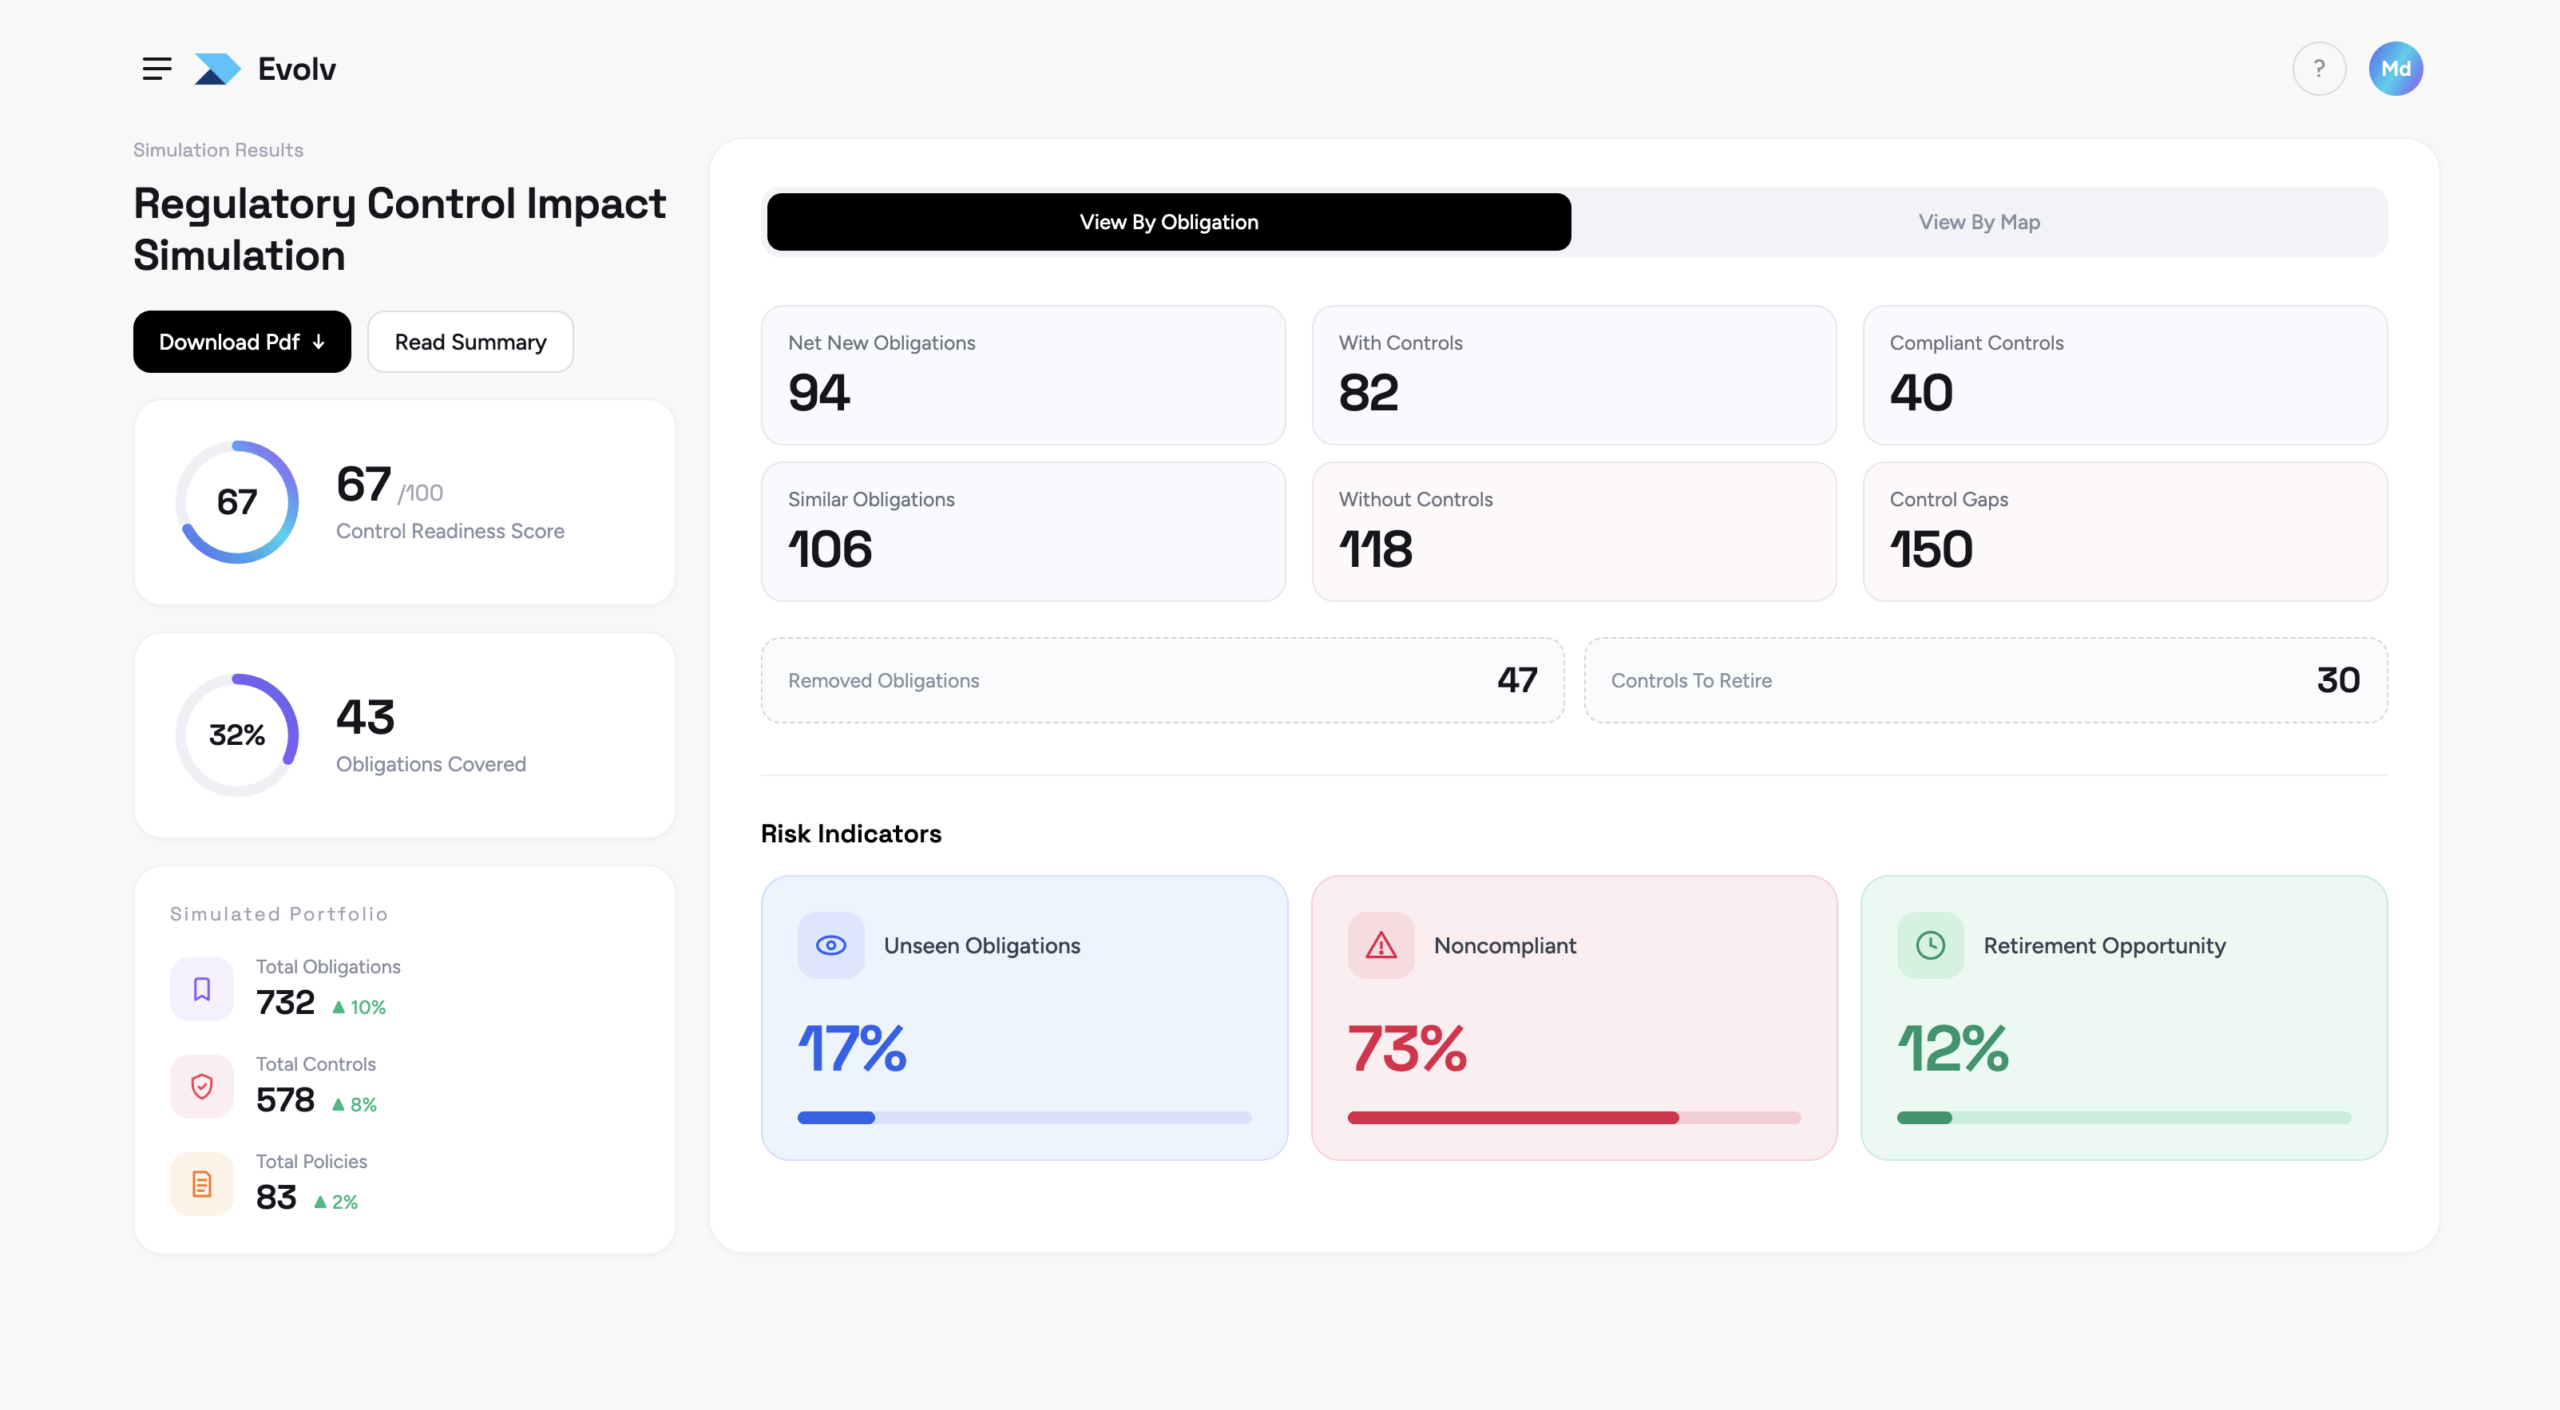
AI Operators are governed digital workers built for specific GRC jobs: intake, analysis, decision reasoning, expert approval, and audit-trail writebacks. Each Operator does the gathering and first pass. Your experts own the judgment. Nothing writes back to Archer without a named human approving it, and every action logs in an immutable audit record.
Entwickelt für komplexe, regulierte Unternehmen · Über 25 Jahre Erfahrung im Bereich GRC · 1.500 Organisationen in über 70 Ländern vertrauen auf uns
-
43
Operators available now
-
200+
Planned by the end of 2026
-
1,500+
Organizations trust Archer
-
Die Hälfte
Von den Kunden der Fortune-500-Unternehmen
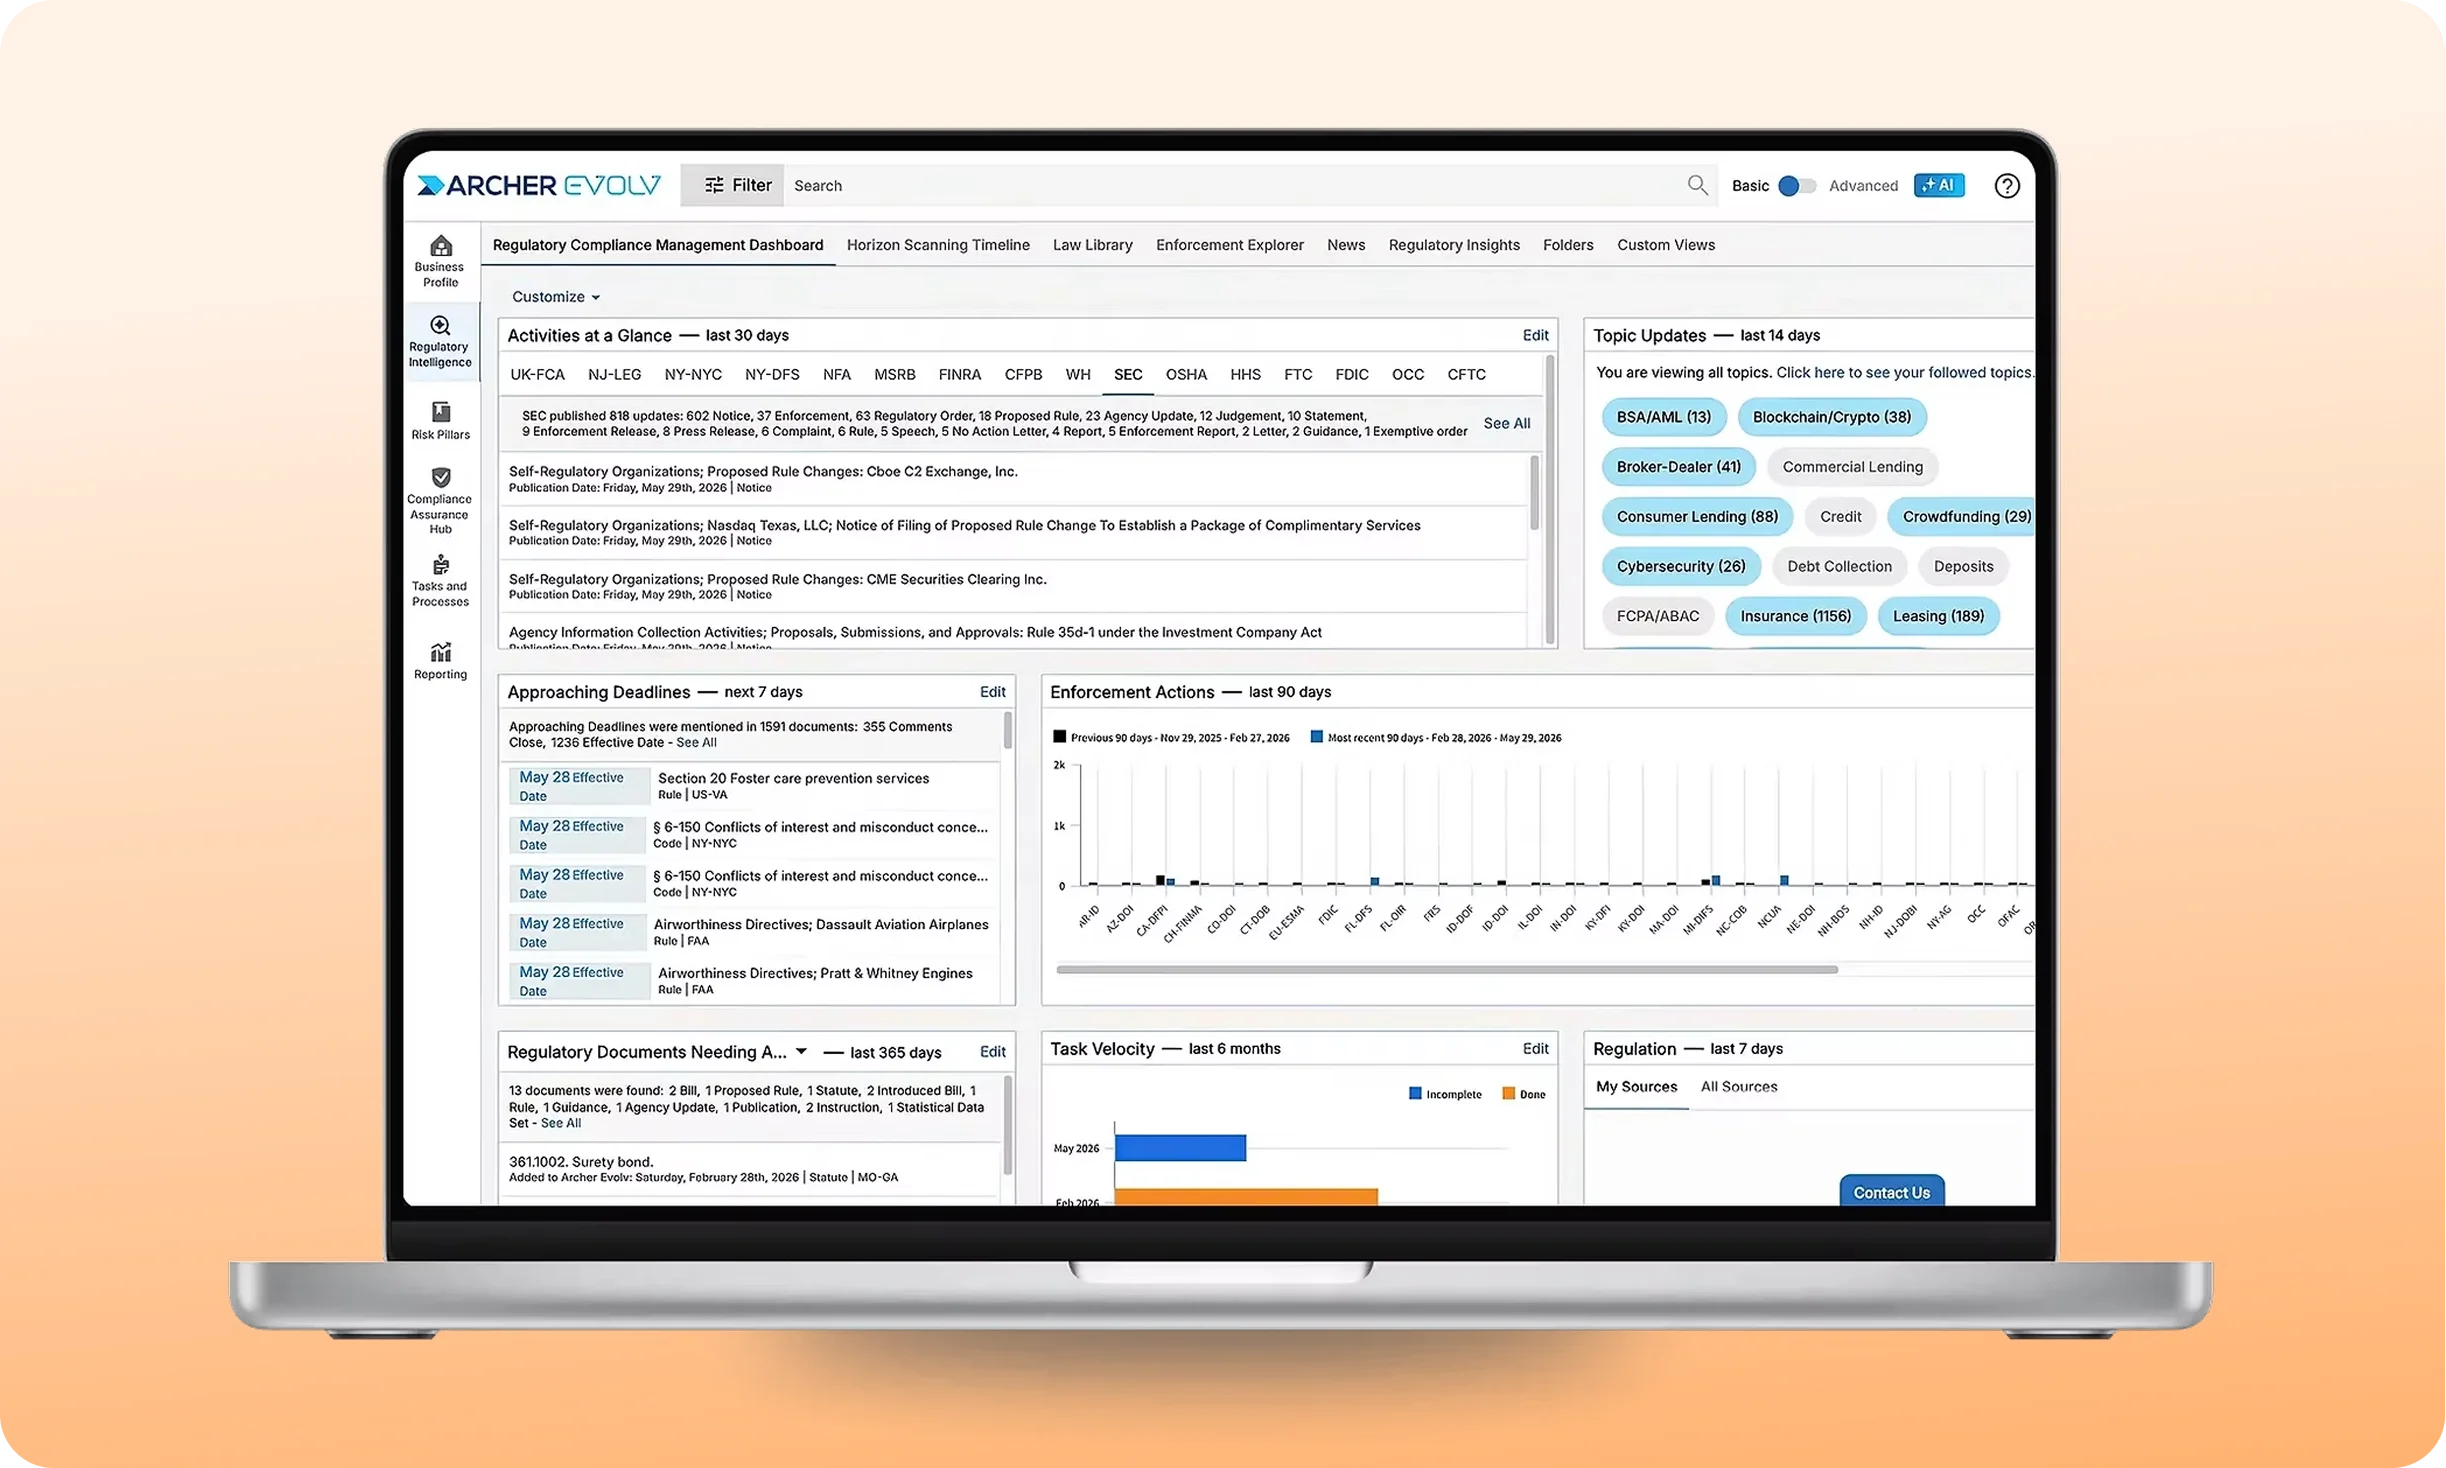
Governed by design, not added after the fact.
For productivity, a generic AI agent can be enough. For control in a regulated environment, you need identity, limits, justification, and an expert in the loop to be part of how the work runs.
Same Archer. Same data. More value with every layer.
Operators sit in the third layer. They work on the governed record you already run in Archer, so none of this requires a migration.
-
Archer GRC
The governed foundation your team already runs: risks, controls, policies, workflows, and the roles and permissions around them.
-
Archer Evolv™ Foundation
AI-native access to that record in plain language, with cited answers and cleaner records underneath.
-
Evolv Workplace + AI Compliance
Governed AI Operators and enforceable AI controls that turn intelligence into action, supervised by your people.
Put governed AI to work on the GRC jobs that matter most.
From managing enterprise and third-party risk to accelerating audits and strengthening compliance, Archer Evolv AI Operators reduce manual work, deliver actionable intelligence, and drive better business outcomes with built-in AI governance and controls.
1
CRO or Risk Lead
Get a clearer picture of enterprise and third-party risk.
Duplicate vendor records and fragmented risk data create extra work and can hide emerging issues. AI Operators help clean up records, assess risks and give teams better information to act on.
Featured Operators: Vendor Profile De-duplication, Risk Scoring, Emerging Risk Detection.
2
CISO Office
Put AI governance into practice.
Understand where AI is being used across the organization, assess the associated risks and establish appropriate guardrails. Give teams the oversight they need to deploy AI responsibly.
Featured Operators: AI Asset Intake, Risk Context, Guardrail Seeding.
3
CCO or Compliance Lead
Move from obligations to action faster.
Identify relevant obligations, generate control procedures and document the reasoning behind decisions. Reduce manual analysis while making compliance work easier to manage and review.
Featured Operators: Obligation Extraction, Control Procedure Generation, Auditable Decision Reasoning.
4
Head of Audit
Accelerate audits from planning through remediation.
Reduce time spent gathering evidence, reviewing documentation and tracking findings. AI Operators help audit teams identify issues earlier, streamline assessments and focus more time on the risks that matter.
Featured Operators: Engagement Scoping Curation, Automated Workpapers and Test Procedures, Audit Automated Findings.
From trusted GRC data to governed action.
Whether it’s improving data quality, assessing third-party risk, preparing for audits or identifying emerging risks, Archer Evolv AI Operators help teams get more work done. All are supported by a shared Foundation that provides the GRC context, governance and controls needed to operate with confidence.
-
AI Risk
KI-Governance
AI Asset Intake and Classification · AI Risk Context · Guardrail Seeding · Governance Oversight
-
IT-Risiko
Asset management
IT Asset Initiation · Risk Scoring Assistant · Control Alignment and Evidence Sync
-
Operatives Risiko
Risk registers
Control Hygiene · Emerging Risk Detection · Scoring and Recalibration Assistant
-
Einhaltung der Vorschriften
Regulatory work
Obligation Extraction and Classification · Control Procedure Generation · Auditable Decision Reasoning
-
Risiken durch Dritte
Vendor management
Vendor Profile De-duplication · Risk Scoring and Posture Evaluation · Emerging Risk Detection
-
Prüfung
Assurance
Audit Engagement Renewal · Automated Finding Generation · Continuous Auditor
Three ways to put governed AI to work.
You do not have to deploy everything at once. Start with the pressure your team feels most today.
-
Archer Evolv™ FoundationIf your challenge is getting trusted answers from complex Archer data, make governed GRC data easier to query, understand, and improve.
-
Archer Evolv™ Workplace
If your teams are stretched across risk and compliance work, assign governed AI Operators to defined jobs while people keep judgment and approval.
-
Archer Evolv™ KI-Compliance
If employees and agents are already using AI, translate approved regulations and policies into runtime guardrails and keep the evidence behind enforcement.
Different starting points. One governed Archer foundation.
Ganz gleich, ob Sie als CCO oder Leiter des Bereichs Regulatory Compliance für das Compliance-Programm verantwortlich sind, als CRO darüber Bericht erstatten, als Leiter der internen Revision das Programm prüfen oder als Leiter des Bereichs OT und Cybersicherheit das Tagesgeschäft leiten – für jede Ihrer Rollen gibt es eine passende Lösung. Teilen Sie uns mit, in welcher Funktion Sie tätig sind, und wir machen dort weiter.
Was Sie von dem Gespräch erwarten können:
-
Klarheit darüber, wie sich Erkenntnisse aus den Bereichen Cybersicherheit und OT auf das operationelle Risiko auswirken.
-
Ein ehrlicher Blick darauf, wie Risiken durch Dritte und Lieferanten überwacht werden.
-
Für Ihre jeweilige Rolle relevante Belege, von der Berichterstattung an den Vorstand für den CRO bis hin zu Nachweisen für die Revision.
In der Analystengemeinschaft anerkannt.
25 Jahre Erfahrung mit speziell entwickelten GRC-Lösungen – keine allgemeine Plattformvielfalt.
-
2
Gartner® Magic Quadrant™ für Governance-, Risiko- und Compliance-Tools, führende Anbieter im Bereich Assurance
-
3
Forrester Wave™: Plattformen für das Risikomanagement bei Drittanbietern, 1. Quartal 2026
-
4
Verdantix Green Quadrant: GRC-Software 2025
Fragen, die Ihr Team stellen wird
Straight answers before you level up.
No. Operators handle the gathering and the first pass. Your experts own the decision, and anything below the confidence threshold you set goes to a named reviewer first.
No. Archer Evolv connects to your Archer GRC, SaaS or on-prem, in days. Your ODAs, customizations, integrations and permissions stay as they are.
Operators are consumption-based: you pay for jobs completed, not tokens used. Your Archer representative can walk through what that looks like for your volume.
Start with the job that costs your team the most time today. Different operators fit different pressures.
AI Compliance runs standalone. Foundation and Workplace are built on the Archer record, so they get stronger the more of your program already lives there.