How Do You Operationalize Signal-Driven GRC? A Five-Pillar Guide
Every organization hears signals all the time. A regulator publishes a new rule. An incident report lands in a queue. A customer complains, or a metric starts drifting in the…
Every organization hears signals all the time. A regulator publishes a new rule. An incident report lands in a queue. A customer complains, or a metric starts drifting in the…
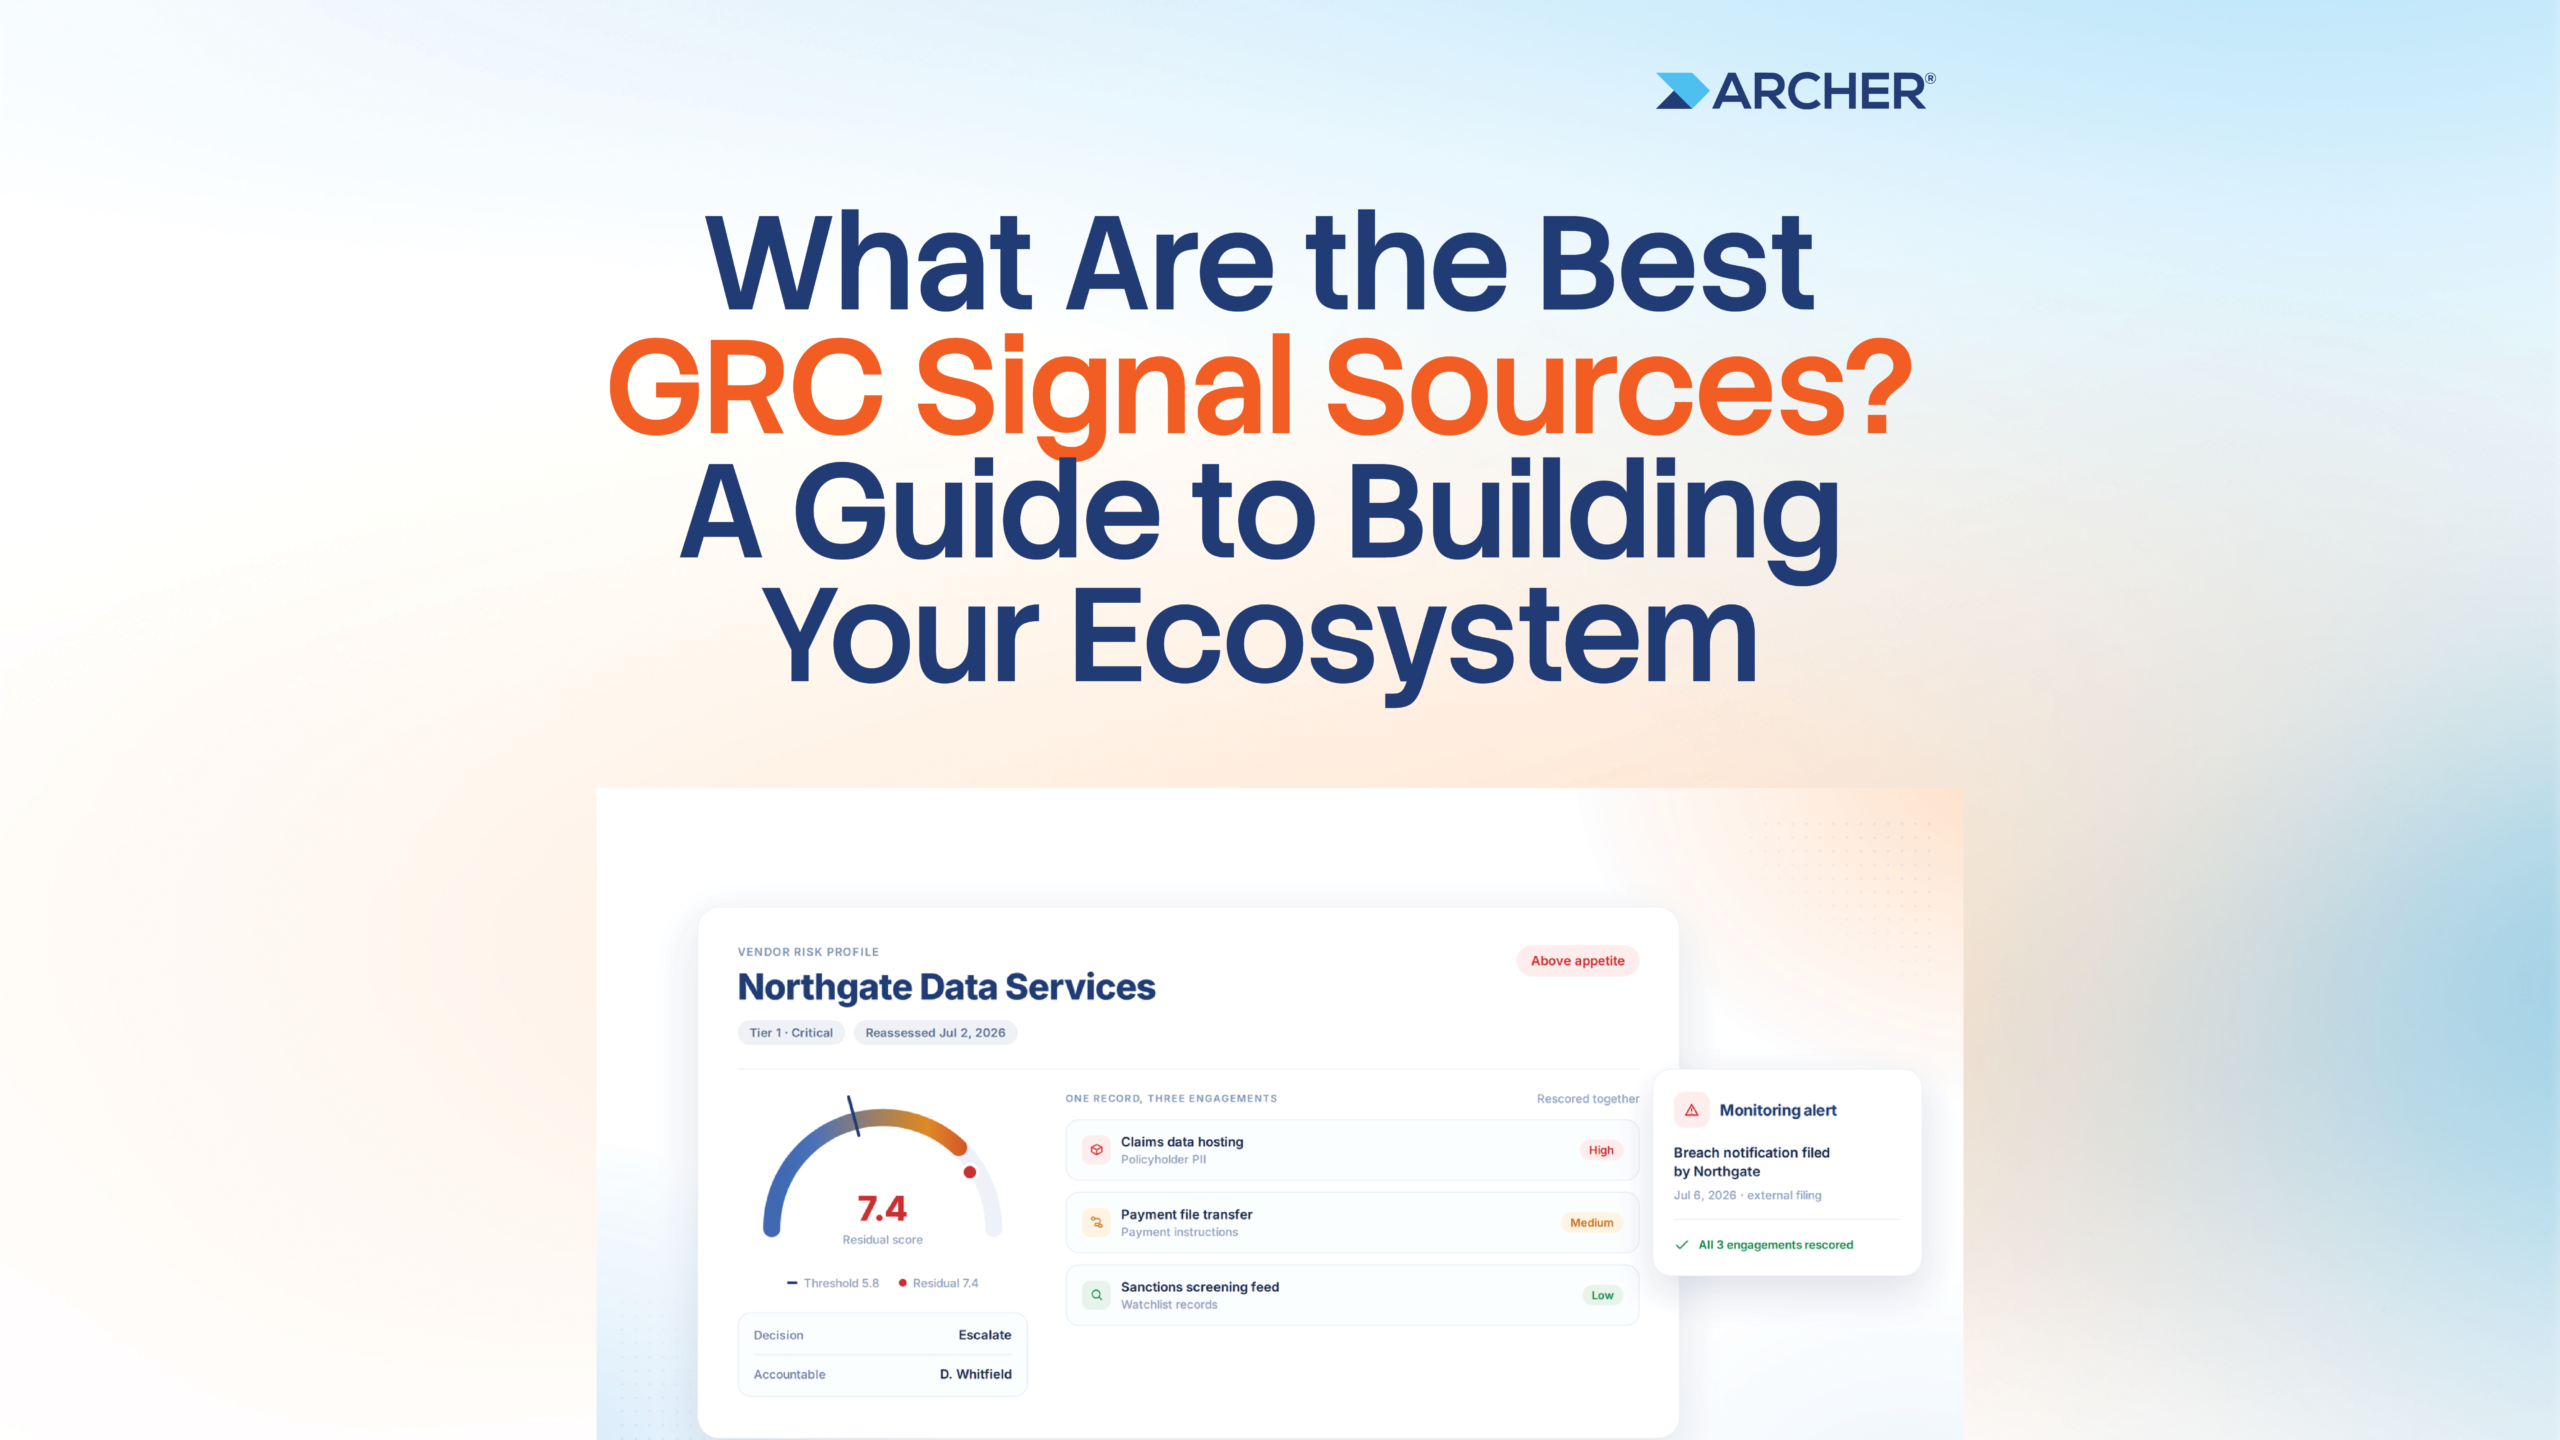
The modern enterprise is surrounded by more information than any risk function in history. Signals come from governments, regulators, hackers, competitors, activists, journalists, markets, algorithms, customers, and the organization’s own…
If you’ve ever watched a thriller, you know the moment. Before the crisis breaks, there’s always a faint indicator: a brief radio intercept, a coded message, a fragment of overheard…
Written by Rossano Magro, Archer’s Sales Director for South Europe There’s a point in every transformation where the conversation has to shift. The vision has been defined, the technology selected,…
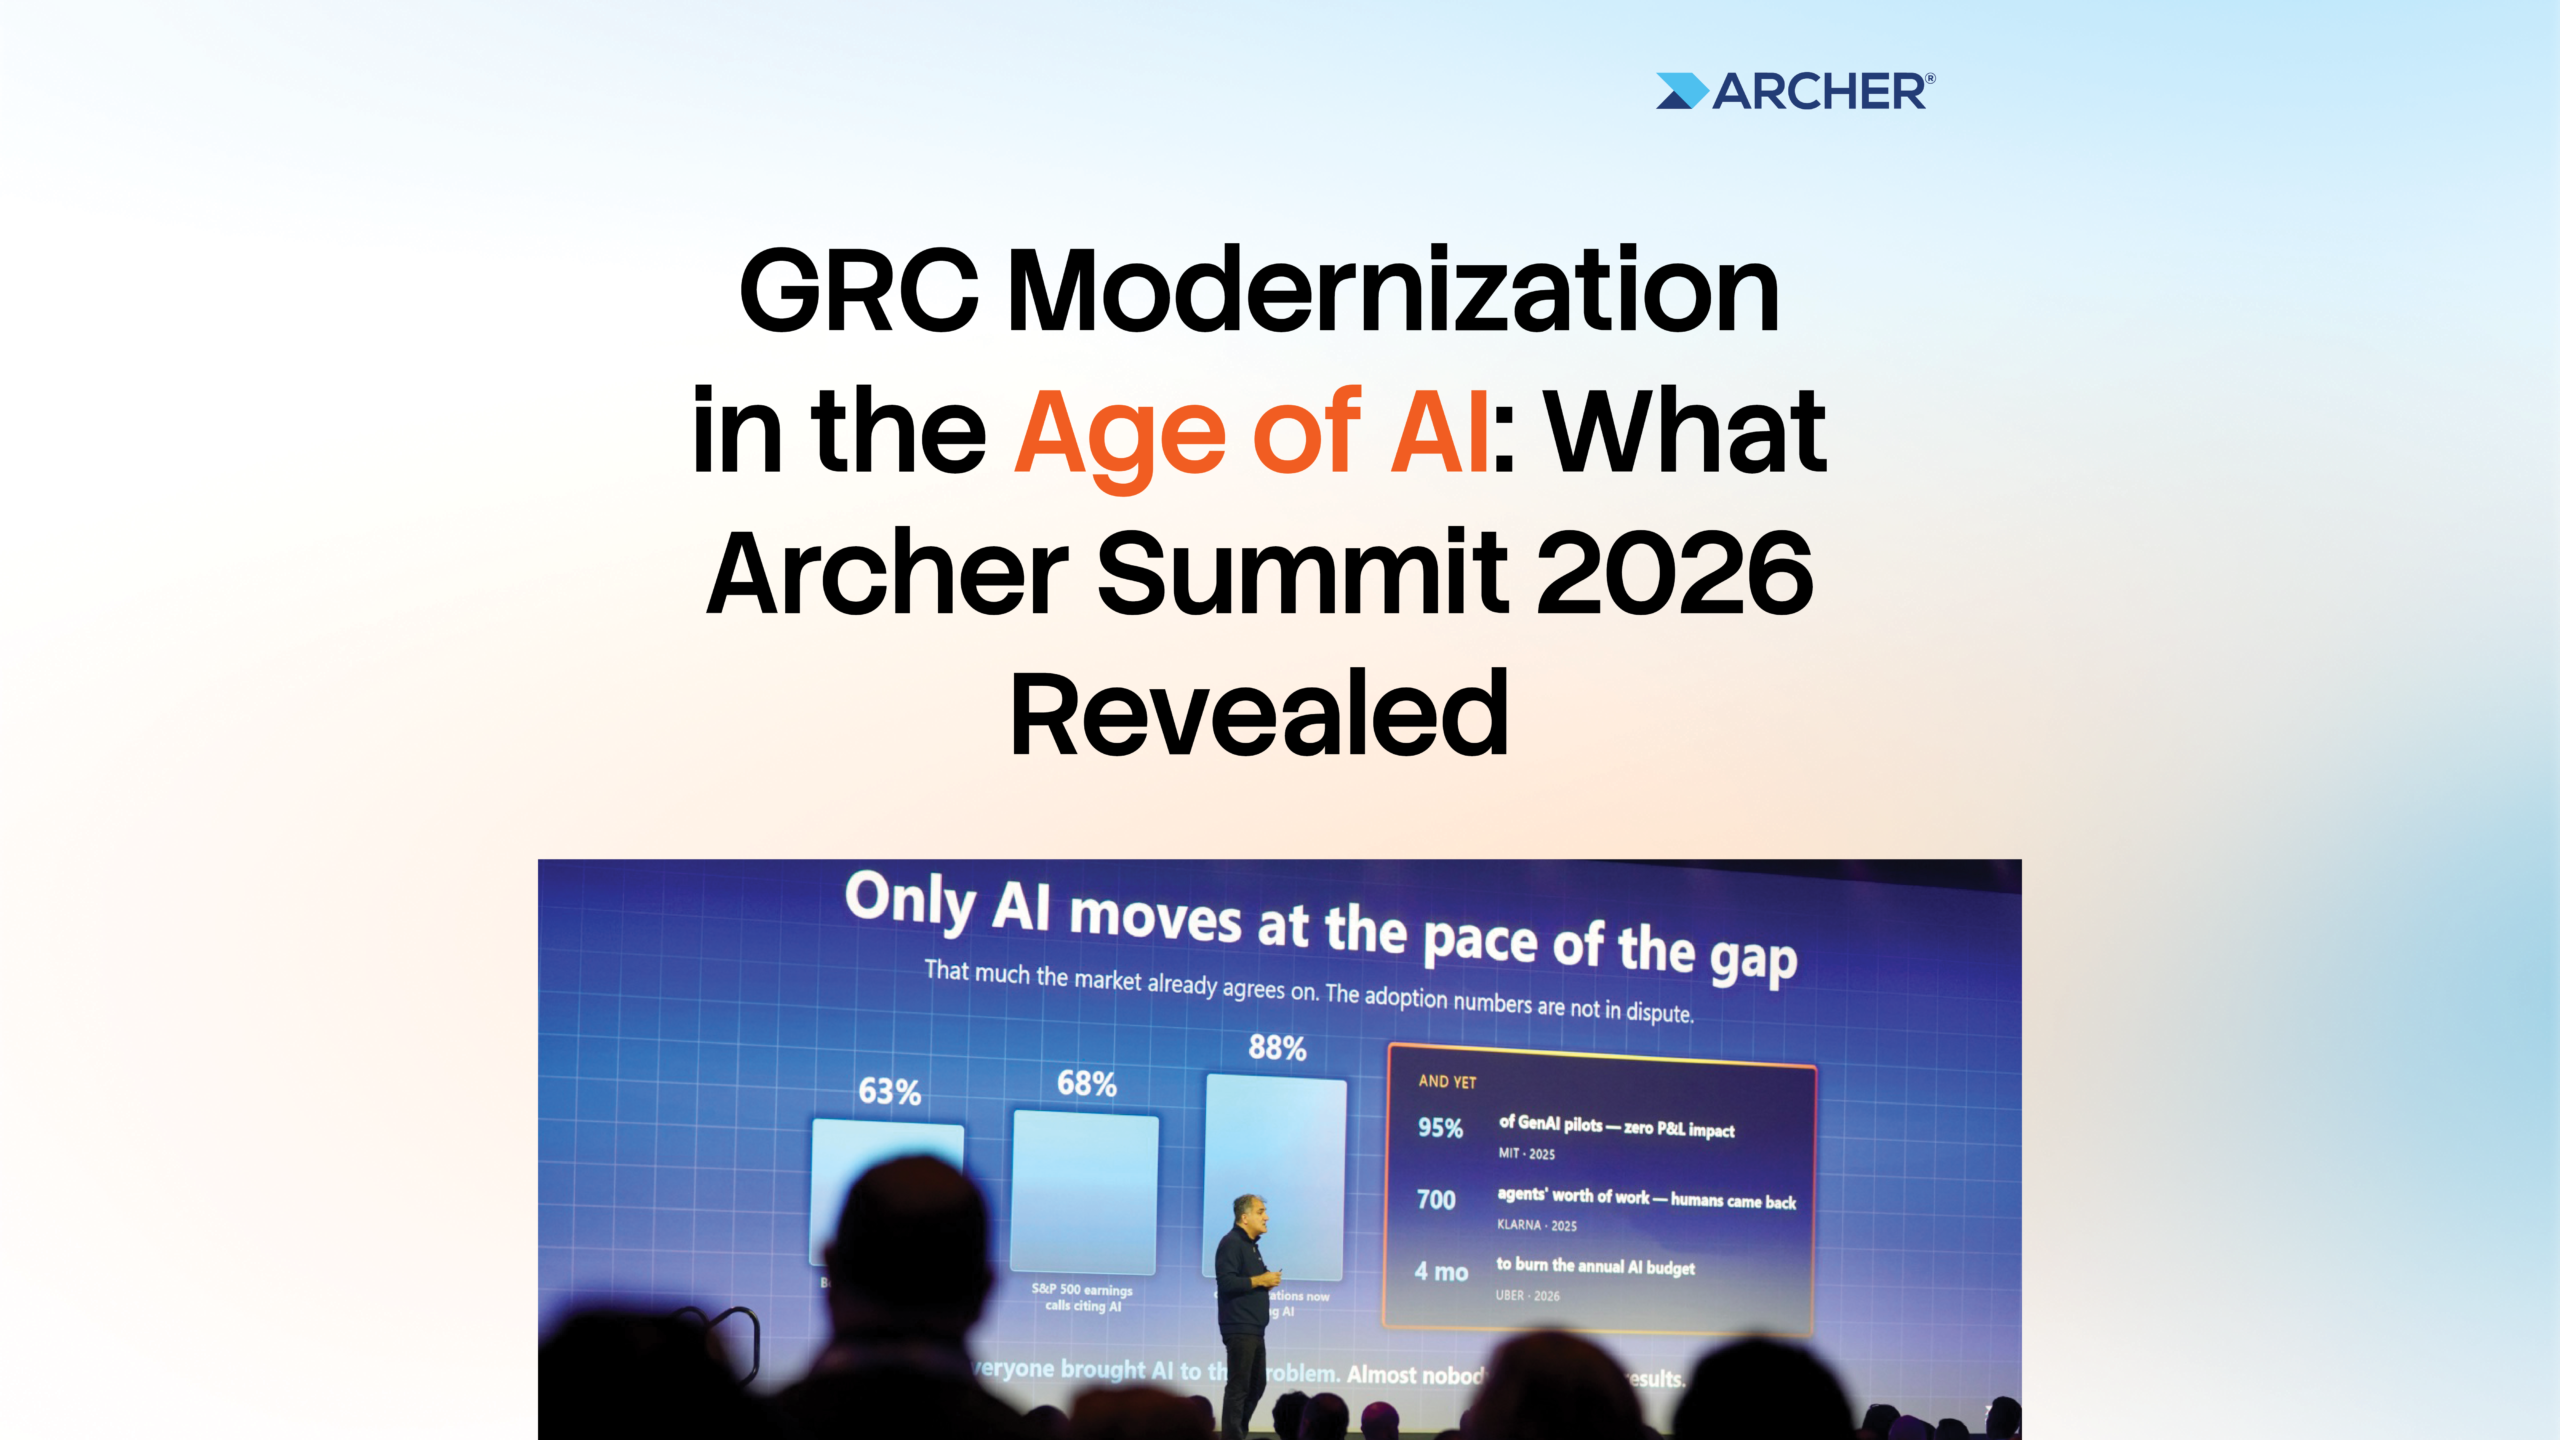
AI has been a major part of the conversation at Archer® Summit 2026, but by Day 3, the conversation had moved beyond what AI can do. The bigger question was…
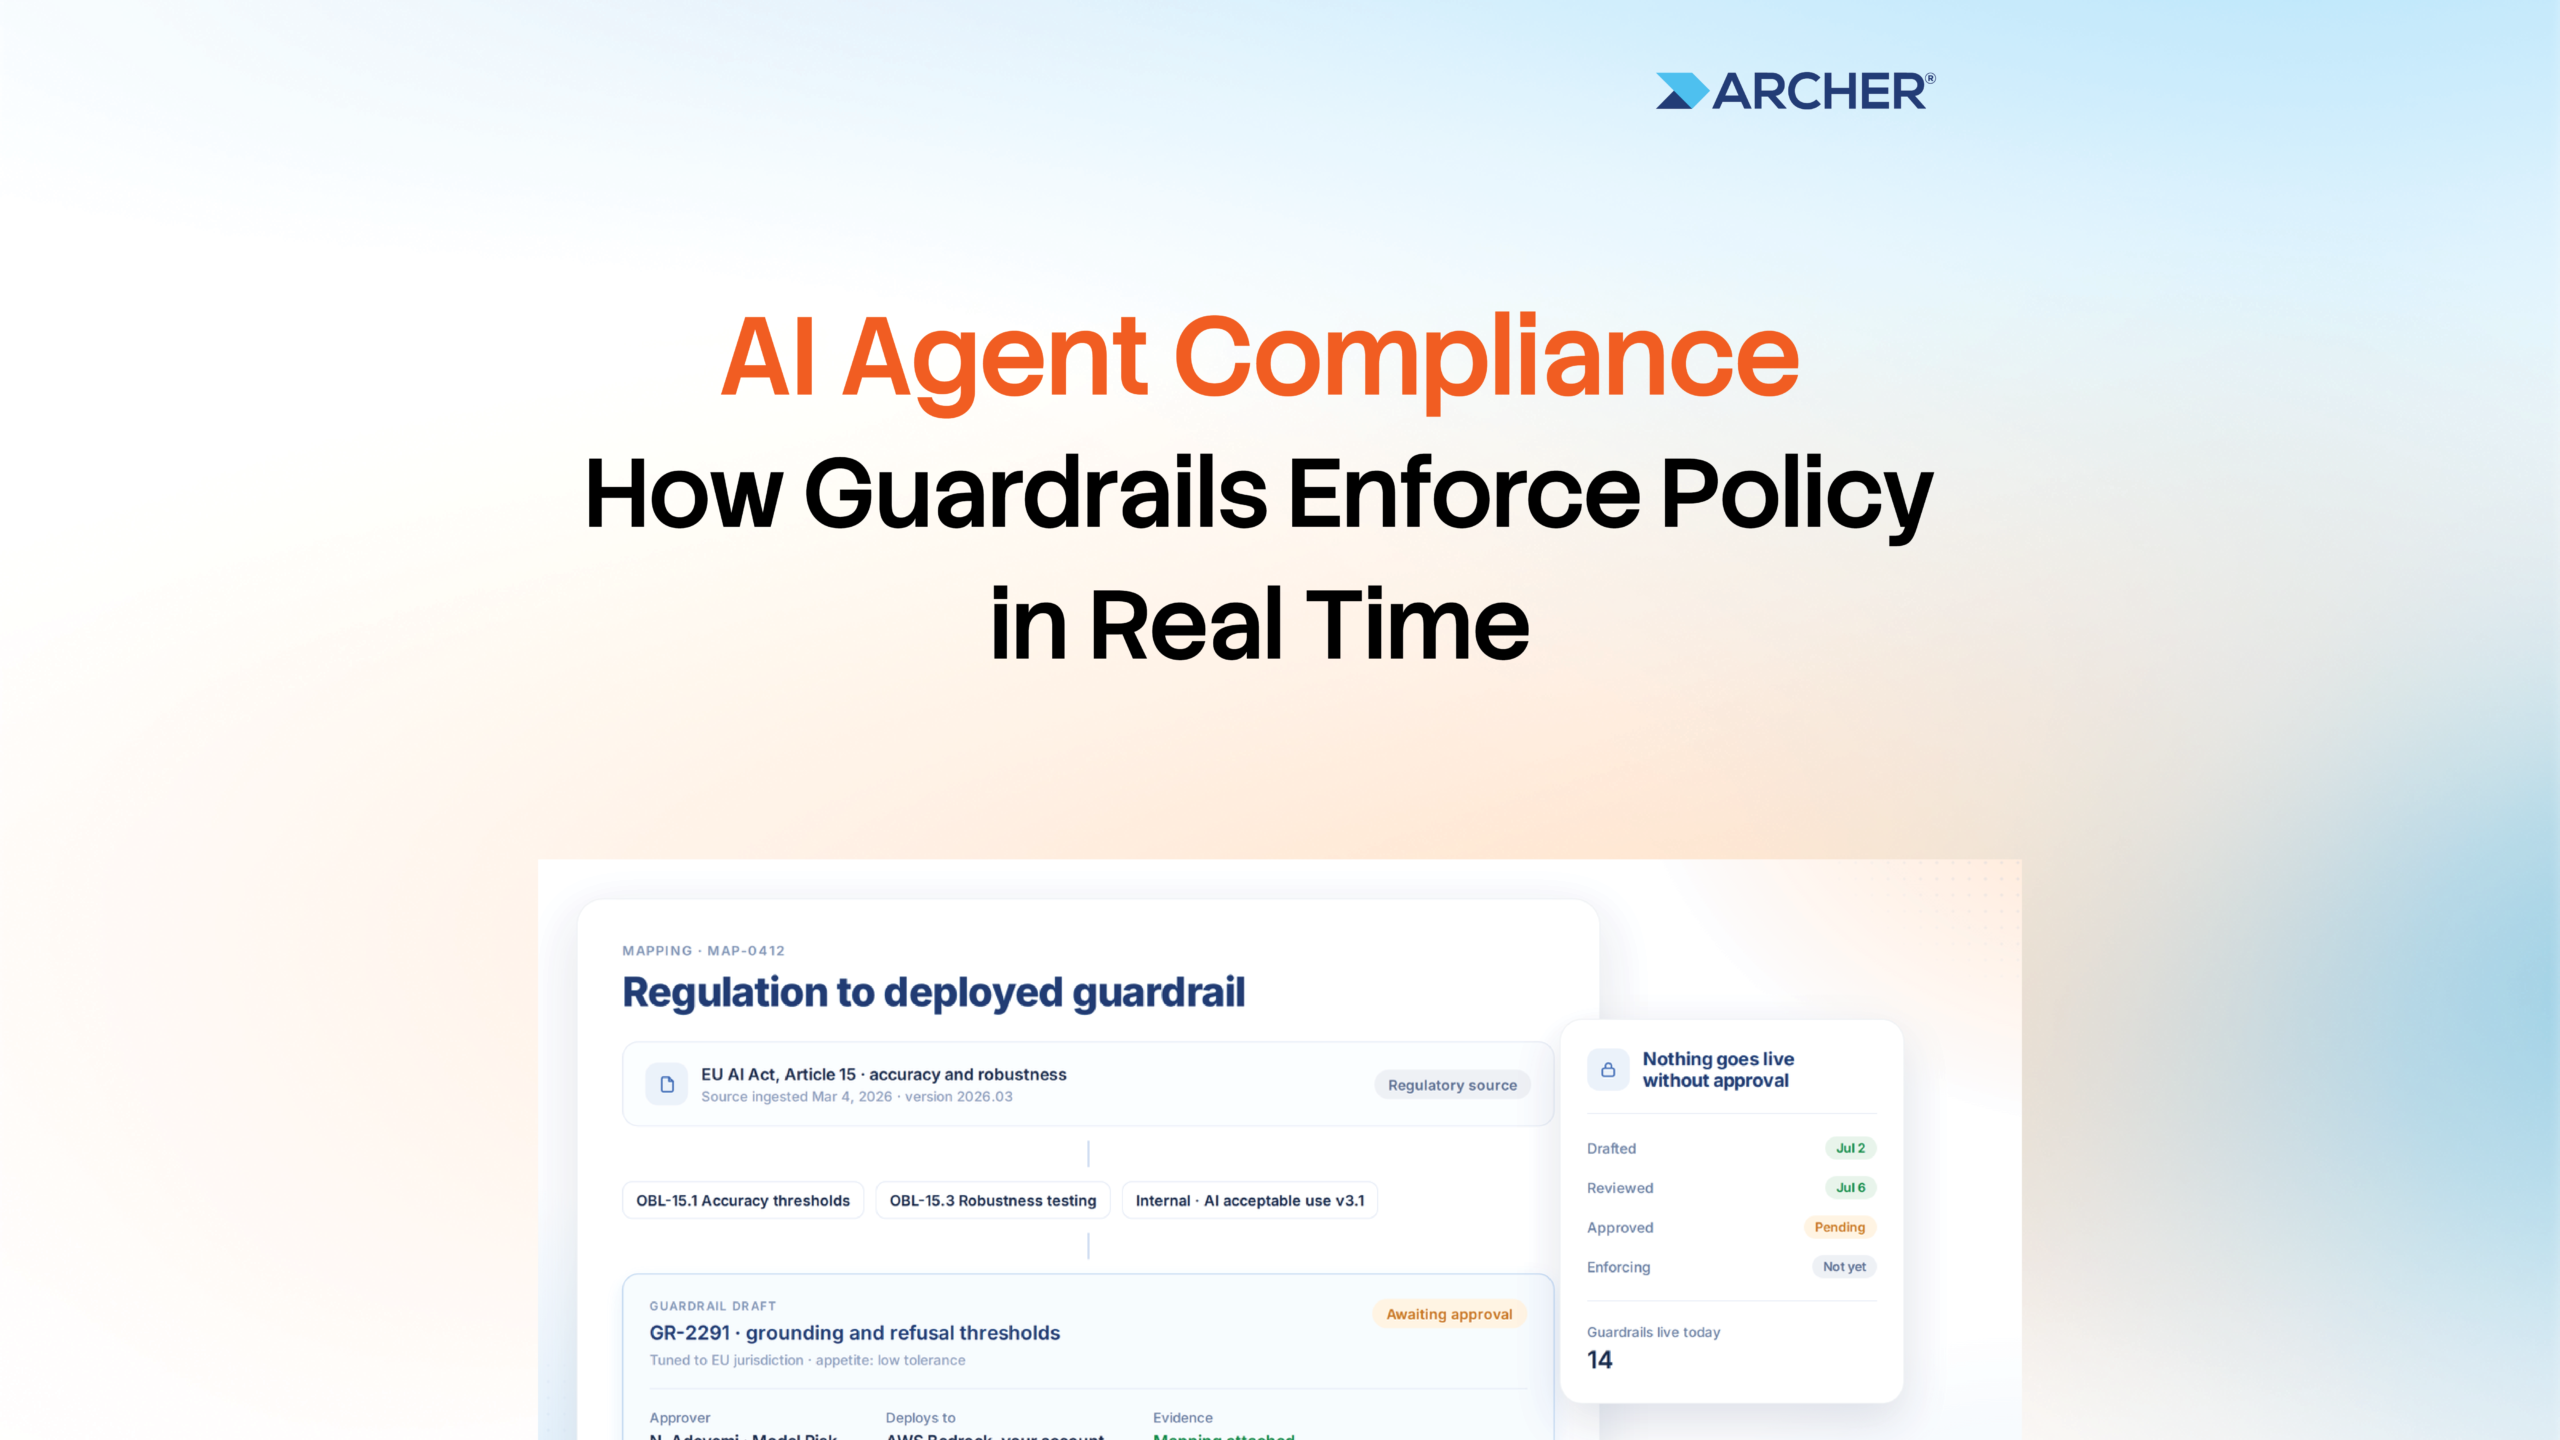
AI systems are increasingly acting on a company’s behalf, accessing systems, generating content and completing work at machine speed. Risk, compliance and security teams already own the policies governing much…
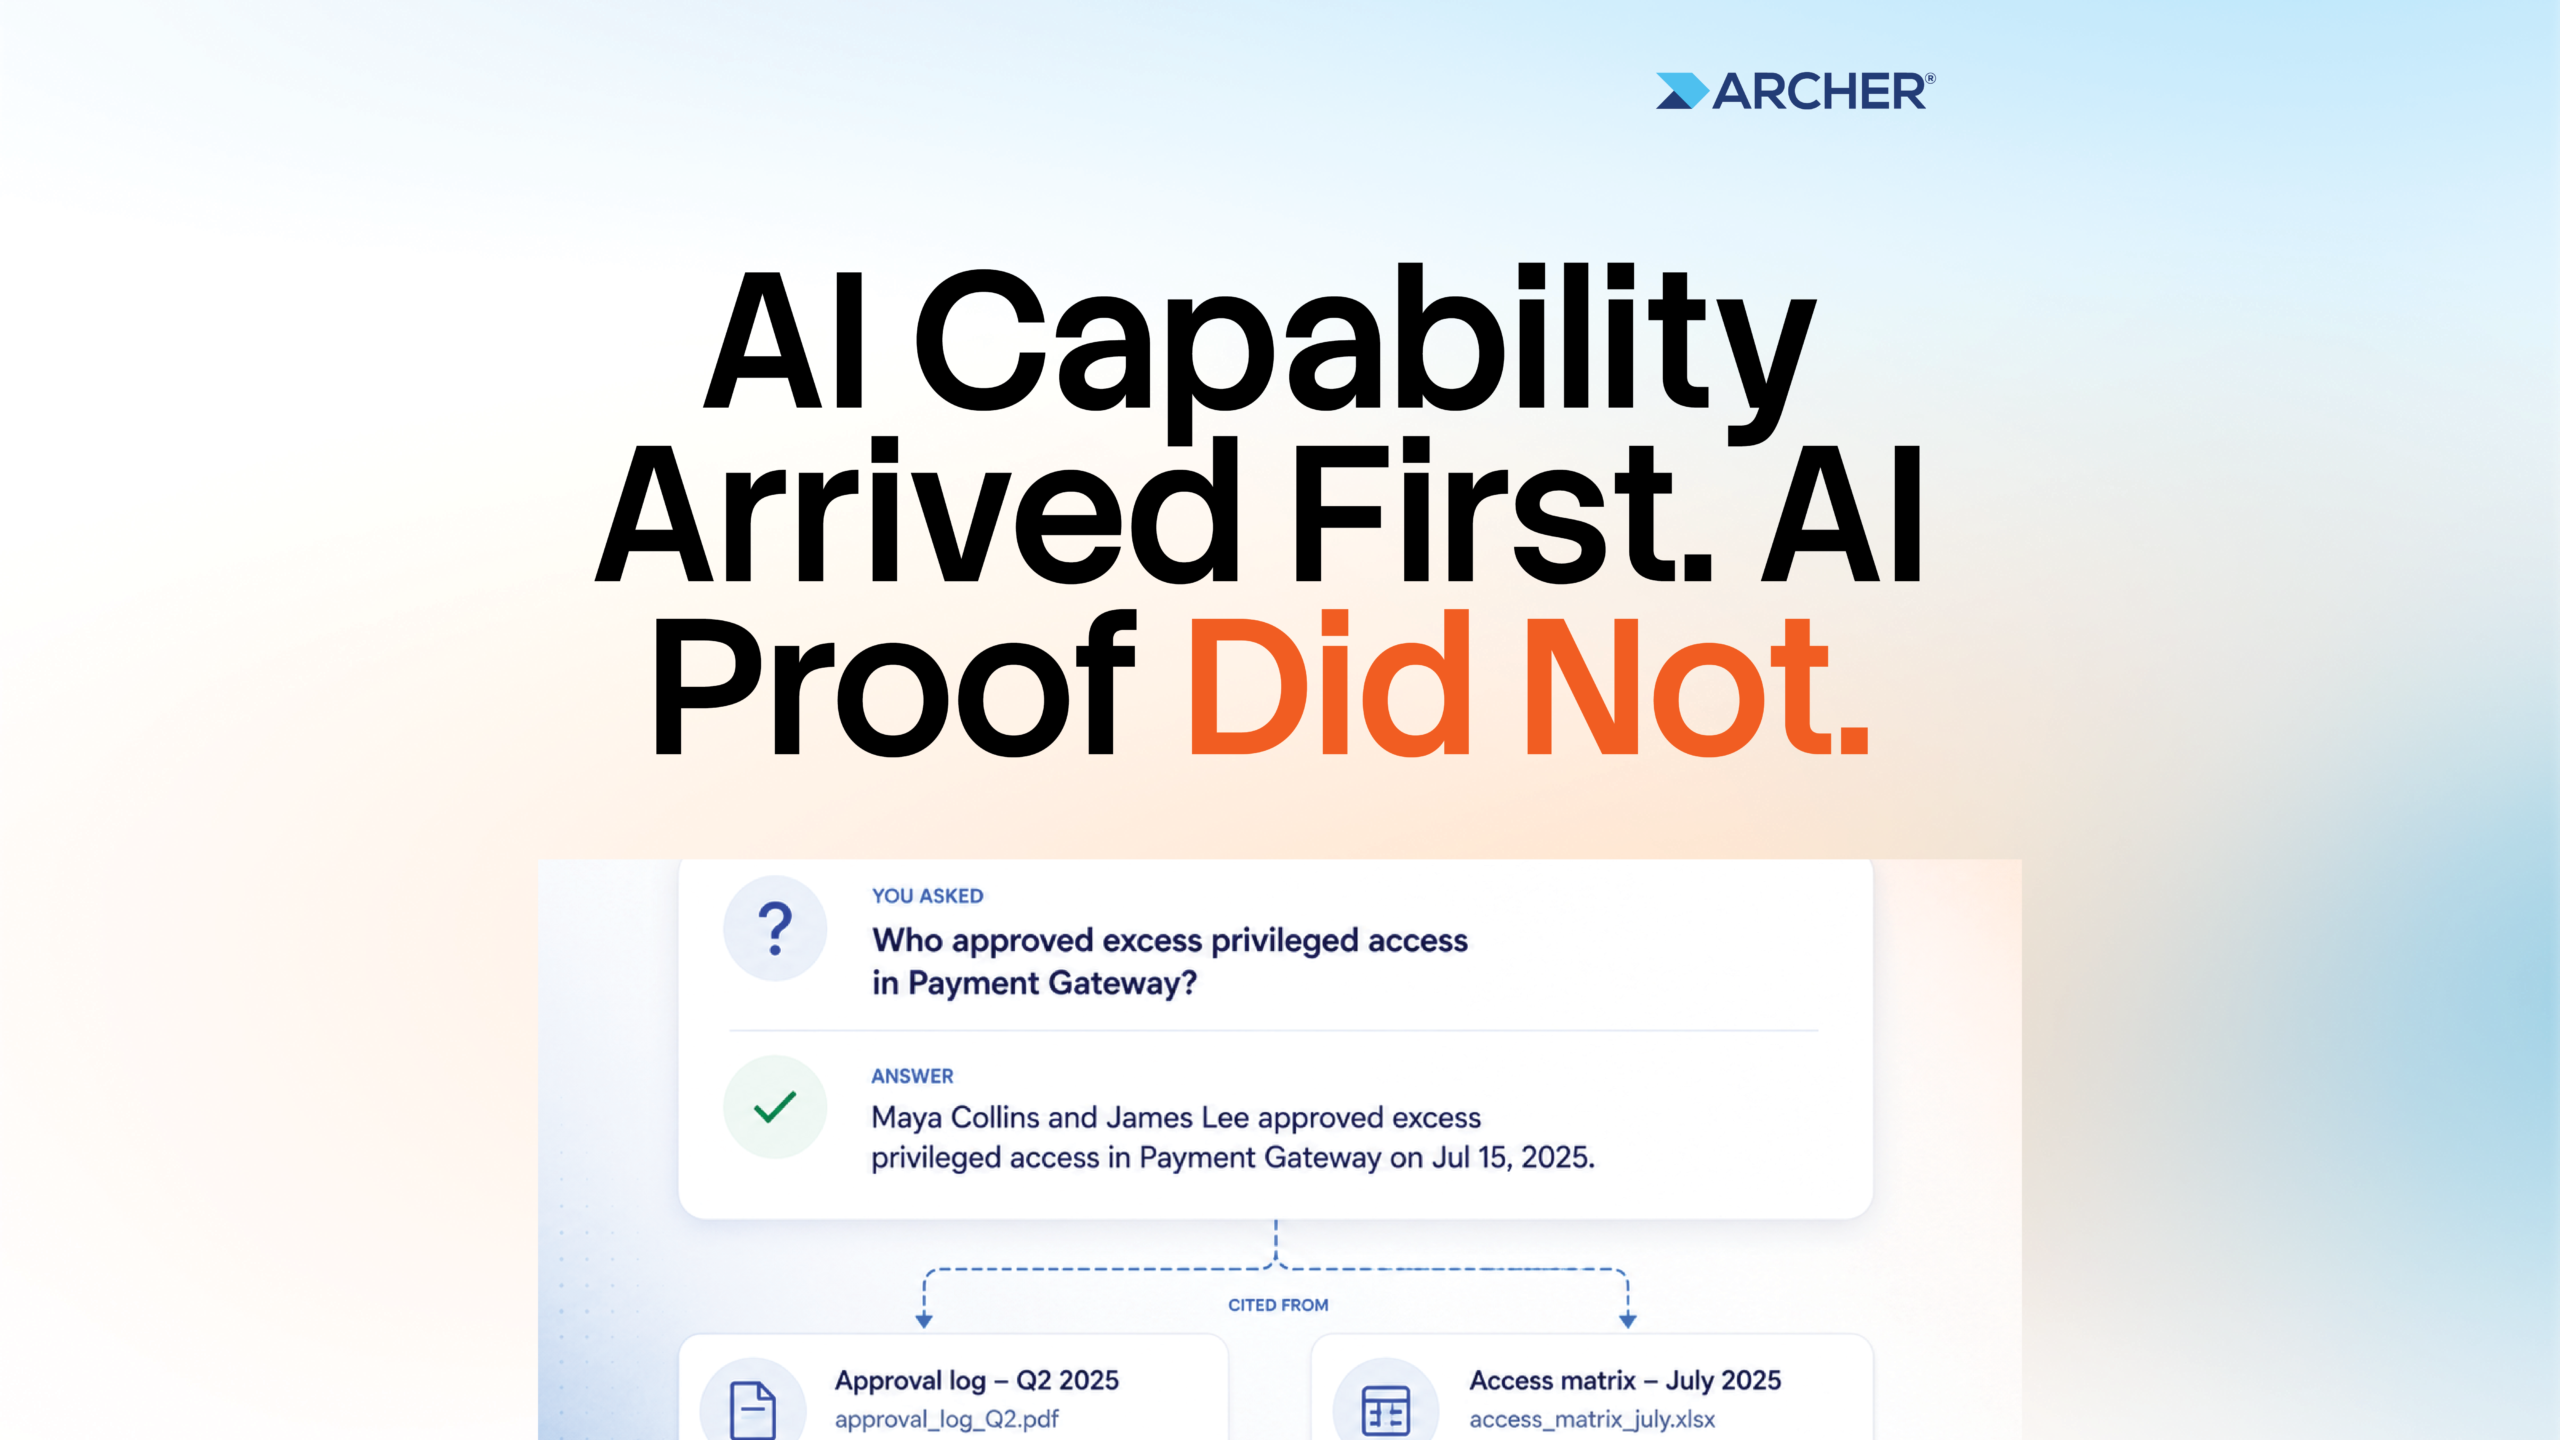
Built on proprietary models trained since 2017, Archer Evolv™ AI Operators are purpose-built digital full-time employees that work alongside risk, compliance and security teams, under their supervision, inside the GRC harness and…
The top-rated GRC software for companies in regulated industries combines continuous regulatory intelligence across jurisdictions, quantitative risk analytics, and unified cross-domain visibility in a single platform. For organizations operating in…
The Score that Matters Most to Archer Forrester published their latest Wave for governance, risk, and compliance platforms. Archer received the highest score possible in the Compliance Management criterion. A…
Authors: Sheila Khosrozadeh and Vinod Sreedharan The pace of business in 2026 leaves no room for static risk programs. Traditional GRC models struggle to keep up with modern systems and…